Your SOC 2 report landed on Vanta, and for a while that was the whole story. Then an enterprise prospect asks for ISO 27001, a healthcare customer wants a HIPAA attestation, and the next quote adds a second framework, an audit fee and a pen test as separate line items. That is usually the moment founders start searching for Vanta alternatives for startups, and it is the moment this guide is built for.
I compared nine platforms on one question: what does it cost, in money and in effort, to run two or three frameworks on a small team? This is the startup and multi-framework version of the comparison. If you want the broader "why people switch from Vanta" read, start with ComplyJet's general Vanta competitors guide, then come back here for the ranked shortlist.
Why Startups Outgrow a Single Framework (and Start Comparing Vanta Competitors)
Most startups buy compliance software for one reason: a customer asked for SOC 2. The first framework is easy to reason about. You pick a platform, connect your cloud accounts, pick an auditor, and wait for the observation window to close.
The second and third frameworks are where the platforms stop looking alike.
Here's the distinction most buyers miss: the headline price of a platform tells you almost nothing about what your second framework will cost. Some vendors price by framework, some by headcount, some by a quote that bundles the audit, and some by company with a framework package. Two platforms with the same sticker price for SOC 2 can be thousands of dollars apart once ISO 27001 and HIPAA are on the roadmap.
You can see the pattern on Vanta's own pricing page. Its Essentials tier lists "one compliance framework" as part of the package.
The four tiers (Essentials, Plus, Professional, Enterprise) carry no published dollar amounts, with pricing handled through a demo. Secureframe's published packages list a framework count of one on both its Fundamentals and Complete tiers. Neither is a flaw, and both are common. They simply mean that "how many frameworks do I need?" is the first question to answer before you compare any quote.
The effort side matters as much as the money. A well-mapped control, such as access reviews or encryption at rest, should satisfy SOC 2 and ISO 27001 once, with evidence reused. For the detail on how those two frameworks overlap, see ComplyJet's SOC 2 to ISO 27001 mapping guide. A platform that makes you re-collect that evidence for each framework quietly doubles your workload.
These are the complaints that recur in reviews and roundups of Vanta competitors:
- Modular pricing. The base plan covers one framework, and trust center, vendor risk and extra questionnaires arrive as add-ons.
- Audit and pen test billed separately. The software quote is not the compliance bill.
- Renewal surprises. Reviewers describe steep second-year increases. I could not verify a specific percentage from a primary source, so treat any number you read as an anecdote and ask for the renewal terms in writing.
- Contract flexibility. One small-business G2 reviewer, in an organic review from June 2025, wrote that Vanta "binds you to long term contract" and titled the review "Not for startups," while still crediting it with getting them to SOC 2. Another reviewer, on a small team of four or five people touching compliance, praised the integrations and said Vanta helped them map existing ISO controls to SOC 2 so they "weren't redoing work." That second review is flagged on G2 as incentivized, from a seller invite. Both are single data points, and I include both because the honest picture is mixed.
For a full breakdown of what Vanta itself costs, read ComplyJet's Vanta pricing guide and ComplyJet's Vanta reviews roundup. I won't repeat that here.
How I Evaluated These 9 Vanta Alternatives for Startups
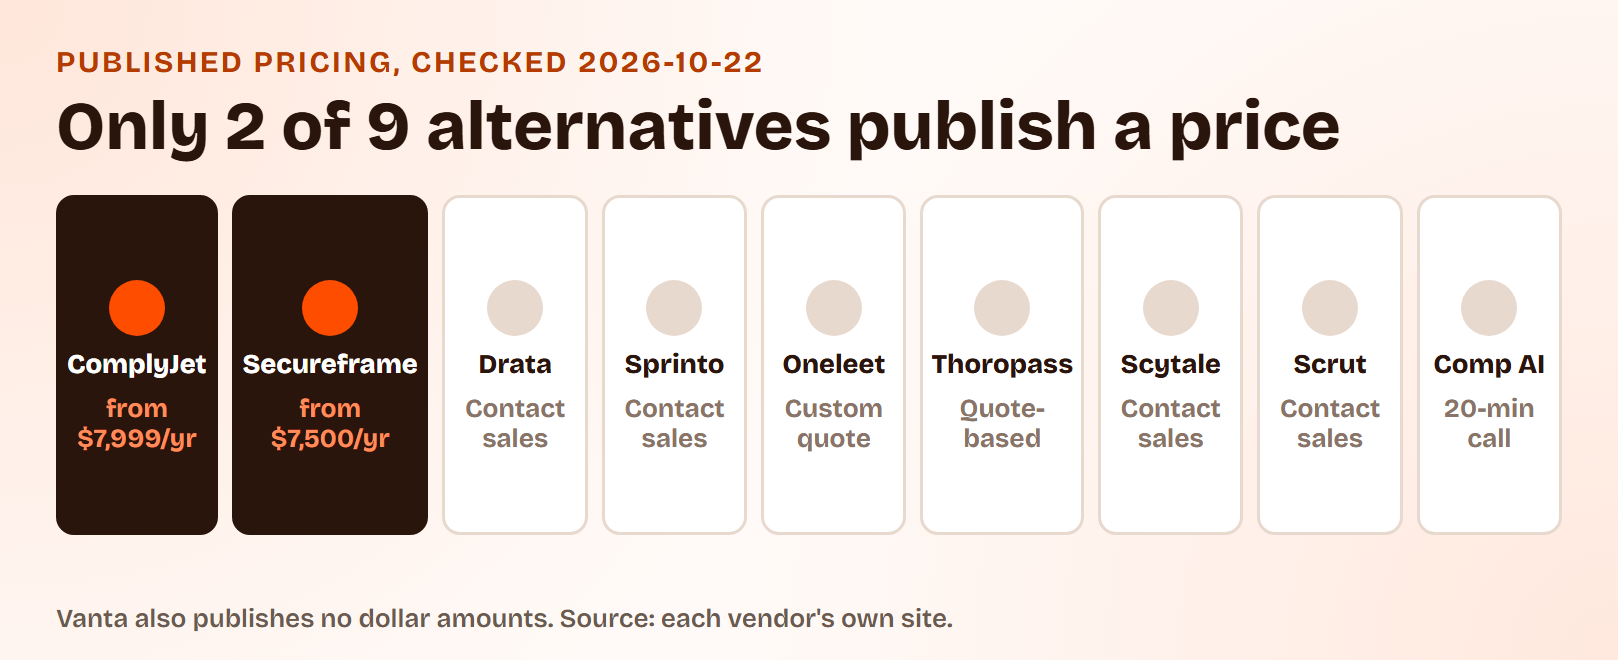
I reviewed nine platforms and scored each against the same criteria. All facts below come from each vendor's own website, checked on 2026-10-22. Where a vendor publishes no price, I say so and do not repeat third-party estimates, because those estimates conflict wildly between sources.
The criteria:
- Framework breadth and the cost of framework number two and three. Which frameworks are listed, whether custom frameworks are supported, and how pricing changes as you add one.
- Pricing transparency. A published number, a published starting price, or "contact sales."
- Audit model. Bring your own auditor, a partner network, or an audit bundled into the contract.
- Integration depth. The integration count the vendor states, and whether the number is consistent across its own site.
- Support model. Software access versus a team that drives the process.
- Fit for a team under 50 employees. Whether the vendor positions for startups, and what a small team gets.
- Independent review signal. Ratings shown, with their source named. I used a rating only where the vendor displays it or I read it on G2 directly.
A disclosure, because it matters: ComplyJet publishes this article and ranks itself first. The criteria above weight published flat pricing and guided delivery, which are things ComplyJet is designed around, and I won't pretend that is a coincidence.
To keep it honest, ComplyJet's entry has a real Cons list, and every other platform gets credit where it earns it. Drata is ahead of ComplyJet on brand recognition and framework count, and Vanta is ahead on integrations. You are reading a vendor's comparison, so verify the facts that matter to you on each vendor's site.
I did not rank Vanta itself. It is the baseline, and I cover where it still wins further down. Vanta is also the platform most readers already know, so I measure every alternative against what it publishes and what it leaves out.
Quick Comparison: 9 Best Vanta Alternatives for Startups at a Glance
| Tool | Best for | Pricing | Frameworks (vendor-stated) | Standout feature |
|---|---|---|---|---|
| ComplyJet | Startups under 50 employees running one to two frameworks | 3-year plan: Core $7,999/yr (1 framework package), Plus $9,999/yr (2 frameworks), up to 50 employees | 25+ including custom | Published flat per-company pricing with an external audit included |
| Drata | Funded teams with a security owner and broad framework needs | Contact sales | 30+ pre-built, 33 listed, plus custom | Largest pre-built framework library of the nine with a stated count |
| Secureframe | Teams wanting a published entry price and a wide framework list | Fundamentals starts at $7,500/yr; other tiers by quote | 35 listed, plus custom | Published starting price and 300+ native integrations |
| Sprinto | Lean cloud-native SaaS teams | Contact sales (Foundation and Growth tiers) | 25+ automated, 200+ "digitized" | Bring-your-own-auditor on the Growth tier |
| Oneleet | Security-minded startups wanting pentest and compliance together | One flat fee, quoted on request | SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, CIS IG1 and more | Manual pentest, vCISO and audit support in the fee |
| Thoropass | Teams wanting software and a licensed auditor in one relationship | Quote-based | SOC 2, ISO 27001, GDPR, PCI DSS, HITRUST, HIPAA and more | Platform plus in-house audit firm |
| Scytale | Teams wanting expert-led GRC services with the software | Contact sales | SOC 2, ISO 27001, GDPR, HIPAA, PCI DSS, ISO 42001 and more | Human experts alongside AI automation |
| Scrut Automation | Teams that need very wide framework coverage | Contact sales | 70+ | Large framework count and 150+ integrations |
| Comp AI | Engineering-led teams that value open source | Quoted on a 20-minute call | SOC 2, ISO 27001, HIPAA, GDPR and more | Open-source codebase, money-back guarantee |
Ratings, where a vendor shows one on its own site: ComplyJet 4.8/5, Drata 4.8/5, Oneleet 4.9/5, Scytale 4.8 on 700+ reviews. Vanta shows 4.5/5 from 2,859 reviews on G2.
Free Demo
Map your framework list to a published price
Want ComplyJet's published per-company pricing mapped to your framework list? Bring your Vanta quote and we will compare it line by line.
The 9 Best Vanta Alternatives for Startups in 2026
1. ComplyJet: Best Among Vanta Alternatives for Startups on Two Frameworks
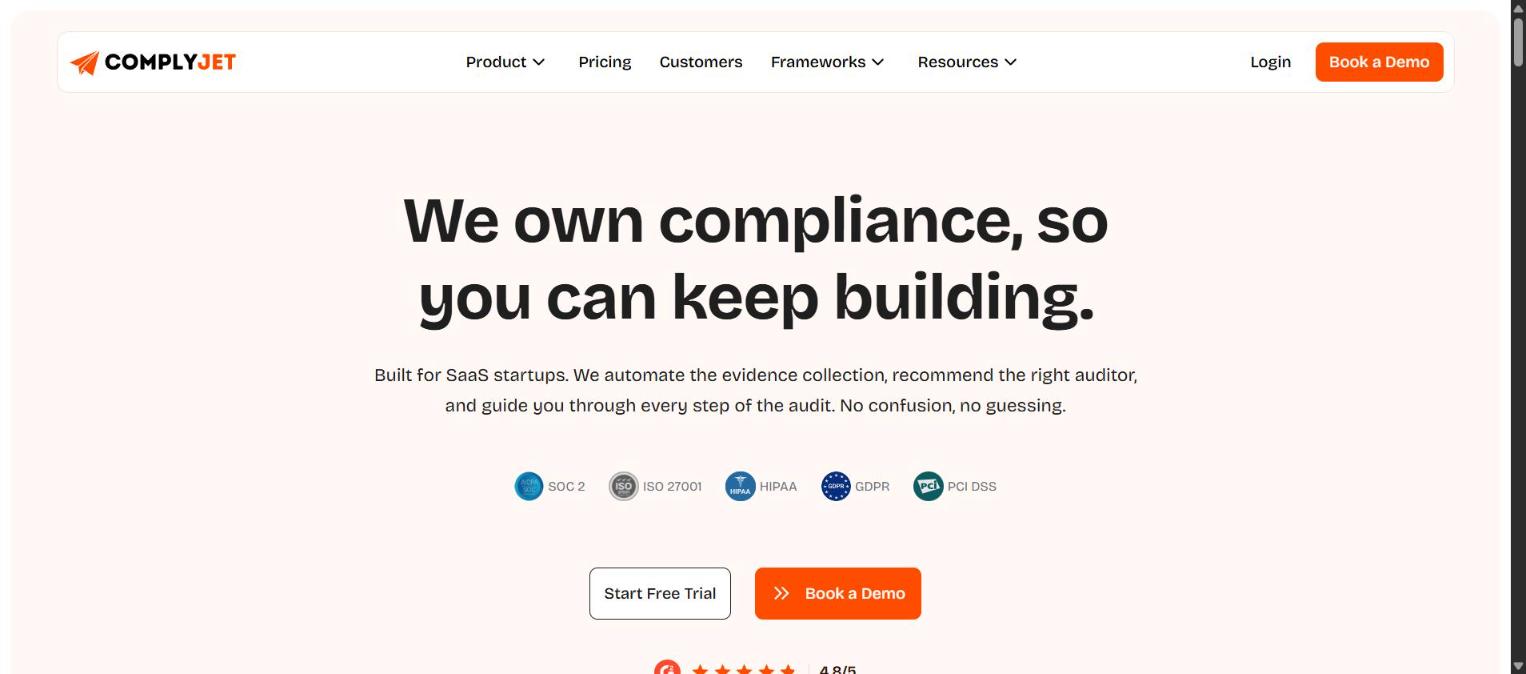
Screenshot of ComplyJet's homepage, captured 2026-10-22, for informational purposes only.
ComplyJet is built for SaaS startups doing compliance for the first time, often to close an enterprise deal. Its homepage describes it as software that automates evidence collection, recommends the right auditor and guides you through every step of the audit. That last part matters for a small team. You are not handed a dashboard and left to work out which controls apply to you.
The pricing model is the clearest difference from most platforms on this list. On its pricing page, the 3-year plan starts at $7,999/yr for Core (one framework package) and $9,999/yr for Plus (a two-framework package), both for companies up to 50 employees. Both include one external audit, implementation support and an internal audit.
The 1-year plan costs more, at $9,999 and $11,999, and prices are shown as "onwards," because the final number varies with the auditor you choose and add-ons like penetration testing, vCISO or managed services. A Custom tier exists for advanced and custom frameworks, vCISO and managed services.
For a startup adding a second framework, the two-framework Plus package is the point. SOC 2 plus ISO 27001, the most common pairing, sits in one plan, with one team working on both.
ComplyJet's hands-on support and clear guidance made SOC, GDPR, and ISO compliance surprisingly smooth. Suhas Manangi, Co-Founder & CEO, Precognition Labs (as shown on complyjet.com)
Key features:
- 25+ frameworks including custom frameworks, with SOC 2, ISO 27001, HIPAA, GDPR and PCI DSS on the homepage
- 350+ integrations
- Team-guided process: auditor recommendation and step-by-step audit support
- One external audit, implementation support and internal audit included in Core and Plus
- AI-assisted policy drafting and a Trust Center
Pros:
- Published pricing, with the plan and framework count visible before you talk to anyone
- Two frameworks in one flat per-company plan, with an audit included
- A team that works through the process with you, which matters most when nobody on staff has done an audit before
- G2 rating of 4.8/5 as shown on its homepage
Cons:
- Smaller company with less brand recognition than Vanta or Drata, which some enterprise buyers and auditors weigh
- Core covers one framework package and Plus covers two, so a startup running three or more frameworks moves to a Custom scope
- Fewer integrations than Vanta (400+), though 350+ covers the common startup stack
- Published plans are for companies of up to 50 employees, so a growing team will outgrow them
Pricing: 3-year plan: Core from $7,999/yr, Plus from $9,999/yr, up to 50 employees. 1-year plan: from $9,999 and $11,999. Custom tier quoted.
Best for: Startups under 50 employees pursuing one or two frameworks who want a published price and a team that drives the process.
Free Demo
See ComplyJet's two-framework plan in a real walkthrough
See how ComplyJet scopes SOC 2 plus ISO 27001 as one program, with the audit included. Book a demo and walk through your own framework list.
2. Drata: Closest Like-for-Like Swap Among Vanta Alternatives for Funded Teams
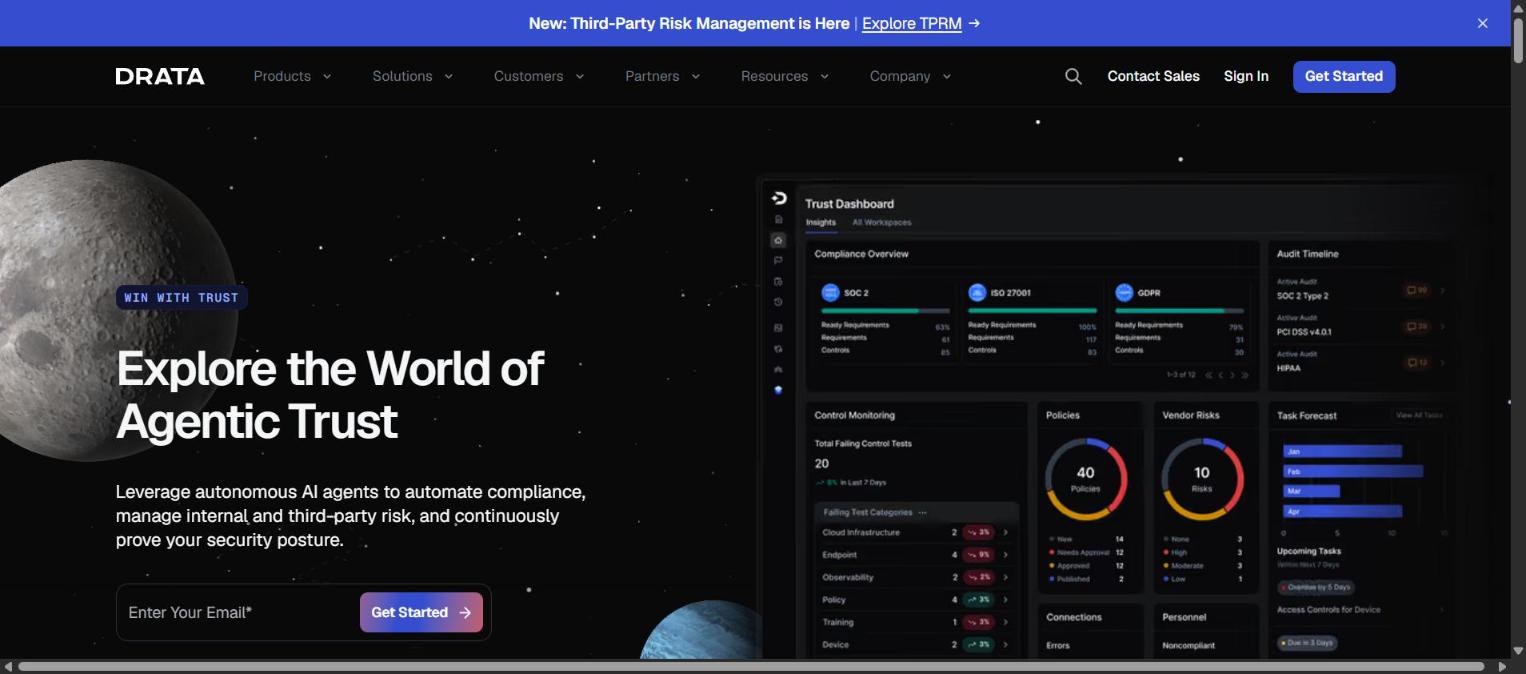
Screenshot of Drata's homepage, captured 2026-10-22, for informational purposes only.
Drata is the rival most often named alongside Vanta, and its homepage leans into scale. It reports 8,500+ global customers and a 4.8/5 G2 rating, and its frameworks page lists 33 pre-built frameworks, including SOC 2, ISO 27001, GDPR, HIPAA, PCI DSS, HITRUST, ISO 42001, NIST AI RMF and DORA, plus custom frameworks. Of the nine platforms, that is the broadest pre-built library with a clear number behind it.
Its homepage is explicit about the multi-framework use case: "Map once, reuse everywhere, and stay continuously audit-ready across multiple frameworks." It also has a stage-based section, with a Startup tier on the page describing automated evidence collection and framework roadmaps.
The trade-off is the buying process. Drata does not publish prices. Its pricing URL simply returns to the homepage, and it directs buyers to demos and contact sales. Drata's own blog, which ranks itself first for this query and covers ten vendors, also lists "pricing details available upon request" for every vendor it covers. Expect an enterprise-flavored sales motion. For a deeper look at Drata's rivals, see ComplyJet's Drata alternatives guide.
Key features:
- 33 pre-built frameworks plus custom frameworks
- Cross-framework control mapping, stated as "map once, reuse everywhere"
- Trust Center, questionnaire automation and third-party risk modules
- Startup, growth and enterprise positioning on its homepage
Pros:
- Widest pre-built framework library of the nine with a stated count
- Strong brand recognition with auditors and buyers
- Built-in cross-framework mapping
- G2 4.8/5 as shown on its site
Cons:
- No published pricing, so you cannot compare cost until you are in a sales conversation
- Positioned to scale into enterprise, which can mean more platform than a 15-person team needs
- Audit fees are separate from the software
Pricing: Not published. Contact sales.
Best for: Funded teams with a dedicated security owner who expect to add many frameworks over time.
3. Secureframe: The One Big-Name Alternative with a Published Starting Price
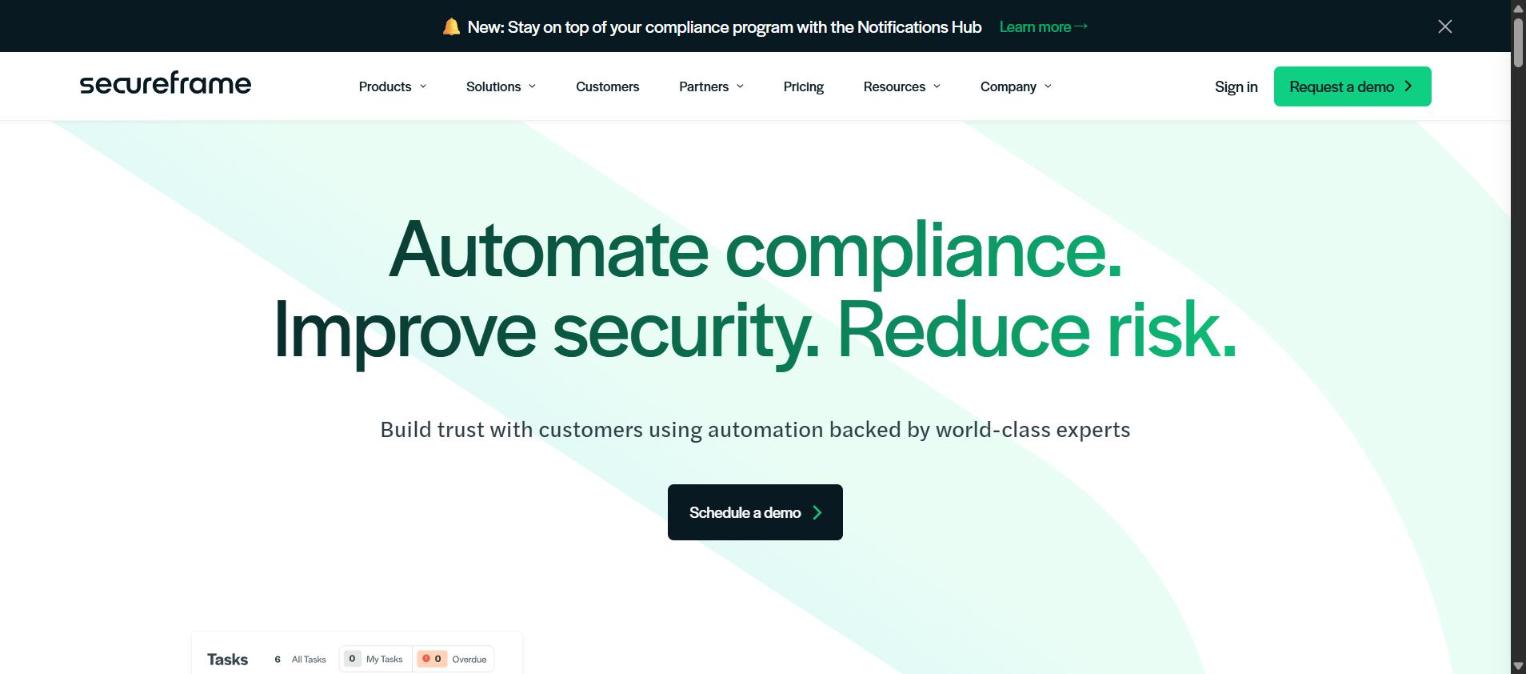
Screenshot of Secureframe's homepage, captured 2026-10-22, for informational purposes only.
Secureframe is the one larger platform here that publishes a number. Its packages page lists Fundamentals "starting at $7,500/year", with Complete and Defense (for CMMC) quoted on request. It lists 35 named frameworks plus custom frameworks: SOC 2, ISO 27001, PCI DSS, HIPAA, GDPR, CMMC 2.0, FedRAMP, NIST, ISO 42001, the EU AI Act and more.
Read the packages table carefully if you are multi-framework. The "Compliance Framework" line shows 1 for both Fundamentals and Complete.
In practice that means the base packages are scoped around one framework, and the cost of a second one is a conversation with sales. That is the exact question this guide tells you to ask any vendor. Both tiers include 300+ native integrations and access to the Secureframe Audit Partner Network, and Complete adds advanced third-party risk, access reviews, SSO and SCIM.
Secureframe's homepage cites case studies (Coda, Stream, PerkUp, Kinectify), but I did not find a named-person quote there, so I am not quoting one.
Key features:
- 35 named frameworks including federal (CMMC, FedRAMP, NIST) and AI frameworks (ISO 42001, EU AI Act)
- 300+ native integrations
- Audit Partner Network
- Trust Center, risk management and questionnaire automation tiers
Pros:
- A published starting price, which is rare at this scale
- Very wide framework list, including federal and AI frameworks
- Optional CMMC package
Cons:
- Packages list one framework each, so multi-framework pricing is quoted, not published
- Complete tier is where many useful features live (advanced access reviews, third-party risk, SSO), and it is quoted
- Not built around a team that walks a first-time startup through the audit
Pricing: Fundamentals starts at $7,500/year. Complete and Defense by quote.
Best for: Teams that want a published entry price and a very wide framework library.
4. Sprinto: Lean Cloud-Native Teams and Bring-Your-Own-Auditor
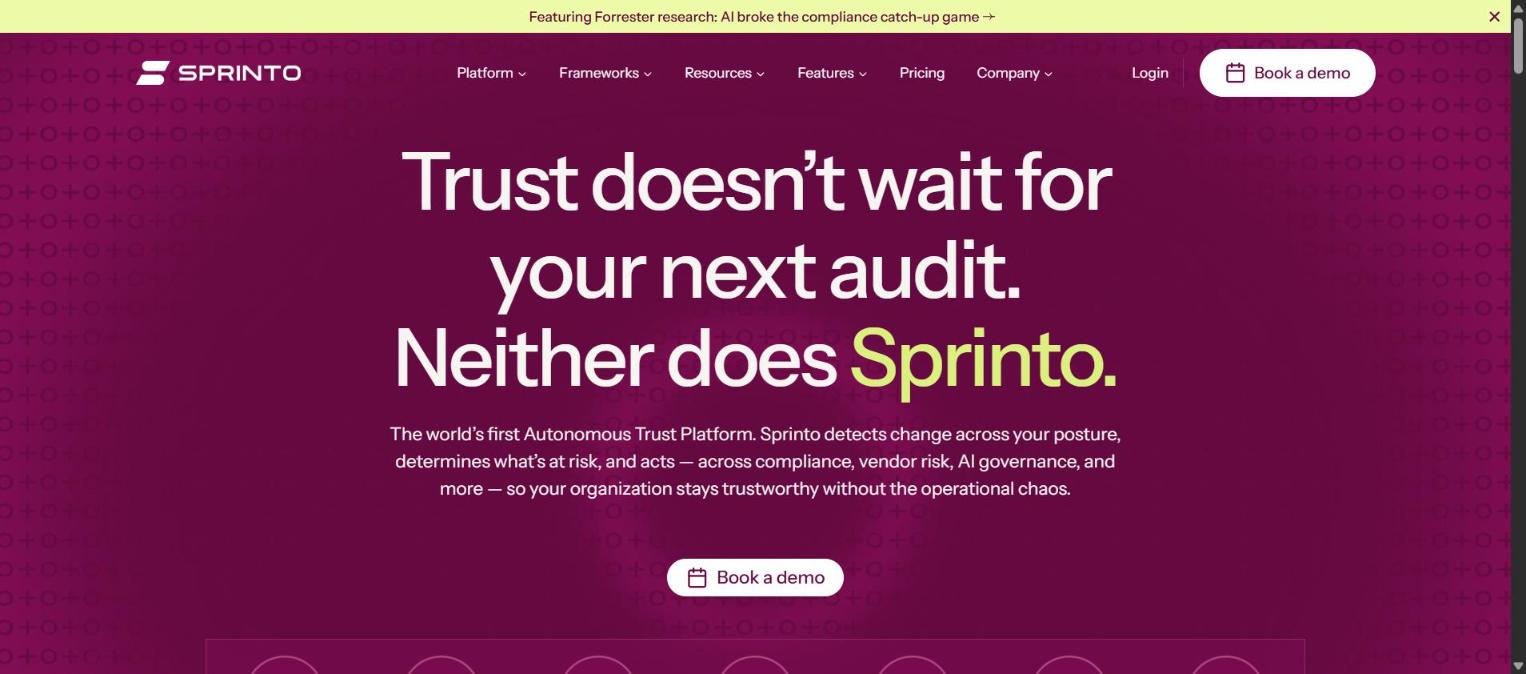
Screenshot of Sprinto's homepage, captured 2026-10-22, for informational purposes only.
Sprinto positions itself as an "Autonomous Trust Platform," and its pricing page splits into Foundation ("for startups on their first certification") and Growth ("for teams automating compliance"). Both are "Contact sales." Foundation includes 25+ frameworks automated out of the box, 200+ frameworks "digitized," continuous monitoring across 300+ integrations, audit planning, and "Sprinto network auditor access." The Growth tier adds bring-your-own-controls and bring-your-own-auditor along with programmable monitors and a dedicated customer success manager.
The 25+ versus 200+ split is worth reading closely. Sprinto's own page separates frameworks that are fully automated from those that are digitized, which I read as mapped rather than natively automated. That is a fair design. It means the "200+" figure is a breadth claim and "25+" is the number to compare against other vendors' automated frameworks.
Its frameworks page lists SOC 2, ISO 27001, PCI DSS, GDPR, HIPAA, NIST CSF, ISO 42001, TISAX, CIS, CSA STAR, CCPA, CMMC and more, and describes a common control framework: set up controls once, reuse across frameworks. For more on Sprinto's rivals, see ComplyJet's Sprinto alternatives guide.
Key features:
- Common control framework designed for reuse across frameworks
- 300+ integrations
- Built-in vendor risk, AI-assisted policies and a public trust center on the Foundation tier
- Bring-your-own-auditor on Growth
Pros:
- Explicit "build once, reuse everywhere" model for adding frameworks
- Startup-specific entry tier
- Bring-your-own-auditor available
Cons:
- No published prices on either tier
- Bring-your-own-auditor and custom monitors sit on the higher Growth tier
- Third-party sources I found give conflicting price estimates, so you cannot benchmark it without a quote
Pricing: Not published. Contact sales for Foundation or Growth.
Best for: Lean cloud-native SaaS teams that want a common control model across several frameworks.
5. Oneleet: Pentest and Compliance in One Flat Fee
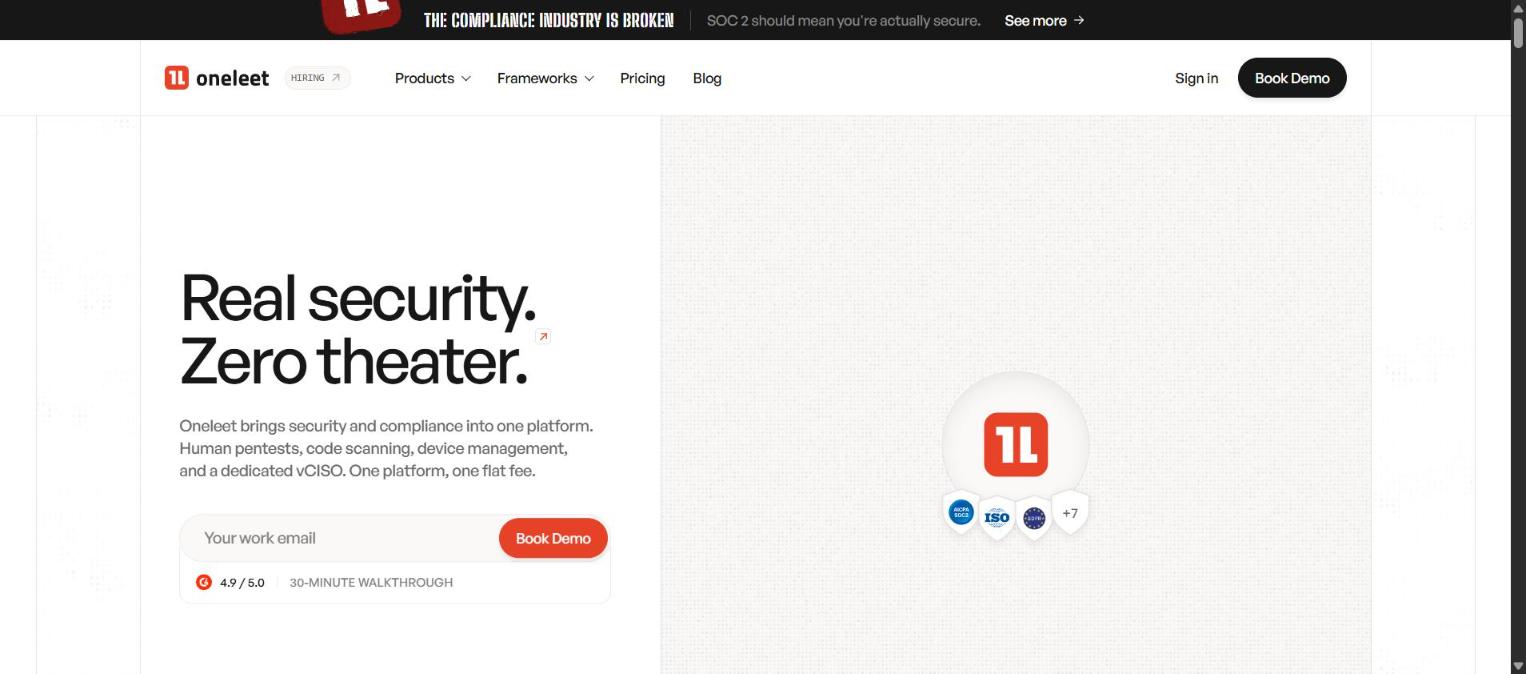
Screenshot of Oneleet's homepage, captured 2026-10-22, for informational purposes only.
Oneleet is the most security-heavy option here. Its homepage promises "human pentests, code scanning, device management, and a dedicated vCISO" with "one platform, one flat fee," and its pricing copy says "Every cost up front. Third-party fees quoted before you sign." Its pricing page lists SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, CIS IG1, DORA and NIST 800-171, plus custom frameworks, and its homepage shows a 4.9/5 G2 rating.
The bundle is the pitch. Where most platforms buy a pen test from a third party, Oneleet includes manual pentesting by its own testers.
For a startup that needs a pen test anyway to satisfy a customer, that can remove a separate vendor and a separate invoice. The homepage claims 300+ teams have migrated to Oneleet from Vanta, Drata and Secureframe, which is a vendor-stated figure I could not independently verify. For more on Oneleet's own rivals, see ComplyJet's Oneleet alternatives guide.
We chose Oneleet over Delve and Vanta. Andrew Rea, Taxwire (as shown on oneleet.com)
Key features:
- Manual pentest, code scanning, device management and vCISO included
- Audit support and a managed auditor relationship
- SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, CIS IG1 and more
Pros:
- Security work and compliance under one contract
- Costs described as up front, with third-party fees quoted before signing
- G2 4.9/5 as shown on its homepage
Cons:
- No prices published, only "request a quote"
- The page does not say whether the independent auditor's own fee sits inside the flat fee
- A security-services bundle is more than a pure compliance buyer may need
Pricing: One flat fee, quoted on request.
Best for: Security-minded startups that want pentest, vCISO and compliance from one vendor.
6. Thoropass: Software and a Licensed Auditor in One Contract
Screenshot of Thoropass's homepage, captured 2026-10-22, for informational purposes only.
Thoropass takes a different angle. Its FAQ says it is "a licensed auditor that delivers audits, supported by purpose built software." If you want one vendor accountable for both the platform and the audit, that is the cleanest version of it on this list. Its homepage lists SOC 2, ISO 27001, GDPR, PCI DSS, HITRUST and HIPAA, and its FAQ says it "is designed to support multi-framework audits" and maps overlapping controls across frameworks to reduce duplicate work.
That multi-framework claim is backed by customer language on the same page, for instance one customer describing how it "made it really easy to see both frameworks at a glance" for HITRUST and SOC 2. Pricing is quote-based, and its own site says price depends on the frameworks you pursue, audit scope, company size and the services you need.
One consideration: with the audit and the platform from the same company, you are choosing a bundled relationship. Some buyers like that, and some prefer a separate auditor. Neither is wrong, but know which you want before you sign.
We picked Thoropass because it provides an assessor and a platform. A lot of other companies have only a platform and bring in a third-party assessor. Thoropass is a one-stop shop, which makes things much easier. Chase Preston, Chief Operating Officer (as shown on thoropass.com)
Key features:
- In-house licensed audit firm plus an AI-powered platform
- Multi-framework audit support, including HITRUST
- Penetration testing offered
- Auditor collaboration inside the platform
Pros:
- One vendor for software and audit
- Strong fit for multi-framework programs that include HITRUST
- In-platform auditor workflow
Cons:
- Quote-based pricing with no published numbers
- Buying the auditor and the software from one company is a choice some teams would rather not make
- Less suited to a team that wants to pick its own auditor on price
Pricing: Quote-based.
Best for: Teams that want one vendor accountable for both the software and the audit.
7. Scytale: Human Experts Alongside the Automation
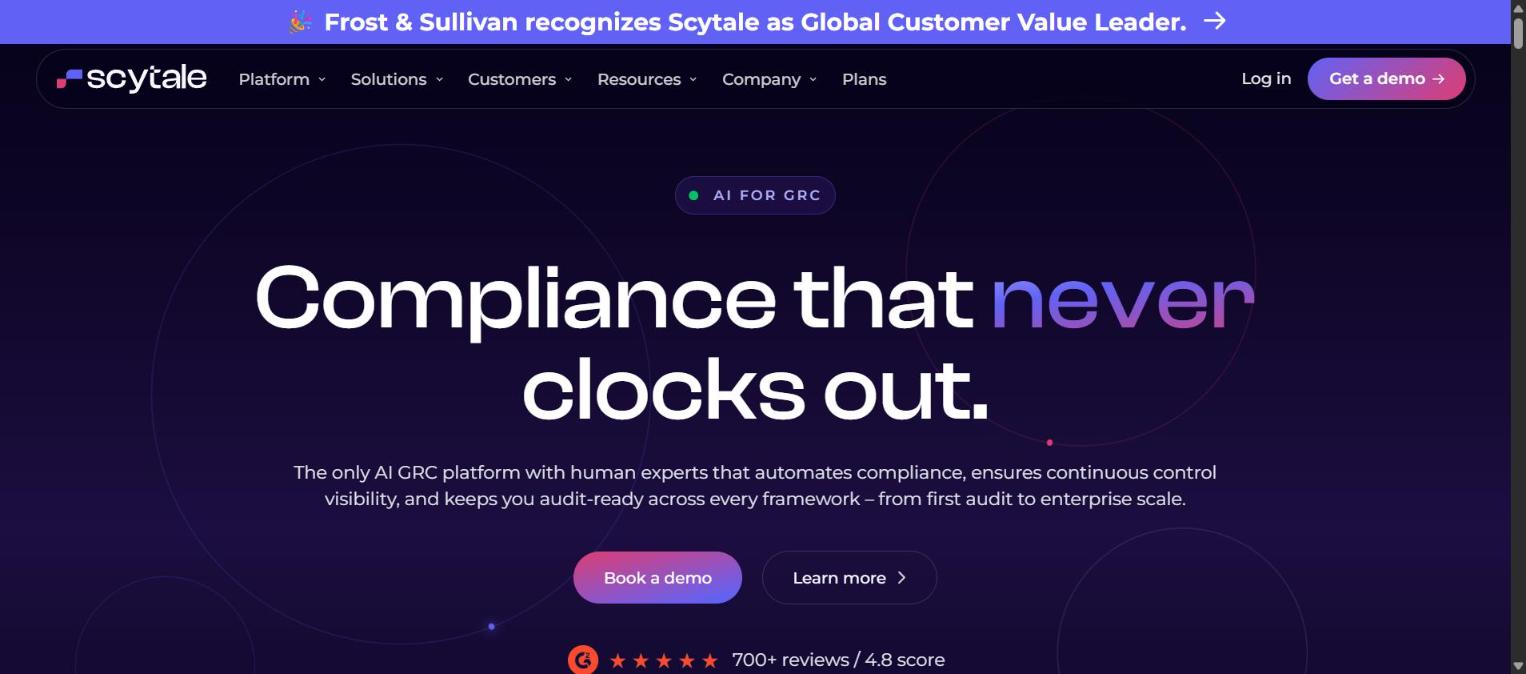
Screenshot of Scytale's homepage, captured 2026-10-22, for informational purposes only.
Scytale markets itself as "the only AI GRC platform with human experts" and shows a G2 rating of 4.8 on 700+ reviews on its homepage, the largest review count among the alternatives that display one. Its navigation lists SOC 2, ISO 27001, GDPR, HIPAA, PCI DSS, ISO 42001, SOX ITGC and CMMC, and it offers audit management and GRC expert services.
One thing to watch: Scytale's own materials give different framework counts. Its May 2026 blog says 80+ frameworks, while the footer on the same site says over 60. I would ask for the exact list you need rather than rely on either figure. I also could not find published prices.
Scytale gives us real-time visibility into compliance drift and automated detection of risks. Amit Levran, Head of Security, SundaySky (as shown on scytale.ai)
Key features:
- AI automation plus human compliance experts
- Audit management
- Broad framework list including SOX ITGC and CMMC
Pros:
- Services layer for teams without in-house compliance experience
- Large review base shown on its homepage
- Good fit for teams adding frameworks beyond security, such as SOX ITGC
Cons:
- Framework count inconsistent across its own pages
- No published pricing found
- Some advanced capabilities reportedly sit on higher tiers
Pricing: Contact sales.
Best for: Teams that want expert-led GRC support alongside the platform.
8. Scrut Automation: Breadth Across Many Frameworks
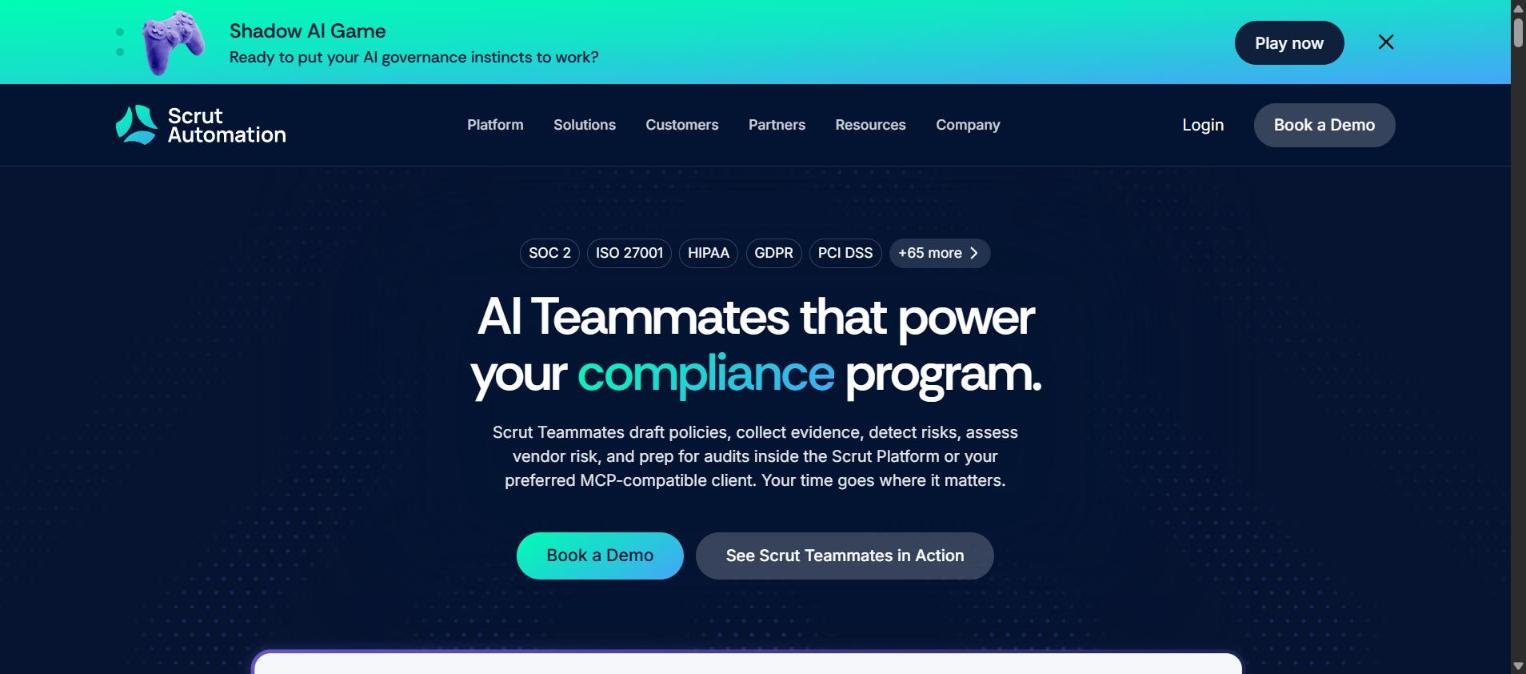
Screenshot of Scrut Automation's homepage, captured 2026-10-22, for informational purposes only.
Scrut leads with breadth. Its homepage shows SOC 2, ISO 27001, HIPAA, GDPR and PCI DSS followed by "+65 more," and states "70+ frameworks supported" and a connection to "150+ tools." That framework count is among the highest on this list, though its stated integration count is the lowest.
Its customer quotes are specific. One CEO says Scrut got their SOC 2 done within two months. Another security director says the ISO 27001 audit timeline was reduced by about four weeks. I found no published pricing, and the pricing URL I tried on its site returned a not-found page. For more on Scrut's own rivals, see ComplyJet's Scrut alternatives guide.
With Scrut, we got our SOC 2 done within two months, something we never could have finished on our own. Yichen Jin, CEO & Co-Founder, Fleak (as shown on scrut.io)
Key features:
- 70+ frameworks
- 150+ tool integrations
- AI teammates for policy drafting, evidence collection and vendor risk
Pros:
- Very broad framework coverage
- Named customer outcomes tied to real timelines
- Cost-savings calculator on its site
Cons:
- 150+ integrations is fewer than Vanta (400+), Secureframe (300+), Sprinto (300+) or ComplyJet (350+)
- No published pricing
- Fewer startup-specific cues than some others here
Pricing: Not published. Book a demo.
Best for: Teams that need wide framework coverage and are comfortable getting a quote.
9. Comp AI: Open Source and a Newer Vendor
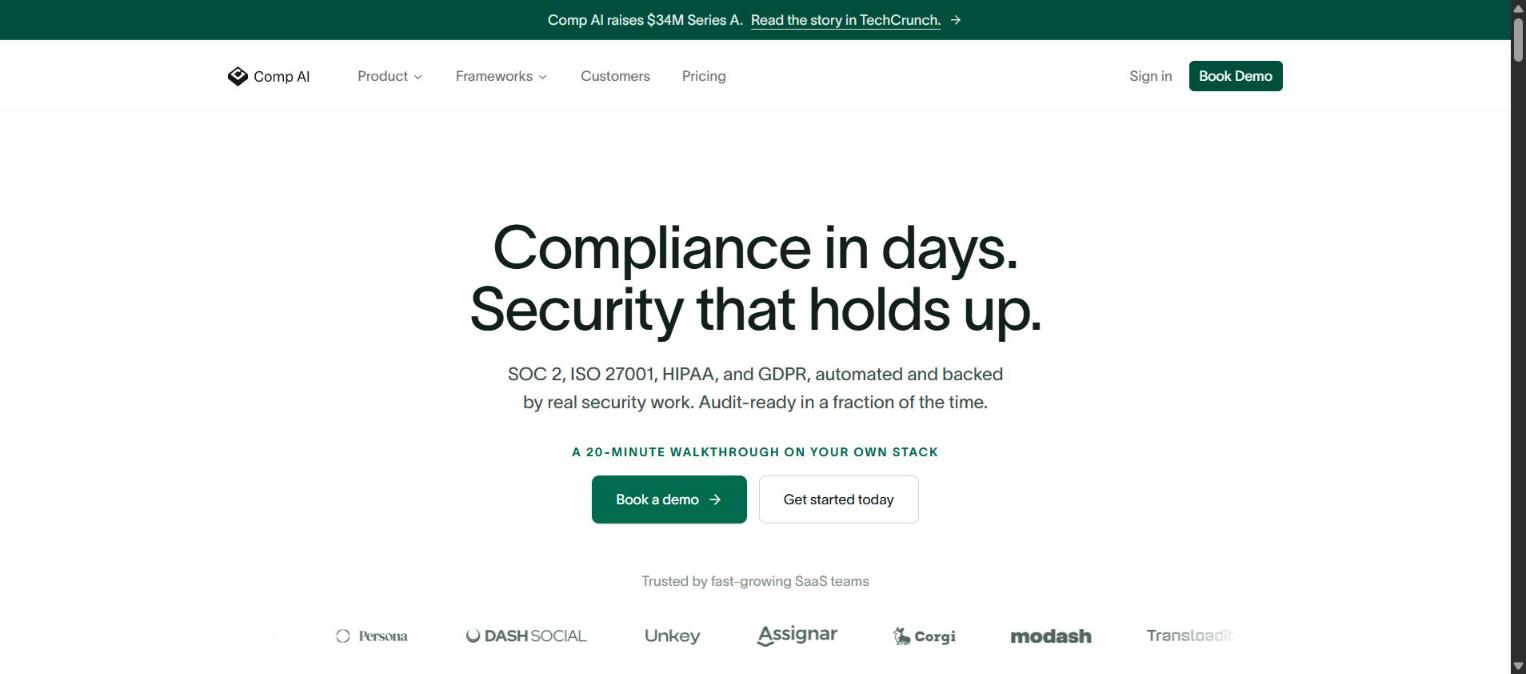
Screenshot of Comp AI's homepage, captured 2026-10-22, for informational purposes only.
Comp AI is the newest name here. Its homepage promises compliance in days and shows a banner that it raised a $34M Series A. It lists SOC 2, ISO 27001, HIPAA and GDPR on its homepage, and its pricing page lists more frameworks it quotes, including PCI DSS, SOC 1, NIST, ISO 42001 and FedRAMP. It describes itself as fully open source with a self-hostable codebase, and it advertises 580+ integrations.
Its pricing page is unusually direct about the multi-framework question: it says controls map across frameworks, so "adding a second framework costs less than starting one from scratch." It has no price list. It prepares an exact number for you on a 20-minute call, and it advertises a money-back guarantee. Whether audit fees are included depends on your scope, so ask. For a fuller look, see ComplyJet's Comp AI alternatives guide.
Key features:
- Open-source codebase and device agent
- 580+ integrations
- Pricing based on frameworks, headcount, timeline and audit needs
Pros:
- Open source, so you can inspect the code
- Explicit multi-framework pricing logic
- Money-back guarantee advertised
Cons:
- Young company with a shorter track record than the incumbents
- No published price list
- Audit and pen test inclusion depends on scope
Pricing: Quoted on a 20-minute call.
Best for: Engineering-led teams that value open source and want to see the code.
Where Vanta Still Wins Against Vanta Alternatives for Startups
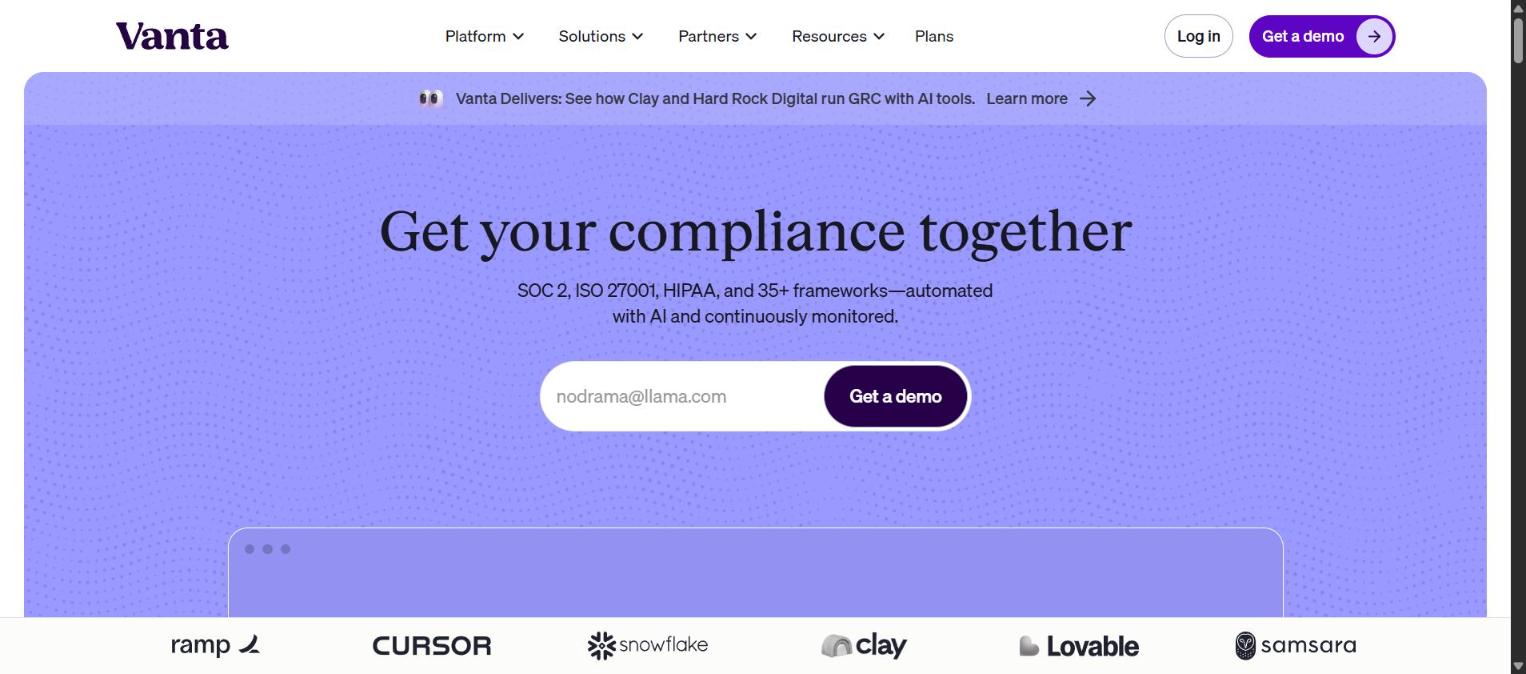
Screenshot of Vanta's homepage, captured 2026-10-22, for informational purposes only.
I ranked nine alternatives, and Vanta is still the reference point. Its homepage cites 35+ frameworks, its pricing page lists 400+ integrations, and it is the best-known name with auditors and buyers. It also lets you bring your own auditor and publishes its tier structure, even without dollar amounts. On G2 it shows 4.5/5 across 2,859 reviews, the largest review base I saw.
If you are funded, have a security owner, and your roadmap points toward enterprise customers, staying put can be the right call. Vanta's tier structure also scales upward cleanly, from Essentials to Enterprise, so you are unlikely to outgrow it. The same goes if you are mid-observation-window on a SOC 2 audit. Do not switch then (more on that below). Vanta also suits teams that need only one framework and are comfortable with the renewal terms they negotiated.
How to Choose Between Vanta Alternatives for Multiple Frameworks
Start with your framework list for the next 12 months, not just today. That is the heart of choosing among Vanta alternatives for multiple frameworks. A vendor that handles SOC 2 beautifully but quotes a new project for ISO 27001 will cost you more than the sticker suggests.
Vanta Alternatives Pricing: What a Second and Third Framework Really Costs
Ask every vendor the same five questions, in writing:
- Is the second framework a line item, or included in the package?
- Is the audit included? If so, how many?
- Are pen tests included?
- What changes at renewal?
- What happens when you pass 50 or 100 employees?
When you read about Vanta alternatives pricing, remember that competitor price ranges in third-party articles conflict with each other and are not verified, so do not benchmark off them. Use the published numbers (ComplyJet's plans, Secureframe's $7,500 starting price) as anchors, then get written quotes for the rest. For Vanta's own numbers, use ComplyJet's Vanta pricing guide.
A quick worked example shows why this matters. Take a 20-person SaaS company that needs SOC 2 this year and ISO 27001 next year. On ComplyJet's published 3-year plans, that is the Plus package at $9,999/yr, which covers two frameworks and includes one external audit.
On a platform whose published package is scoped to one framework, such as Secureframe Fundamentals at a $7,500/year starting price, the second framework is a quote you request later. I am not claiming one is cheaper overall.
The point is that the second price only appears if you ask for it, and you should ask before you sign the first.
Three mistakes come up repeatedly in this buying decision:
- Comparing only the first framework. The second one is where quotes diverge.
- Treating "supported" as "automated." A vendor can list a framework and still treat it as a manual mapping exercise. Sprinto's own split between 25+ automated and 200+ digitized frameworks is a useful reminder to read the fine print.
- Forgetting the audit. Your auditor's fee is usually a separate bill, and whether the vendor includes one, bundles one or leaves it to you changes the real cost.
Pick by Company Stage Among Vanta Alternatives for Startups
- Under 10 people, first SOC 2 for one enterprise deal. A published-price, guided option such as ComplyJet Core, or Secureframe Fundamentals, keeps things simple.
- 10 to 50 people, two frameworks. ComplyJet Plus, Sprinto Growth, Oneleet and Comp AI all quote against two frameworks. Compare what the audit includes.
- 50 to 150 people, GRC and vendor risk needs. Drata, Secureframe Complete, Scrut and Scytale are built for larger programs.
- Bring your own auditor or bundle it? Sprinto Growth, Vanta and Secureframe's partner network keep the auditor separate. Thoropass bundles one in-house, and ComplyJet and Oneleet manage the audit relationship for you.
How to Switch From Vanta Without Breaking Your Audit
Switching is easier than most people expect, if you do it in the right order:
- Export first. Pull your evidence, policies and control mappings before you cancel anything.
- Do not switch mid-observation window. If a Type 2 audit period is open, finish it, or confirm in writing with your auditor how evidence from a new platform will be treated.
- Ask how the new vendor ingests existing evidence. The answer tells you how much of your work carries over.
- Parallel-run if renewal is close. A few weeks of overlap costs less than a gap.
- Confirm auditor continuity. Keep the same auditor if you can.
ComplyJet also has a help article on switching to ComplyJet from Vanta, Drata or another platform.
Free Demo
Moving off Vanta without losing your evidence
Planning a move off Vanta? We will map your existing controls and evidence to ComplyJet's frameworks in the demo, so you know what carries over.
If you are still comparing, take the five pricing questions into every demo and judge each answer.
Free Demo
Get the plan and price for your framework mix
Tell us your two frameworks and your headcount, and we will show you the plan and price that fit, with no sales gauntlet.
FAQs About Vanta Alternatives for Startups
What Are the Best Vanta Alternatives for Startups?
The best Vanta alternative depends on your framework count and team size. For startups under 50 employees on one or two frameworks, ComplyJet and Secureframe publish prices and are worth a look first. For funded teams with a security owner, Drata is the closest like-for-like swap. Whichever Vanta alternative you shortlist, test it against your own framework list.
Is Vanta worth it for a small startup?
It can be. Vanta has the broadest integration list and the strongest brand with auditors. Its pricing page lists one framework in the entry Essentials tier and keeps prices behind a demo, so small teams should confirm the full cost, including add-ons and renewal, before signing.
How much does Vanta cost for startups?
Vanta does not publish dollar amounts. Its pricing page lists Essentials, Plus, Professional and Enterprise tiers and routes you to a demo for a personalized quote. ComplyJet's Vanta pricing guide covers what to expect.
Why do startups switch from Vanta?
The reasons that recur most are modular add-on pricing, audit and pen test fees billed on top, renewal terms, and contract flexibility. One small-business G2 reviewer described the contract as a long-term bind. Others value Vanta and stay.
Which Vanta Alternatives for Startups Support Multiple Frameworks?
Most on this list do. Drata lists 33 pre-built frameworks, Secureframe 35 and Scrut 70+. The better question is what the second framework costs, which varies by vendor. ComplyJet's Plus plan covers two frameworks in one flat per-company price.
Can you switch compliance platforms mid-audit?
You can, but it is risky during an open observation window. Finish the window or get your auditor's written agreement on how evidence from the new platform will count.
Is there a cheaper alternative to Vanta?
Published prices exist: ComplyJet's 3-year plan starts at $7,999/yr and Secureframe's Fundamentals at $7,500/year. Because Vanta does not publish its prices, a fair comparison needs a written quote from each vendor that includes the audit.
Do Vanta alternatives include the audit?
It varies. ComplyJet's Core and Plus plans include one external audit. Thoropass is itself a licensed audit firm. Oneleet includes audit support, and Sprinto and Vanta let you bring your own auditor. Always confirm whether the auditor's own fee is inside the price.
Final Thoughts on Vanta Alternatives for Startups
If I had to boil this down, it is three questions. How many frameworks will you run in the next 12 months? Do you want to buy software or an outcome? And how much of the audit do you want one vendor to own?
For a startup under 50 people on one or two frameworks, I ranked ComplyJet first for its published flat pricing and guided delivery, and I have listed its limits above so you can judge for yourself. For funded teams with a security owner and a long enterprise roadmap, Drata and Vanta remain strong. For security-heavy needs, Oneleet and Thoropass bundle more. Wherever you land, get written quotes and ask the five pricing questions above.
My suggested shortlist process is simple. Pick two platforms from this list that fit your stage, add Vanta as the baseline, and put the same framework list and headcount in front of all three. Ask each for the second-framework price, the audit terms and the renewal terms in writing, then compare the answers side by side.
The platform that answers those three questions plainly, before you have signed anything, is usually telling you something about how the relationship will go afterward. Treat a vague answer as an answer. If a vendor will not put the second-framework price in writing before you sign, you have learned what the renewal conversation will feel like. Give yourself two weeks for this comparison, and do not let a quarter-end discount shorten it.
Free Demo
Bring your Vanta quote and compare it line by line
Book a free demo and bring your Vanta quote. We will compare it with ComplyJet's published plans line by line.
Related Reading on Vanta Alternatives for Startups
- Top Vanta competitors and alternatives, the general guide to why teams switch and when it makes sense.
- Vanta pricing guide, for what Vanta costs and what drives the quote.
- Best SOC 2 compliance software, the ranked comparison for SOC 2 alone.
- SOC 2 to ISO 27001 mapping, for how one control can serve both frameworks.
Sources: Framework counts, integration counts and pricing statements come from each vendor's own site, checked 2026-10-22: ComplyJet pricing, Vanta pricing, Drata, Secureframe pricing, Sprinto pricing, Oneleet pricing, Thoropass, Scytale, Scrut, Comp AI pricing. Review quotes and the 4.5/5 Vanta rating come from Vanta's G2 reviews, read 2026-10-22.