Your auditor's request list lands in your inbox, and it is a spreadsheet with 200 rows. Access reviews, change tickets, control walkthroughs, evidence screenshots. Half of it lives in a shared drive nobody owns, the other half is in someone's head.
It is your first SOX year, or the year before your IPO when the auditors start asking the same questions on a dry run, and someone on the finance team says the words every SOX owner eventually says: we need software for this.
So you search for the best SOX compliance software and expect a clean ranked list.
What you get is a strange mix. Vendor-written roundups that rank the vendor first. Lists that put a checklist app next to a Fortune 500 controls suite. Names you know from SOC 2 shopping sitting beside names you have never heard of. None of it tells you the thing that actually decides the purchase: "SOX software" is not one market, and picking from the wrong one costs you a year.
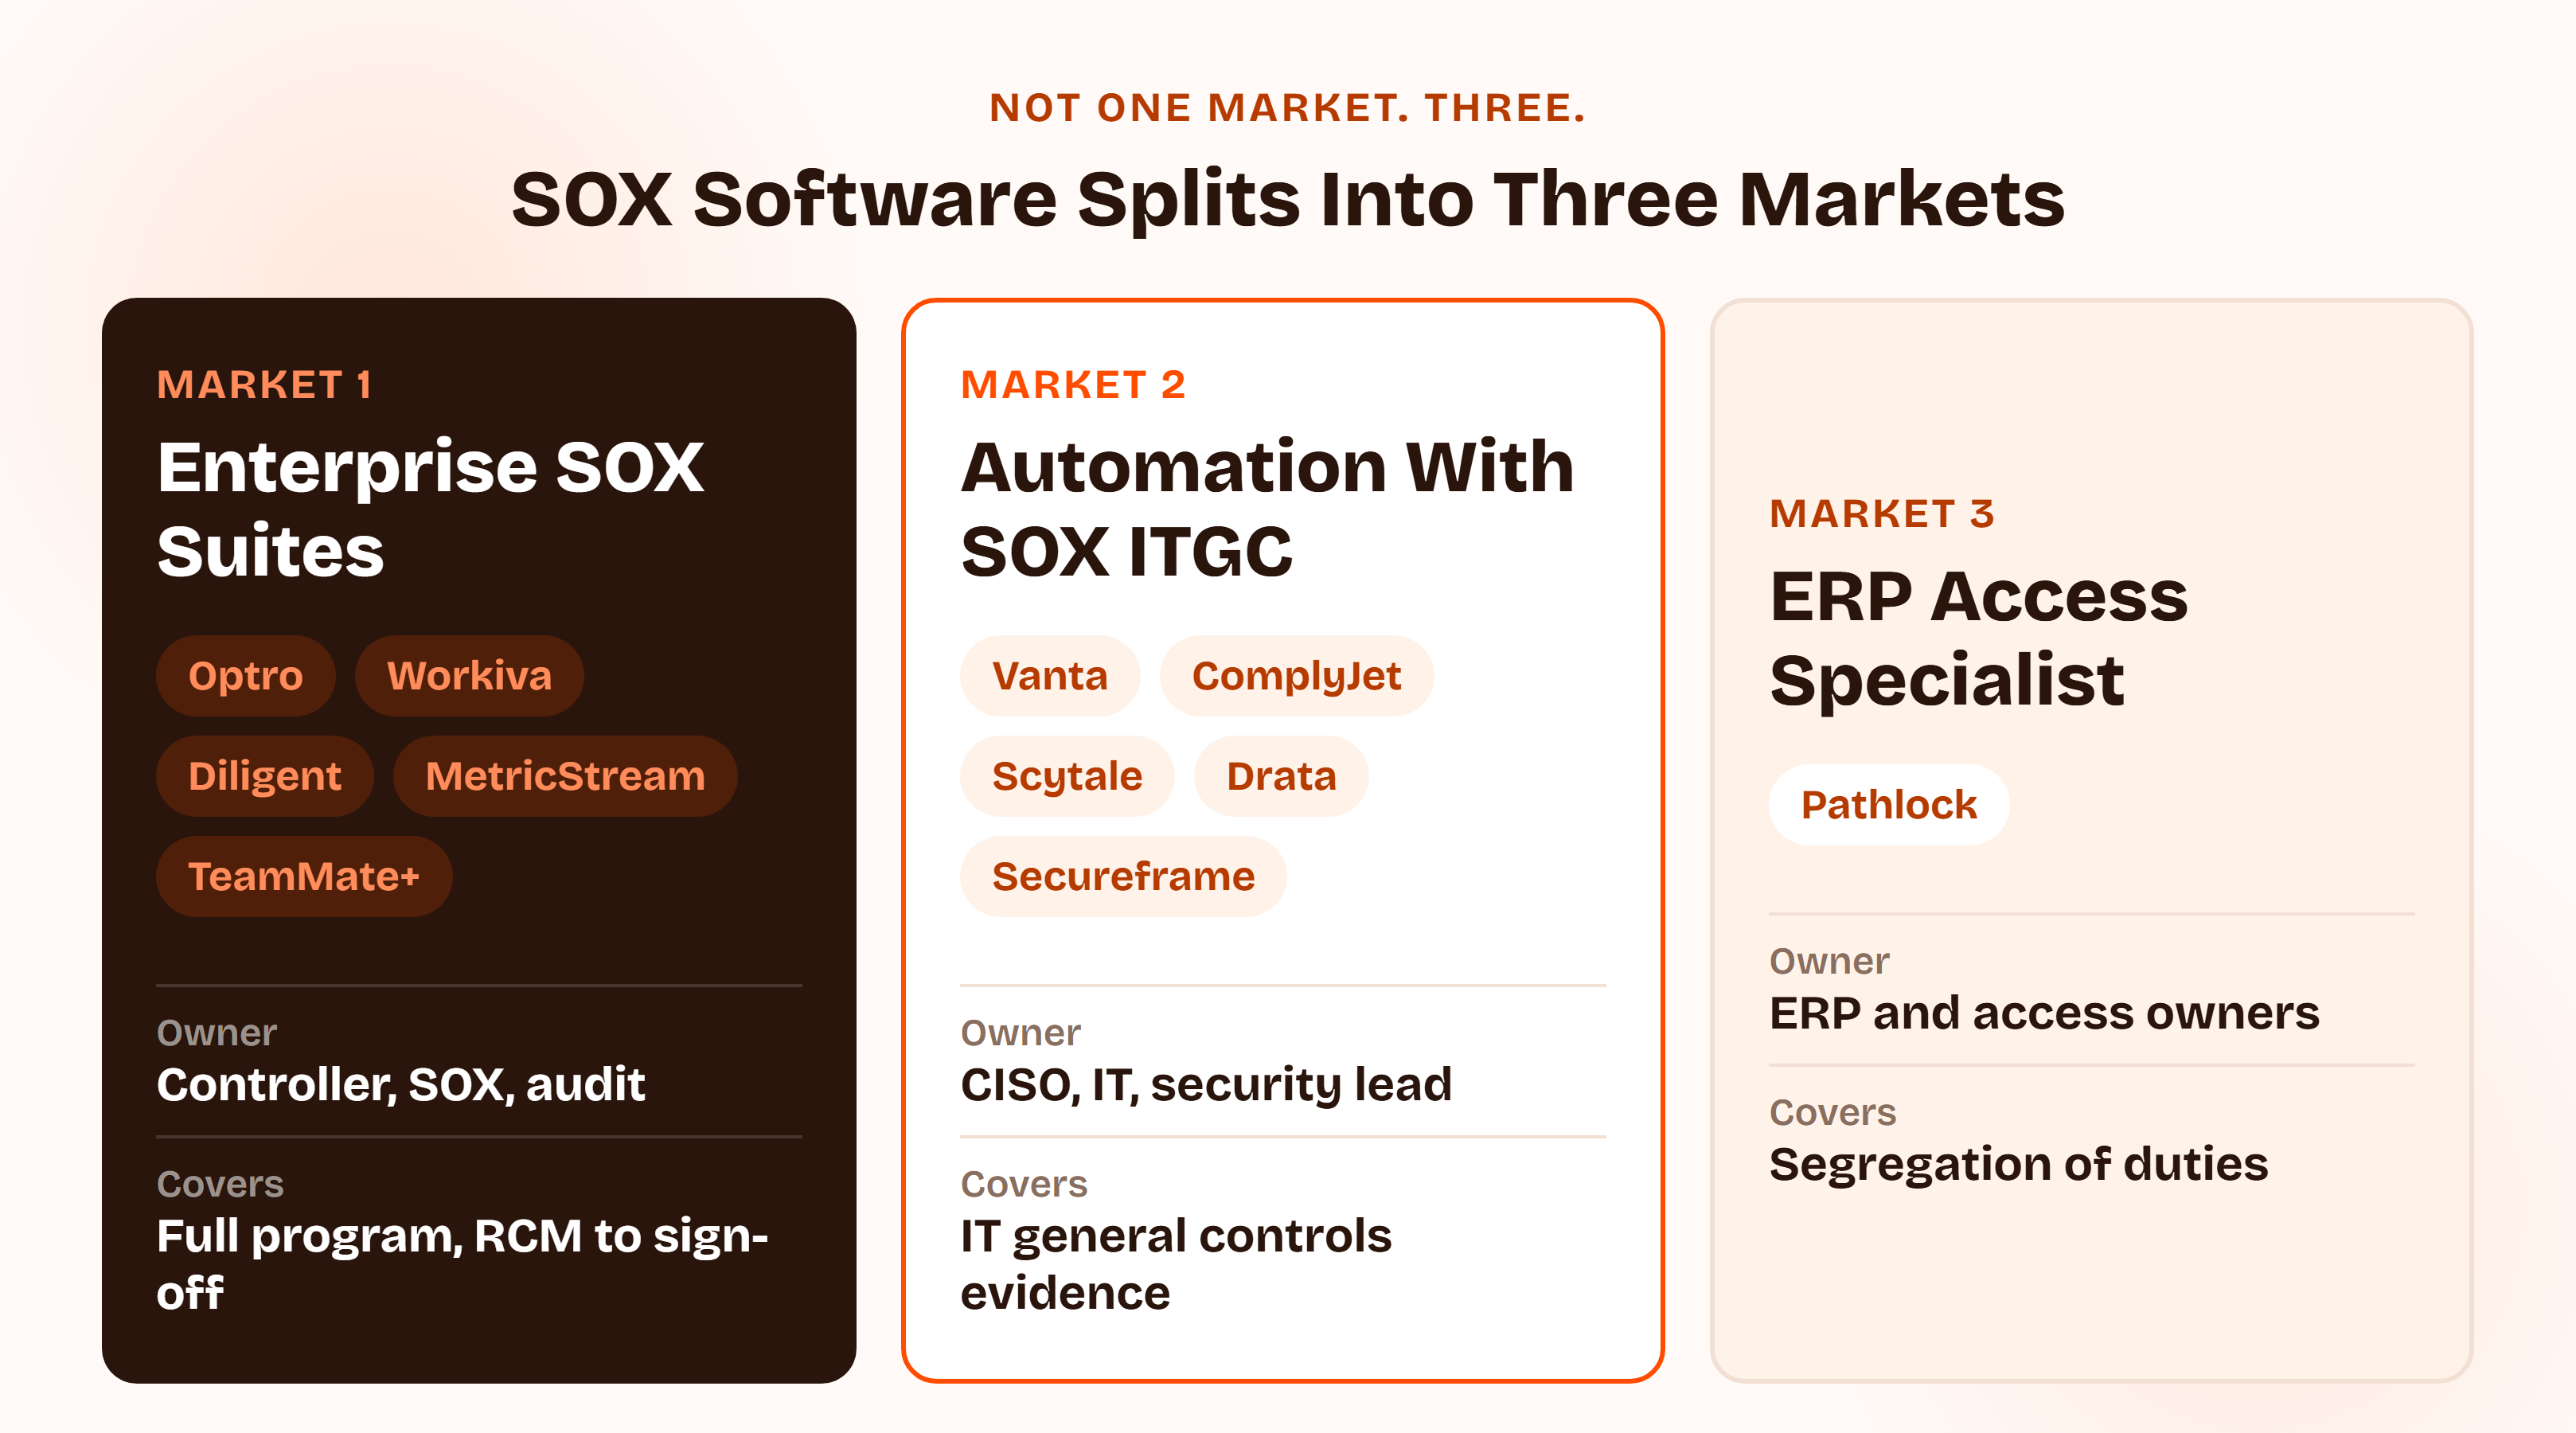
Here is the honest frame before any ranking. Some of these tools manage the whole SOX program: risk-control matrices, testing, deficiencies, management certifications. Others automate only the IT general controls slice with continuous evidence collection. One specializes in ERP access. That split, not a single leaderboard, is how the rest of this guide is organized.
What Is SOX Compliance Software? Why the Best SOX Compliance Software Splits Into Three Markets
SOX compliance software is the platform layer that helps a company run the internal-control work the Sarbanes-Oxley Act requires: documenting the risk-control matrix, testing controls, tracking deficiencies to remediation, collecting evidence for the external auditor, and supporting the Section 302 and 404 certifications that management signs. It shows up in searches as SOX compliance tools, SOX management software, SOX ITGC software, and SOX compliance automation software, and those labels describe genuinely different products.
Three markets share the term.
Enterprise SOX and internal-controls suites are built for public-company finance, internal audit, and compliance teams. Optro (the company formerly known as AuditBoard), Workiva, Diligent, MetricStream, and Wolters Kluwer's TeamMate+ Controls sit here. They manage the full program: process narratives, risk-control matrices, control testing, certifications, and auditor collaboration.
Compliance-automation platforms with a SOX ITGC module are the SOC 2 and ISO 27001 tools you may already know. Vanta, Scytale, ComplyJet, Drata, and Secureframe added SOX ITGC as a framework, so the same integrations that collect SOC 2 evidence also test access, change management, and IT operations controls. They cover the IT slice of SOX, not the finance-process slice.
ERP access-governance specialists like Pathlock focus on the part of SOX that most often produces findings inside SAP, Oracle, and Workday: who can do what, and whether those permissions conflict.
Why does the manual approach stop working? Because SOX is a repeating cycle, not a project. Controls get tested every quarter, evidence has to be current and retrievable, and the external auditor will ask for the same population of access lists and change tickets you pulled last quarter, with a new date on them. Software earns its cost by making that cycle repeatable: one control library, one evidence trail, one place the auditor and the control owner both look.
The questions auditors ask have not changed much. A commenter who said he was Yelp's director of systems during its IPO wrote in a 2015 Hacker News thread that auditors care about "who can access the data, who can change data" for anything feeding financial reports. Those are still the access and change-management questions ITGC software now tests on a schedule.
Not what this article is
This is a software comparison, not a SOX explainer. For what the law requires and when a private company should start, read ComplyJet's SOX compliance guide. For the execution list, use the SOX compliance checklist. For how SOX differs from a SOC 2 report, see SOC 2 vs SOX. This piece picks up where those end: which tool to actually buy.
Which Market Has the Best SOX Compliance Software for You?
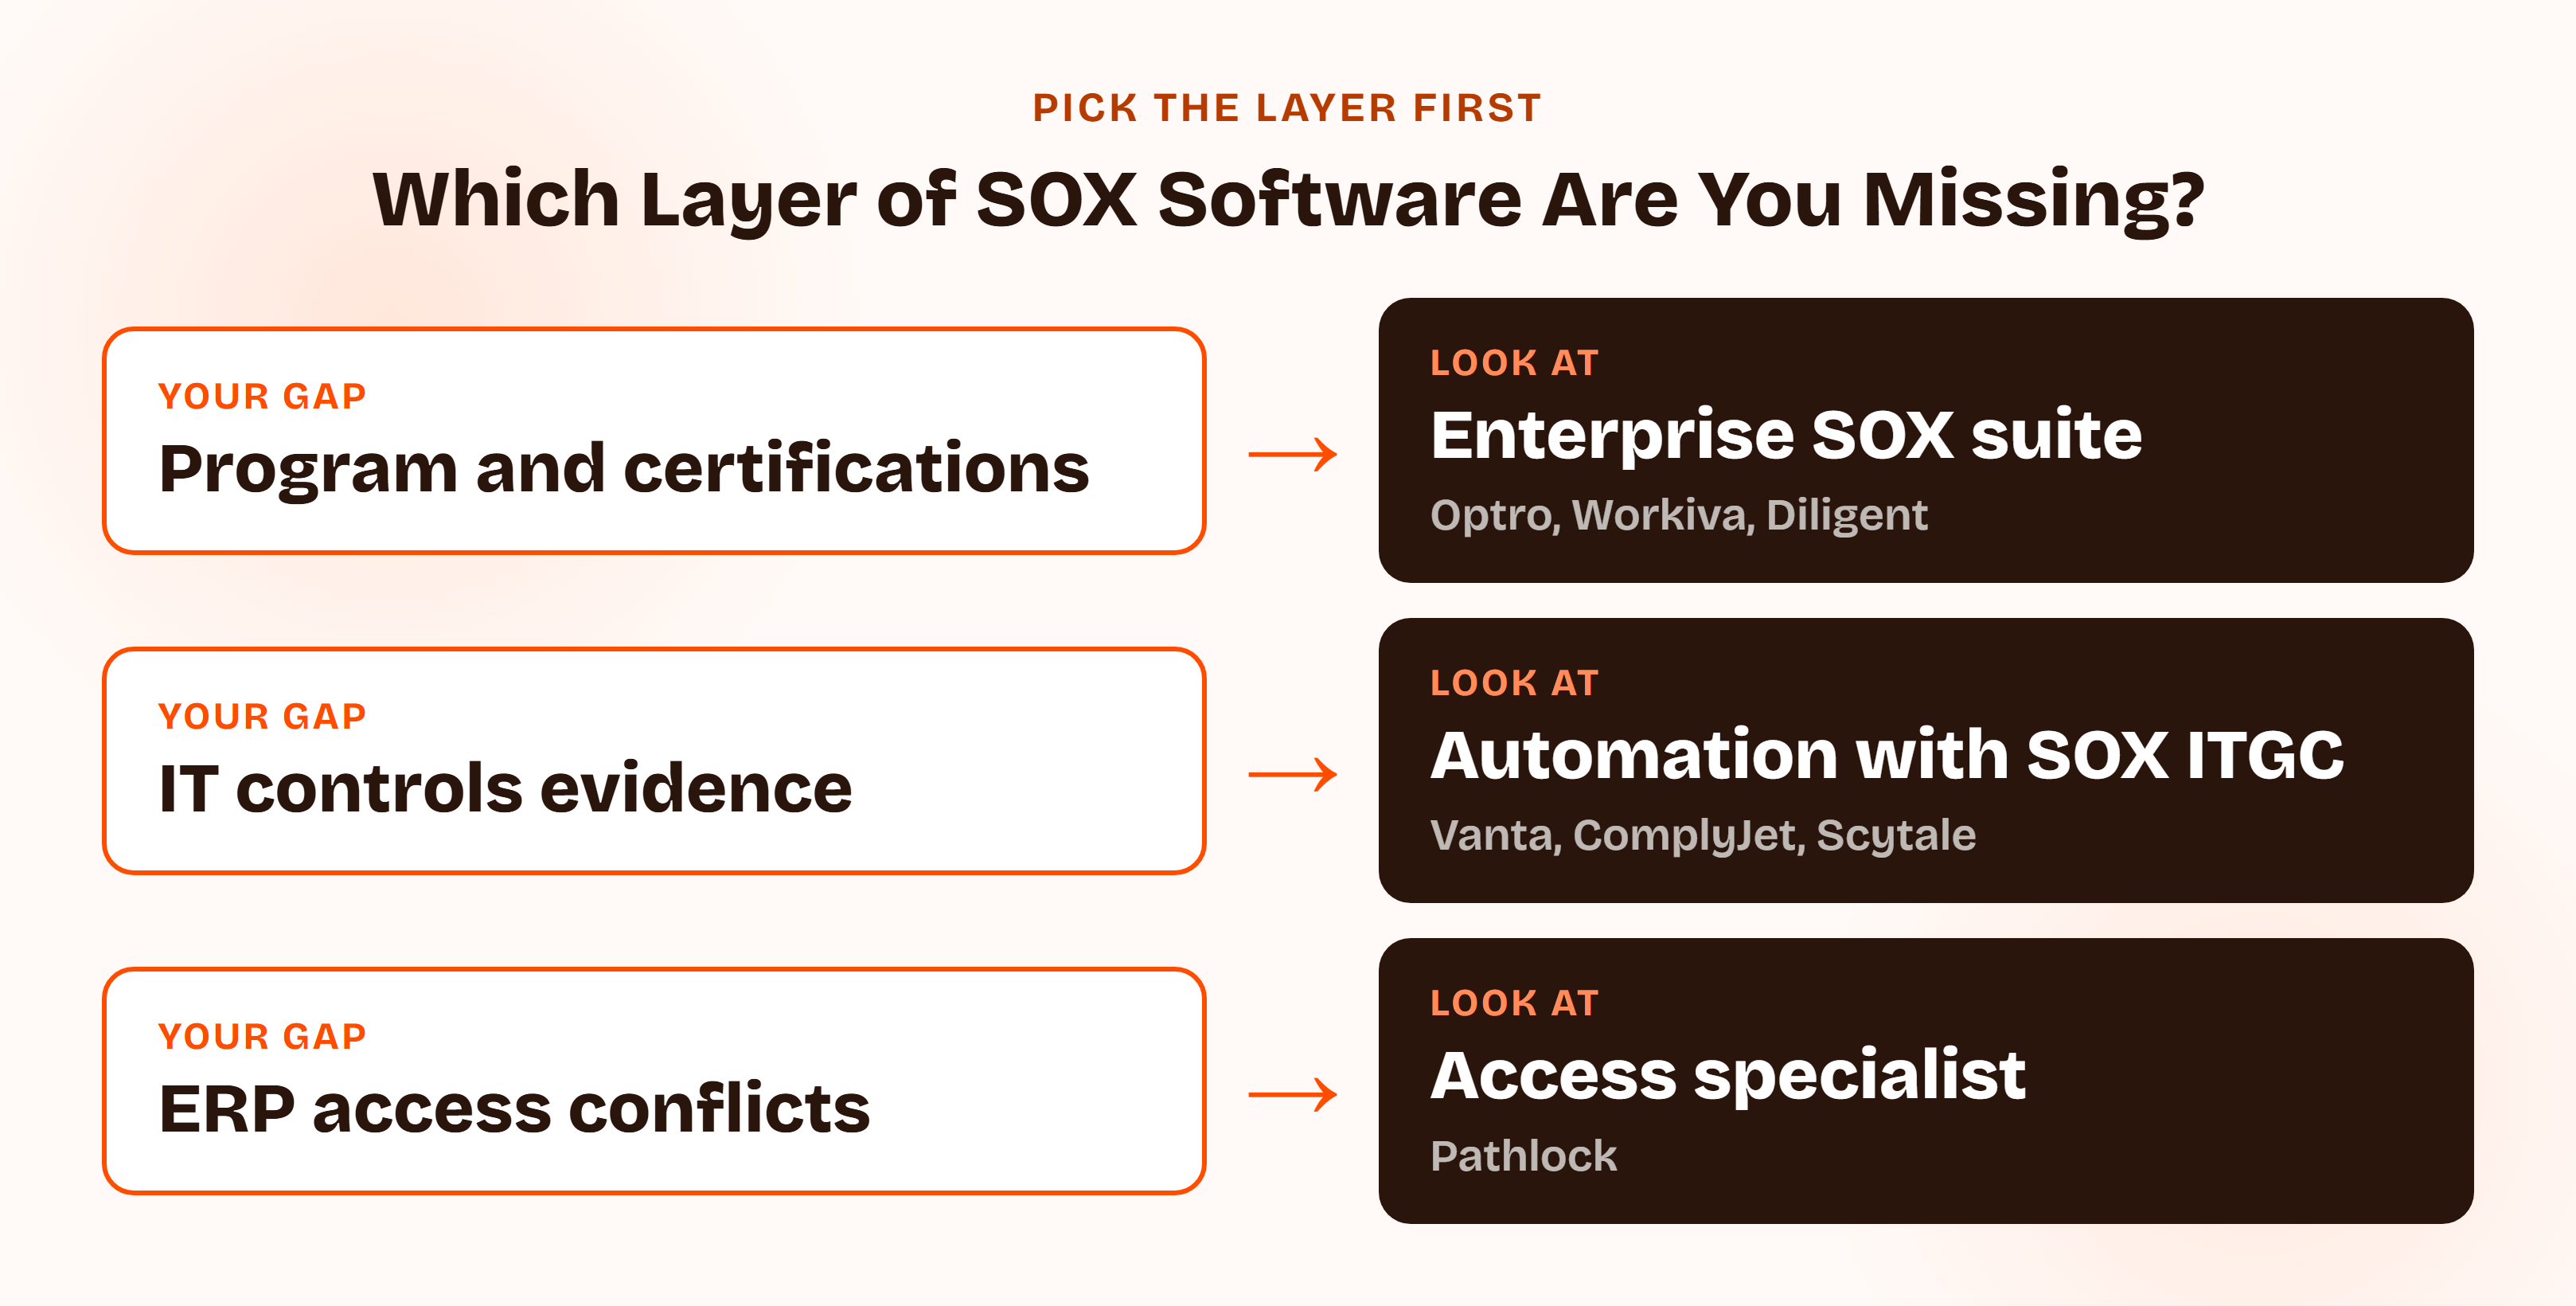
Start with two questions. Who owns SOX at your company, and what is failing today?
If the owner is a controller, SOX director, or internal audit lead, and what is failing is the program itself (narratives in Word, testing in Excel, certifications by email), you are shopping in the first market.
If the owner is a CISO, head of IT, or security lead, and what is failing is ITGC evidence (quarterly access reviews, change-management proof, terminated-user checks), the second market fits. If your findings cluster around segregation of duties in your ERP, the third is where you look.
One subtle point most buyers miss: ITGC is a subset of SOX. A platform that tests your IT general controls flawlessly can still leave revenue recognition, journal entries, and close controls untouched. Vanta says this plainly on its own SOX ITGC page, noting that financial controls fall outside ITGC scope and need a custom framework. Keep that boundary in mind for every tool below.
Worth Checking First
Is this really a SOX mandate, or an enterprise customer asking for SOC 1 or SOC 2?
ComplyJet supports SOC 1 and SOC 2 for growth-stage companies, and the access-control, change-management, and monitoring evidence built for those reports overlaps with what a SOX ITGC program needs. SOX itself has no certificate to earn, so it is worth confirming which ask you actually have.
How I Evaluated These 11 Best SOX Compliance Software Tools (SOX Compliance Tools Method)
I did not rank these off a roundup or a features-page skim. For each vendor I went to its own site and looked for a real SOX listing: a dedicated SOX product page, or SOX named in a live frameworks list. A blog post that merely explains what SOX is did not count.
I sorted every tool into one of the three markets above, because comparing a controls suite to an ITGC module on features alone gives you nonsense. Then I checked what each one says it covers (full program, IT slice only, or ERP access), where the vendor states its own limits, whether pricing is published, and whether a real, named customer says anything about SOX specifically.
Pricing is the weak point of this whole category. Ten of the eleven vendors do not publish SOX pricing on the pages I checked, so I did not invent ranges. The exception is ComplyJet, which publishes platform pricing.
Where I could not verify something, I say so. Two vendors, Workiva and Wolters Kluwer, blocked my automated page fetches, so those two entries rest on their own SOX and controls-management pages as they appeared in search results rather than a full read.
The order below is my judgment, not a scoreboard, and it is ranked for the reader this guide mostly serves: a private, pre-IPO, or newly public company with a lean team, where the SOX gap is IT controls.
That is why the compliance-automation platforms (#1 to #5) come first, then the enterprise suites (#6 to #10), then the ERP specialist (#11). If you are a public company with a dedicated SOX team and a full program to run, start reading at #6, because for you the enterprise suites are the first look, not the second.
Within each group, the order reflects breadth of SOX coverage, verifiable detail, and startup fit.
ComplyJet is ranked here, and I should say why and where it falls short. ComplyJet is our company.
It is included because it lists SOX ITGC as a supported framework with built-in ITGC domain mapping, and it sits at #2 because it is the only vendor in the group that publishes its pricing and it is built for exactly the startup buyer above. It is not a full SOX program manager, it is smaller than Vanta and Drata, and SOX ITGC is a recent addition, all of which are spelled out in its Cons.
Read that entry with the same skepticism I applied to Scytale's roundup.
I also checked and excluded a few names that appear in other SOX roundups. Hyperproof's homepage lists 160+ frameworks and none of them is SOX, and its SOX solution URL returns a 404. Sprinto surfaced only as a general compliance-automation platform, with no SOX ITGC framework page I could find. SafetyCulture and Lumiform are inspection and checklist apps, which is a different job from testing SOX controls.
Quick Comparison: 11 Best SOX Compliance Software Tools at a Glance
| Tool | Market | Best for | Pricing | Standout feature |
|---|---|---|---|---|
| Vanta | Automation platform | Pre-IPO and newly public teams already on Vanta for SOC 2 | Not public | Pre-built SOX ITGC controls tested hourly across 400+ integrations |
| ComplyJet | Automation platform | Startups and pre-IPO teams under 50 employees adding SOX ITGC to SOC 1 or SOC 2 | $7,999/year Core, $9,999/year Plus (3-year plan, up to 50 employees) | Built-in ITGC domain mapping with flat per-company pricing and 350+ integrations |
| Scytale | Automation platform | Public companies wanting a dedicated SOX ITGC product | Not public | Automated ITGC working papers and 24/7 deficiency monitoring |
| Drata | Automation platform | Existing Drata customers adding SOX ITGC | Not public | SOX ITGC listed among 30+ pre-built frameworks |
| Secureframe | Automation platform | Teams wanting ITGC testing from 200+ integrations | Not public | Automatic control testing plus policy templates from former auditors |
| Optro (formerly AuditBoard) | Enterprise suite | Public-company SOX and internal audit teams | Not public | AI-powered autonomous control testing; grew out of a SOX-first product |
| Workiva | Enterprise suite | Finance teams running SOX alongside SEC reporting | Not public | Links the risk-control matrix, narratives and flowcharts on one platform |
| Diligent | Enterprise suite | Multi-entity compliance and audit teams | Not public | Built-in SOX, COSO and SOX ITGC frameworks; claims a 10-day program launch |
| MetricStream | Enterprise suite | Large enterprises with a broad GRC footprint | Not public | Financial accounts and assertions mapped inside the SOX framework |
| Wolters Kluwer TeamMate+ Controls | Enterprise suite | Audit teams that already run TeamMate | Not public | Dynamic control mapping across SOX and other frameworks |
| Pathlock | ERP access specialist | SAP, Oracle and Workday shops with SoD findings | Not public | Cross-application segregation-of-duties analysis |
Read the table by market first, then by fit. A tool in the wrong market will look weak on features that were never its job, so compare vendors within a market before you compare across them.
The 11 Best SOX Compliance Software Tools in 2026
1. Vanta
Vanta is the category default for startup compliance, and its SOX ITGC page is direct about who it is for: public US companies preparing for an audit or IPO. It comes with pre-built SOX ITGC controls covering access, change management, and IT operations, automated tests that monitor controls hourly, and 400+ integrations across cloud, code, identity, and device tools.
What I respect most is the scope honesty. Vanta's page states that financial controls such as revenue recognition and journal entries fall outside ITGC scope and need a custom framework. Its help center adds that the set of in-scope systems for ITGC is often different from a SOC 2 scope, so you cannot assume your SOC 2 boundary carries over unchanged.
That makes Vanta a strong pick for the IT slice of SOX if you already run SOC 2 or ISO 27001 there, and a partial answer if you are hoping one tool will run the whole program.
Users of these platforms are not uniformly happy either. In an August 2026 Hacker News comment on a SOC 2 thread, a commenter who had set up Drata, Vanta and Oneleet over roughly a decade called grabbing evidence screenshots "a huge pain."
It was a SOC 2 remark, not a SOX one, but it is a fair prompt to ask in any demo how much ITGC evidence is pulled by integration and how much still needs a human with a screenshot tool.
"Vanta has helped address our pain point of having 1,000 spreadsheets, and transforming that into one single source of truth." Mandy Matthew, Lead Senior Security Risk Program Manager, Duolingo (as featured on Vanta's SOX ITGC page)
Key features:
- Pre-built SOX ITGC controls for access, change management and IT operations
- Hourly automated tests across 400+ integrations
- Adaptive scoping and custom tests to map controls to financial applications
- Cross-framework support so SOX ITGC work reuses other framework evidence
Pros
- Clear, honest statement of what ITGC does and does not cover
- Same integrations and workflow as its SOC 2 product
- Named customer proof on the SOX page
Cons
- Financial (non-IT) controls need a custom framework
- No public pricing on the SOX page; it points you to a demo
- You still need a process for narratives, management certifications and finance-side testing
Pricing: Not public. The pages I checked send you to a demo request for a quote.
Best for: Pre-IPO and newly public teams that already run SOC 2 or ISO 27001 on Vanta and need the IT controls slice of SOX.
2. ComplyJet
Disclosure: ComplyJet is the company that publishes this blog. I ranked it against the same checks as every other vendor here, and its Cons below are as specific as anyone else's.
ComplyJet is a compliance-automation platform built for SaaS startups and growth-stage companies, and it is the newest entry in the ITGC tier. It added SOX ITGC as a framework, with built-in ITGC domain mapping that organizes controls under the IT general control areas auditors test: access, change management, and IT operations. The same integrations that collect evidence for its SOC 2 and ISO 27001 programs feed that mapping, across 350+ integrations.
Two things put it near the top for the reader this guide is written for.
First, the evidence overlap: the access-control, change-management, and monitoring evidence a company builds for SOC 1 and SOC 2 is largely the same evidence a SOX ITGC program asks for, so a private company can build it once.
Second, the commercial model. ComplyJet uses flat per-company pricing rather than per-seat, and it publishes its prices, which is rare in this category. AI-assisted policy drafting and a team that walks you through implementation round out the pitch.
I want to be clear about the boundary. ComplyJet covers the IT slice of SOX.
It is not a full SOX 404 program manager: I am not claiming it runs a risk-control matrix, control testing workflows, PBC request tracking, deficiency management, or management certifications, so a public company that needs those still needs a program-management tool from the enterprise group. ComplyJet is also not your auditor, and there is no such thing as a SOX certification to hand out, since SOX compliance is assessed through your management assessment and your external auditor's opinion.
Key features:
- Built-in ITGC domain mapping for access, change management and IT operations controls
- Evidence reuse between SOC 1, SOC 2 and SOX ITGC programs
- 350+ integrations feeding continuous evidence collection
- AI-assisted policy drafting and a guided, team-led implementation
Pros
- Published, flat per-company pricing in a category where nobody else lists a price
- Startup-sized: built for teams under about 50 employees with a first compliance program
- SOC 1 and SOC 2 evidence carries over to ITGC work
- Team-guided implementation rather than software access alone
Cons
- ITGC layer only: no full SOX 404 program, PBC or finance-side testing workflow suite
- SOX ITGC is newly added, so it has a shorter SOX track record and no named SOX customer quote to show yet
- Smaller than Vanta and Drata, with less integration and community depth
- Small G2 review base: 4.9 out of 5 from 16 reviews as of 2026-09-29 (G2)
- Not an auditor: your independent auditor and any SOX advisory work sit outside the subscription
Pricing: Published. $7,999/year Core and $9,999/year Plus on a 3-year plan, up to 50 employees (Core covers one framework package, Plus covers two). Larger teams are on a custom plan. The pricing page prices framework packages, so ask whether SOX ITGC counts as one of your packages.
Best for: Startups and pre-IPO companies under about 50 employees that already run, or are about to run, SOC 1 or SOC 2 and want the IT controls slice of SOX at a published price.
SOX ITGC Readiness
Getting the IT controls ready before your first SOX year?
See how ComplyJet maps your access, change-management, and IT operations controls to ITGC domains, on flat per-company pricing with a team guiding you through it.
3. Scytale
Scytale is the only compliance-automation vendor on this list with a dedicated SOX ITGC product page rather than a framework tile. It describes 24/7 deficiency monitoring of ITGC controls, automated working papers that generate ITGC audit documentation, and a three-layer architecture: data extraction, consolidation, and a customizable compliance-logic rule engine.
It also publishes an implementation shape: roughly one week for integration, two weeks for customization, then a data-cleansing phase. It targets public companies with complex IT control environments that want to cut manual ITGC audit hours, and it lists SOX ITGC among 80+ frameworks it supports.
A disclosure: Scytale publishes its own "best SOX compliance tools" roundup that ranks Scytale first. I did not use that ranking as a source. I used the SOX ITGC product page, and I note the conflict of interest so you can weigh it when you read theirs.
"Manual ITGC management testing was overwhelming and prone to gaps. The platform's automation highlights trends and gaps more effectively, helping us resolve issues before audits." Ludmila Rossbach, Director of SOX, Pagaya (as featured on Scytale's SOX ITGC page)
Key features:
- 24/7 ITGC deficiency monitoring
- Automated ITGC working papers
- Three-layer data architecture with a customizable rule engine
- Published onboarding phases (integration, customization, data cleansing)
Pros
- Dedicated SOX ITGC product, not just a framework listing
- Automated working papers speak directly to auditor deliverables
- Named SOX customer quote from a working SOX director
Cons
- Pricing not published
- Focused on ITGC, so finance-process controls sit outside its described scope
- Its own SOX roundup ranks itself first, so treat vendor-authored comparisons with care
Pricing: Not public. The pages I checked send you to a demo request for a quote.
Best for: Public companies that want a purpose-built SOX ITGC automation product.
4. Drata
Drata lists SOX ITGC on its live frameworks page with a one-line description: demonstrate IT controls for reliable financial reporting. It sits among 30+ pre-built frameworks on the same platform that runs SOC 2, ISO 27001, and the rest.
That listing is all I could verify, and I want to be clear about the limit. On the frameworks page the SOX ITGC entry links to Drata's demo page rather than a dedicated framework page, so I could not read control counts, test coverage, or any SOX-specific customer story. For an existing Drata customer, that is still a meaningful signal that the framework is available on the platform you already use.
If SOX ITGC depth is the reason you are buying, ask for the control list and test mapping in the demo before you commit. If you are already a Drata shop and need a first pass at ITGC evidence, the shared platform is the practical advantage.
Key features:
- SOX ITGC listed among 30+ pre-built frameworks
- Same platform and integrations as Drata's SOC 2 and ISO 27001 programs
- Cross-framework control reuse on one platform
Pros
- Convenient for teams already running Drata
- Broad framework library keeps SOX ITGC alongside other programs
- Confirmed on Drata's own frameworks page
Cons
- No dedicated SOX ITGC product page found, so depth is unverified
- No SOX-specific customer quote or published control count
- Pricing gated behind a demo
Pricing: Not public. The pages I checked send you to a demo request for a quote.
Best for: Existing Drata customers adding SOX ITGC to a SOC 2 or ISO 27001 program.
5. Secureframe
Secureframe has a dedicated SOX ITGC page and a launch announcement for its SOX ITGC support, aimed at publicly traded US companies or those seeking to list. The page centers on automation: automatic control testing through continuous configuration data collection from 200+ integrations, with real-time alerts on misconfigurations and remediation guidance.
It also offers policy templates developed and verified by in-house experts and former auditors, and third-party risk management to help identify and manage vendor risks. The framing is evidence automation for the IT slice of SOX, in the same style as Secureframe's SOC 2 work.
I found no pricing and no named SOX customer quote on the page, and the launch announcement I fetched carried no visible publication date, so I cannot say how long the module has been live.
Key features:
- Automatic control testing from 200+ integrations
- Real-time alerts on failing controls with remediation guidance
- Policy templates from in-house experts and former auditors
- Third-party risk management in the same platform
Pros
- Dedicated SOX ITGC page and launch write-up
- Clear focus on continuous evidence collection
- Reuses the platform and integrations of its SOC 2 product
Cons
- No published pricing
- No named SOX customer testimonial on its page
- Scope is IT controls; finance-process SOX work needs another tool
Pricing: Not public. The pages I checked send you to a demo request for a quote.
Best for: Teams that want ITGC testing automated from a broad integration library.
SOC 1 & SOC 2 Groundwork
The automation tier reuses your SOC 2 evidence. Have you built that base yet?
If you would rather build once, ComplyJet runs SOC 1, SOC 2 and SOX ITGC on the same evidence, with flat per-company pricing and a team that guides you through the process. There is no SOX certificate, but the access, change and monitoring evidence carries across. See SOC 1 vs SOC 2 to see which report fits.
6. Optro (Formerly AuditBoard)
Optro is the best-known name in this category under a new label. AuditBoard announced its rebrand to Optro on March 9, 2026, and the old auditboard.com domain now redirects to optro.ai. The company began life as SOXHUB, a SOX-focused internal audit product, so SOX management is the origin of the platform rather than a module added later.
Its SOX management page centers on AI-driven testing: autonomous testing of controls, continuous control monitoring, and AI-generated planning documentation including narratives and flowcharts. There are customizable workflows for internal teams and external auditors, which matters because the auditor handoff is where many SOX programs slow down.
The audience is explicit on the page: enterprise organizations that need to automate controls testing and improve collaboration between control owners and stakeholders. Optro also says it is trusted by more than half of the Fortune 500, which is the vendor's own claim, and a useful signal of who it is built for.
For an outside view, Rishabh Singhal, whose name carries a CISA credential and who offers Workiva and AuditBoard implementation help, wrote in an August 2025 LinkedIn post that he finds AuditBoard's "dashboarding and usability more seamless" for SOX work. That is one consultant's preference, not a benchmark, and the same post is careful to say the right answer depends on the environment.
"Optro has allowed us to take a step back and rationalize our control structure." Scott Cronin, Global Head of SOX Compliance & Controls, BNY Mellon (as featured on Optro's SOX management page)
Key features:
- Autonomous, AI-assisted control testing and continuous monitoring
- AI-generated process narratives and flowcharts for planning
- Workflows shared between internal teams and external auditors
- Part of a broader connected-risk platform covering internal audit, third-party risk and AI governance
Pros
- SOX-first heritage, so the core workflows are mature
- Strong named-customer proof on its SOX page
- Covers the full program (RCM, testing, deficiencies), not just IT controls
- Scales to complex multi-entity environments
Cons
- Pricing is not published anywhere on the SOX page
- Built for enterprise programs; a pre-IPO startup will likely buy more platform than it needs
- The rebrand means reviews, docs and comparison pages still use the AuditBoard name, so research takes extra care
Pricing: Not public. The pages I checked send you to a demo request for a quote.
Best for: Public-company SOX, internal audit and finance teams that want one platform for the full controls program.
7. Workiva
Workiva approaches SOX from the finance side. Its SOX and internal-controls pages describe automating control testing and workflows for SOX and its international cousins, including UK SOX and J-SOX, on one platform that also handles financial reporting. If your SOX owner already lives in the tool that assembles your SEC filings, that adjacency is the pitch.
The platform links the risk-control matrix, process narratives, and flowcharts to testing workflows and evidence, and Workiva says it uses AI agents to automate testing, from refining attributes to generating rules to executing tests. That is a finance-and-audit workflow story more than an IT-evidence story.
The practitioner view is not one-sided here. The consultant in the same LinkedIn post that leans toward Optro also wrote that he has "seen Workiva work beautifully in the right environment," which fits a team that already collaborates in Workiva for reporting.
One disclosure about this entry: workiva.com returned an access error to my automated fetch, so what I can state rests on its SOX and internal-controls page listings as they appeared in search, not a full page read. I found no named SOX customer quote I could verify, so I have not included one.
Key features:
- SOX controls management with risk-control matrix, narratives and flowcharts linked to testing
- AI agents for test design and execution
- Support for UK SOX, J-SOX and other international internal-control regimes
- Shared platform with financial and sustainability reporting
Pros
- Natural fit when finance already reports on Workiva
- Multi-regime support helps global companies
- Full-program scope, not just ITGC
Cons
- No published pricing
- Less relevant if your SOX pain is IT evidence collection rather than finance-process controls
- I could not do a full read of its pages, so feature depth is unverified beyond its own listing
Pricing: Not public. The pages I checked send you to a demo request for a quote.
Best for: Finance and controllership teams that want SOX inside the same platform as their external reporting.
8. Diligent
Diligent sells SOX under two overlapping names. The page title still carries HighBond, the legacy product name, while the unified branding is the Diligent One Platform. Its SOX management page describes a centralized risk and control library aligned to the COSO internal control framework, pre-configured SOX templates, automated controls monitoring, and one-click reporting.
Diligent's internal controls product page adds that you can build a library from Excel or use built-in SOX, COSO, and SOX ITGC frameworks. The headline claim on the SOX page is that you can establish a robust SOX program in 10 days. That is the vendor's own number, and it depends entirely on your scope, so treat it as a best case.
The audience is compliance, risk, audit and general counsel teams, and the emphasis on multiple business entities suggests companies with real organizational complexity rather than a single-entity startup.
Key features:
- Centralized risk and control library aligned to COSO
- Built-in SOX, COSO and SOX ITGC frameworks
- Automated controls monitoring and one-click compliance reporting
- SOX-specific dashboards for program status and entity reporting
Pros
- Pre-configured SOX content shortens initial setup
- Good fit for multi-entity oversight
- Sits inside a broader audit and GRC suite
Cons
- No published pricing
- The HighBond and Diligent One naming overlap makes it harder to tell exactly which product you are buying
- The 10-day launch claim is unverified and scope-dependent
Pricing: Not public. The pages I checked send you to a demo request for a quote.
Best for: Multi-entity compliance and internal audit teams that want SOX content pre-loaded.
9. MetricStream
MetricStream is the classic enterprise GRC vendor, and its SOX compliance management product is built for complex, regulated organizations. The page describes a centralized SOX framework covering processes, risks, controls, financial accounts, financial statement assertions, evidence, questionnaires, and tests, with support for Section 302 and 404 certifications.
Its AI capabilities are aimed at deficiencies: documenting them, suggesting classification, and recommending remediation paths. The product includes real-time dashboards and a risk and control matrix, plus a COSO 2013 framework page tying the tooling to the internal-control standard.
MetricStream publishes performance figures on the page: a 60% reduction in control testing and certification time, 0% errors in SOX certifications, and a 93% reduction in issue resolution time. These are the vendor's own numbers with no methodology attached, so read them as marketing, not benchmarks. Named customers on the page include Shell, PETRONAS, Siemens Energy, UBS, Glencore, and BAE Systems.
Key features:
- Financial accounts and statement assertions mapped inside the SOX framework
- Section 302 and 404 certification workflows
- AI-assisted deficiency classification and remediation
- COSO 2013 framework alignment
Pros
- Deep, finance-aware SOX data model
- Proven with large global enterprises
- Part of a wider GRC platform
Cons
- Enterprise scale and implementation weight; likely too much for a mid-size or pre-IPO team
- No published pricing
- Headline performance numbers are self-reported
Pricing: Not public. The pages I checked send you to a demo request for a quote.
Best for: Large enterprises that want SOX inside a broad enterprise GRC platform.
10. Wolters Kluwer TeamMate+ Controls
TeamMate+ Controls is Wolters Kluwer's controls management product, positioned for financial reporting needs. Its pages describe centralizing control documentation, streamlining testing and monitoring, and driving ownership across control owners in the business, with configurable templates, workflows, and surveys for evidence collection.
What differentiates it is control mapping: teams can align control activities to multiple frameworks, including SOX, CSRD, and GDPR, using dynamic mapping and shared testing. Wolters Kluwer also lists SOX, ISO 27001, and COSO as supported frameworks and hosts a UK SOX demo.
It is part of the wider TeamMate family, which includes an audit management product, so the natural buyer is an internal audit function already in that ecosystem. As with Workiva, Wolters Kluwer's site blocked my automated fetch, so this entry rests on its page listings in search results.
Key features:
- Central control documentation with configurable testing templates and workflows
- Dynamic control mapping across SOX and other frameworks
- Surveys and workflows for control-owner self-assessment
- UK SOX support
Pros
- Shared testing across frameworks cuts duplicate work
- Fits naturally beside TeamMate audit management
- Broad framework flexibility beyond SOX
Cons
- No published pricing
- Best value when you already use the TeamMate ecosystem
- I could not read the full pages, so implementation detail is unverified
Pricing: Not public. The pages I checked send you to a demo request for a quote.
Best for: Internal audit teams that already run TeamMate and want controls management in the same family.
11. Pathlock
Pathlock is the specialist. Its SOX page centers on access risk analysis that continuously finds segregation-of-duties conflicts, automated periodic user access reviews with audit-ready evidence, elevated and emergency access management with audit trails, and continuous controls monitoring for unauthorized changes.
It lists the ERP and business systems it covers: SAP ERP, Oracle EBS and Fusion Cloud, Workday, PeopleSoft, Microsoft Dynamics 365, JD Edwards, SAP Ariba, and SuccessFactors. If your auditor's findings are about who can post journal entries and approve them, this is the category that speaks to it directly.
The page describes access, SoD, and monitoring. It does not describe a risk-control matrix or a certification workflow, so plan on pairing Pathlock with a program-management tool from the first market.
"Pathlock streamlined our SOX audits by helping us identify true SoD violations." Suzan Zortea, Global Governance Lead, Jabil (as featured on Pathlock's SOX page)
Key features:
- Cross-application segregation-of-duties analysis
- Automated user access reviews with audit-ready evidence
- Elevated access management with full audit trails
- Continuous controls monitoring and dynamic data masking
Pros
- Directly targets the access findings that commonly appear in SOX audits
- Wide ERP coverage
- Named SOX customer quote
Cons
- Not a full SOX program manager; expect to pair it with another tool
- No published pricing
- Most relevant to companies with a large ERP footprint, less so to a cloud-native startup
Pricing: Not public. The pages I checked send you to a demo request for a quote.
Best for: Companies with SAP, Oracle or Workday environments and segregation-of-duties findings.
How to Choose SOX Compliance Software (SOX ITGC Software vs. SOX Management Software)
Here is how to choose SOX compliance software without buying the wrong layer. The "smart choice versus safe choice" question runs through every purchase in this category. The safe choice is the biggest name on the list. The smart choice is the tool that fits your stage, your SOX owner, and the layer of SOX that is actually failing. Work through these in order.
Do You Need the Best SOX Compliance Software Yet, or Is This a Pre-IPO Readiness Question?
SOX applies to public companies. If you are private, no regulator is asking for SOX software today, and the real question is timing. Companies typically begin ITGC and control documentation in the year or two before listing, because the first audit under SOX is much harder if the controls are new and untested.
Engineering teams often resist that early work: a self-described audit, security and GRC professional wrote in a June 2025 Hacker News comment that he keeps hearing "we don't need ITGCs" from tech teams, and he called that a mistake.
If what triggered your search was an enterprise customer asking about security or financial controls assurance, check whether a SOC 1 or SOC 2 report answers it before buying SOX tooling. The SOX compliance guide covers when a pre-IPO company should start.
SOX ITGC Software vs. SOX Management Software: Which Layer of the Best SOX Compliance Software Are You Missing?
This is the most important filter. SOX management software (Optro, Workiva, Diligent, MetricStream, TeamMate+ Controls) runs the program: RCM, narratives, testing, deficiencies, certifications. SOX ITGC software (Vanta, ComplyJet, Scytale, Drata, Secureframe) automates evidence and testing for IT general controls only. Pathlock covers ERP access.
Most public companies need program management and ITGC automation, and buy both. A startup with no finance-side control library and a security-led SOX owner may start with the ITGC layer and add program management as the scope grows.
Best SOX Compliance Software for Your Company Stage: Enterprise Suites vs. Compliance-Automation Fit
Enterprise suites are built for organizations with dedicated SOX teams, multiple entities, and implementation budgets. A 40-person pre-IPO company with one security lead and a fractional controller will spend more time configuring a full suite than testing controls.
The automation platforms are lighter and reuse SOC 2 style integrations, which is why they fit teams already operating that way. The tradeoff is the scope gap Vanta itself points out: financial controls are outside ITGC. That is also the honest limit on ComplyJet at #2: it is a good fit for a lean pre-IPO team and a poor fit for a public company that needs a full SOX program platform.
Buyer's checklist
Before any demo, ask every vendor three things in writing. What is in scope, ITGC only or financial controls too? Which named customers use the SOX product specifically, not the platform in general? What does year two cost? Vendors that answer clearly are usually the ones with something real to show.
What to Ask About Pricing Before You Book a Demo
Because only ComplyJet publishes pricing ($7,999/year Core and $9,999/year Plus on a 3-year plan, up to 50 employees), for the other ten the demo is where the real number appears, and it will vary with scope. Ask what drives the quote (entities, in-scope systems, users, or control count), whether SOX ITGC is a separate module from your SOC 2 subscription, and what the renewal terms are.
Ask for the same scope in writing from every vendor you shortlist, so the quotes are comparable. A price for ITGC only is not comparable to a price for the full program, and comparing them will make the narrower tool look cheaper than it is.
Best SOX Compliance Automation Software When You Already Run SOC 2
If you already run SOC 2 or ISO 27001 on Vanta, ComplyJet, Drata, or Secureframe, check whether the SOX ITGC framework on that platform covers your financial systems before you shop for a second vendor. Shared integrations and one vendor relationship are the fastest path when they fit.
Watch the scope: Vanta's help center notes that in-scope systems for ITGC often differ from a SOC 2 scope, so plan for additional systems such as your ERP and financial applications.
Build the Groundwork
Not at the SOX year yet? Build the evidence once, not twice.
ComplyJet supports SOC 1, SOC 2 and SOX ITGC, and a lot of the access-control, change-management, and monitoring evidence built for either report is the same evidence your SOX ITGC program will need. Read the SOX compliance checklist to see what that looks like.
FAQs
What Is SOX Compliance Software?
It is the software layer that helps a company document, test, and report on the internal controls the Sarbanes-Oxley Act requires. That can mean full-program platforms that manage the risk-control matrix and management certifications, ITGC automation that collects IT evidence continuously, or specialist tools for ERP access.
Do Private Companies Need SOX Compliance Software?
Not legally. SOX applies to public companies. Private companies typically start preparing before an IPO, and some buy ITGC automation early so their first audited SOX year is not the first time the controls are tested.
What Is the Difference Between SOX ITGC Software and GRC Software?
SOX ITGC software focuses on IT general controls: access, change management, and IT operations for systems that touch financial reporting. Broader GRC or SOX management software runs the entire program, including finance-process controls, testing workflows, deficiencies, and certifications. See ComplyJet's best GRC software comparison for the wider category.
How Much Does SOX Compliance Software Cost?
Ten of the eleven vendors compared here do not list SOX pricing on the pages I checked and direct you to request a demo. The exception is ComplyJet, which publishes $7,999/year Core and $9,999/year Plus on a 3-year plan, up to 50 employees. For the rest, expect a quote that depends on entities, systems in scope, and users.
Can Vanta, ComplyJet or Drata Handle SOX Compliance?
They can handle the ITGC slice. Vanta, ComplyJet and Drata all list SOX ITGC, and Vanta states directly that financial controls outside ITGC need a custom framework. None of them replaces a program-management tool for narratives, certifications, and finance-side testing.
Does ComplyJet Support SOX Compliance?
ComplyJet supports the SOX ITGC slice: built-in ITGC domain mapping, evidence collection through 350+ integrations, and evidence overlap with SOC 1 and SOC 2. It is not a full SOX 404 program-management platform, it does not audit, and there is no SOX certification to receive.
Does SOX Compliance Software Replace an External Auditor?
No. The software organizes controls, tests, and evidence. Your independent auditor still performs its own work and forms its own opinion, and the tools here are designed to make that handoff faster.
What Does SOX Compliance Automation Software Automate?
Mostly evidence collection and monitoring: pulling access lists, change records, and configuration data from your systems, testing them against control definitions, and flagging failures. Some suites also automate test design and documentation with AI.
Which Is the Best SOX Compliance Software for a Pre-IPO Startup, and When Should It Buy?
When your listing timeline puts a first SOX assessment within roughly a year or two, and your controls are not yet documented or tested.
For most pre-IPO teams that means starting with the ITGC automation tier (Vanta, ComplyJet, Scytale, Drata or Secureframe) if IT evidence is the gap, and adding a program-management suite once the finance-side control library grows. Earlier than that, a SOC 2 or SOC 1 program is usually the better use of budget. See SOC 2 vs SOX for how the two relate.
Final Thoughts on the Best SOX Compliance Software
There is no single best SOX compliance software, because there are three markets under one search term. Enterprise suites (Optro, Workiva, Diligent, MetricStream, TeamMate+ Controls) run the whole program. Compliance-automation platforms (Vanta, ComplyJet, Scytale, Drata, Secureframe) automate the IT controls slice. Pathlock handles ERP access. Most public companies eventually need more than one layer.
One more practical point: SOX software does not create controls, it runs them. If your control design is weak or nobody owns testing, no platform fixes that on its own. The strongest programs pair the tool with a named owner for each control, a calendar for testing, and an auditor who has seen the evidence format before the fieldwork starts. Buy the software to make good habits repeatable, not to replace them.
Before you request a demo, decide which layer is actually failing, who owns SOX at your company, and whether your real trigger is SOX or a SOC 1 or SOC 2 request from a customer.
If you are a lean pre-IPO team, start with the ITGC tier; if you are a public company with a full program to run, start with the enterprise suites. Ask each vendor for scope and pricing in writing. And treat vendor-authored rankings, including the ones I flagged, as marketing until you have checked the product page yourself.
Free Demo
Not sure whether you need SOX software, or a SOC 1 or SOC 2 report first?
Talk to ComplyJet either way. We support SOC 1, SOC 2 and SOX ITGC for growth-stage companies with flat per-company pricing and a team that guides you through the process. We do not audit or certify SOX, and we will tell you when a full SOX suite is the right answer instead.
Related Reading on the Best SOX Compliance Software
- SOX Compliance: What It Is, Requirements, and How to Prepare, for the full guide to the law and when a private company should start.
- SOX Compliance Checklist: Requirements, Steps, and Internal Controls, for the execution list behind any of these tools.
- SOC 2 vs SOX: Key Differences, Costs and Mistakes to Avoid, for readers deciding between the two frameworks.
- SOC 1 vs SOC 2: Key Differences and Which You Need, for the adjacent reports ComplyJet actually supports.
- Best GRC Software, for a broader governance, risk, and compliance platform comparison.
- Best SOC 2 Compliance Software, the parallel comparison for the SOC 2 platforms that also offer SOX ITGC modules.
Sources: Vendor SOX support verified against each vendor's own site on 2026-09-29: Optro SOX management, Workiva SOX compliance and internal controls management (page listings via search; direct fetch blocked), Diligent SOX management and internal controls, Vanta SOX ITGC and Vanta help center, Scytale SOX ITGC, Drata frameworks, Secureframe SOX ITGC, MetricStream SOX compliance management, Wolters Kluwer TeamMate+ Controls (page listing via search; direct fetch blocked), and Pathlock SOX software.
Also verified: the AuditBoard to Optro rebrand (CPA Practice Advisor, March 9, 2026), Hyperproof's homepage (SOX absent from its framework list, so excluded), and ComplyJet's own frameworks and pricing pages (pricing read 2026-09-29).