An enterprise buyer's AI due-diligence questionnaire comes back with a line you haven't seen before: does your company hold ISO 42001, or have a documented AI governance program? You've got SOC 2, maybe ISO 27001 too — that part's handled. This is a different question, and a shrug isn't an answer a Series B due-diligence team or an enterprise security reviewer will accept.
So you search for the best ISO 42001 software, expecting the kind of ranked, checkable comparison you'd find for SOC 2 or ISO 27001.
What you find instead is a strange mix. Half the results are "best AI governance platform" roundups built around names like Credo AI, Holistic AI, and Microsoft Purview — genuinely real products, but priced and built for a dedicated enterprise AI/ML risk team, not a 20-person startup shipping an AI feature. The other half are single-vendor pages that never name a real competitor.
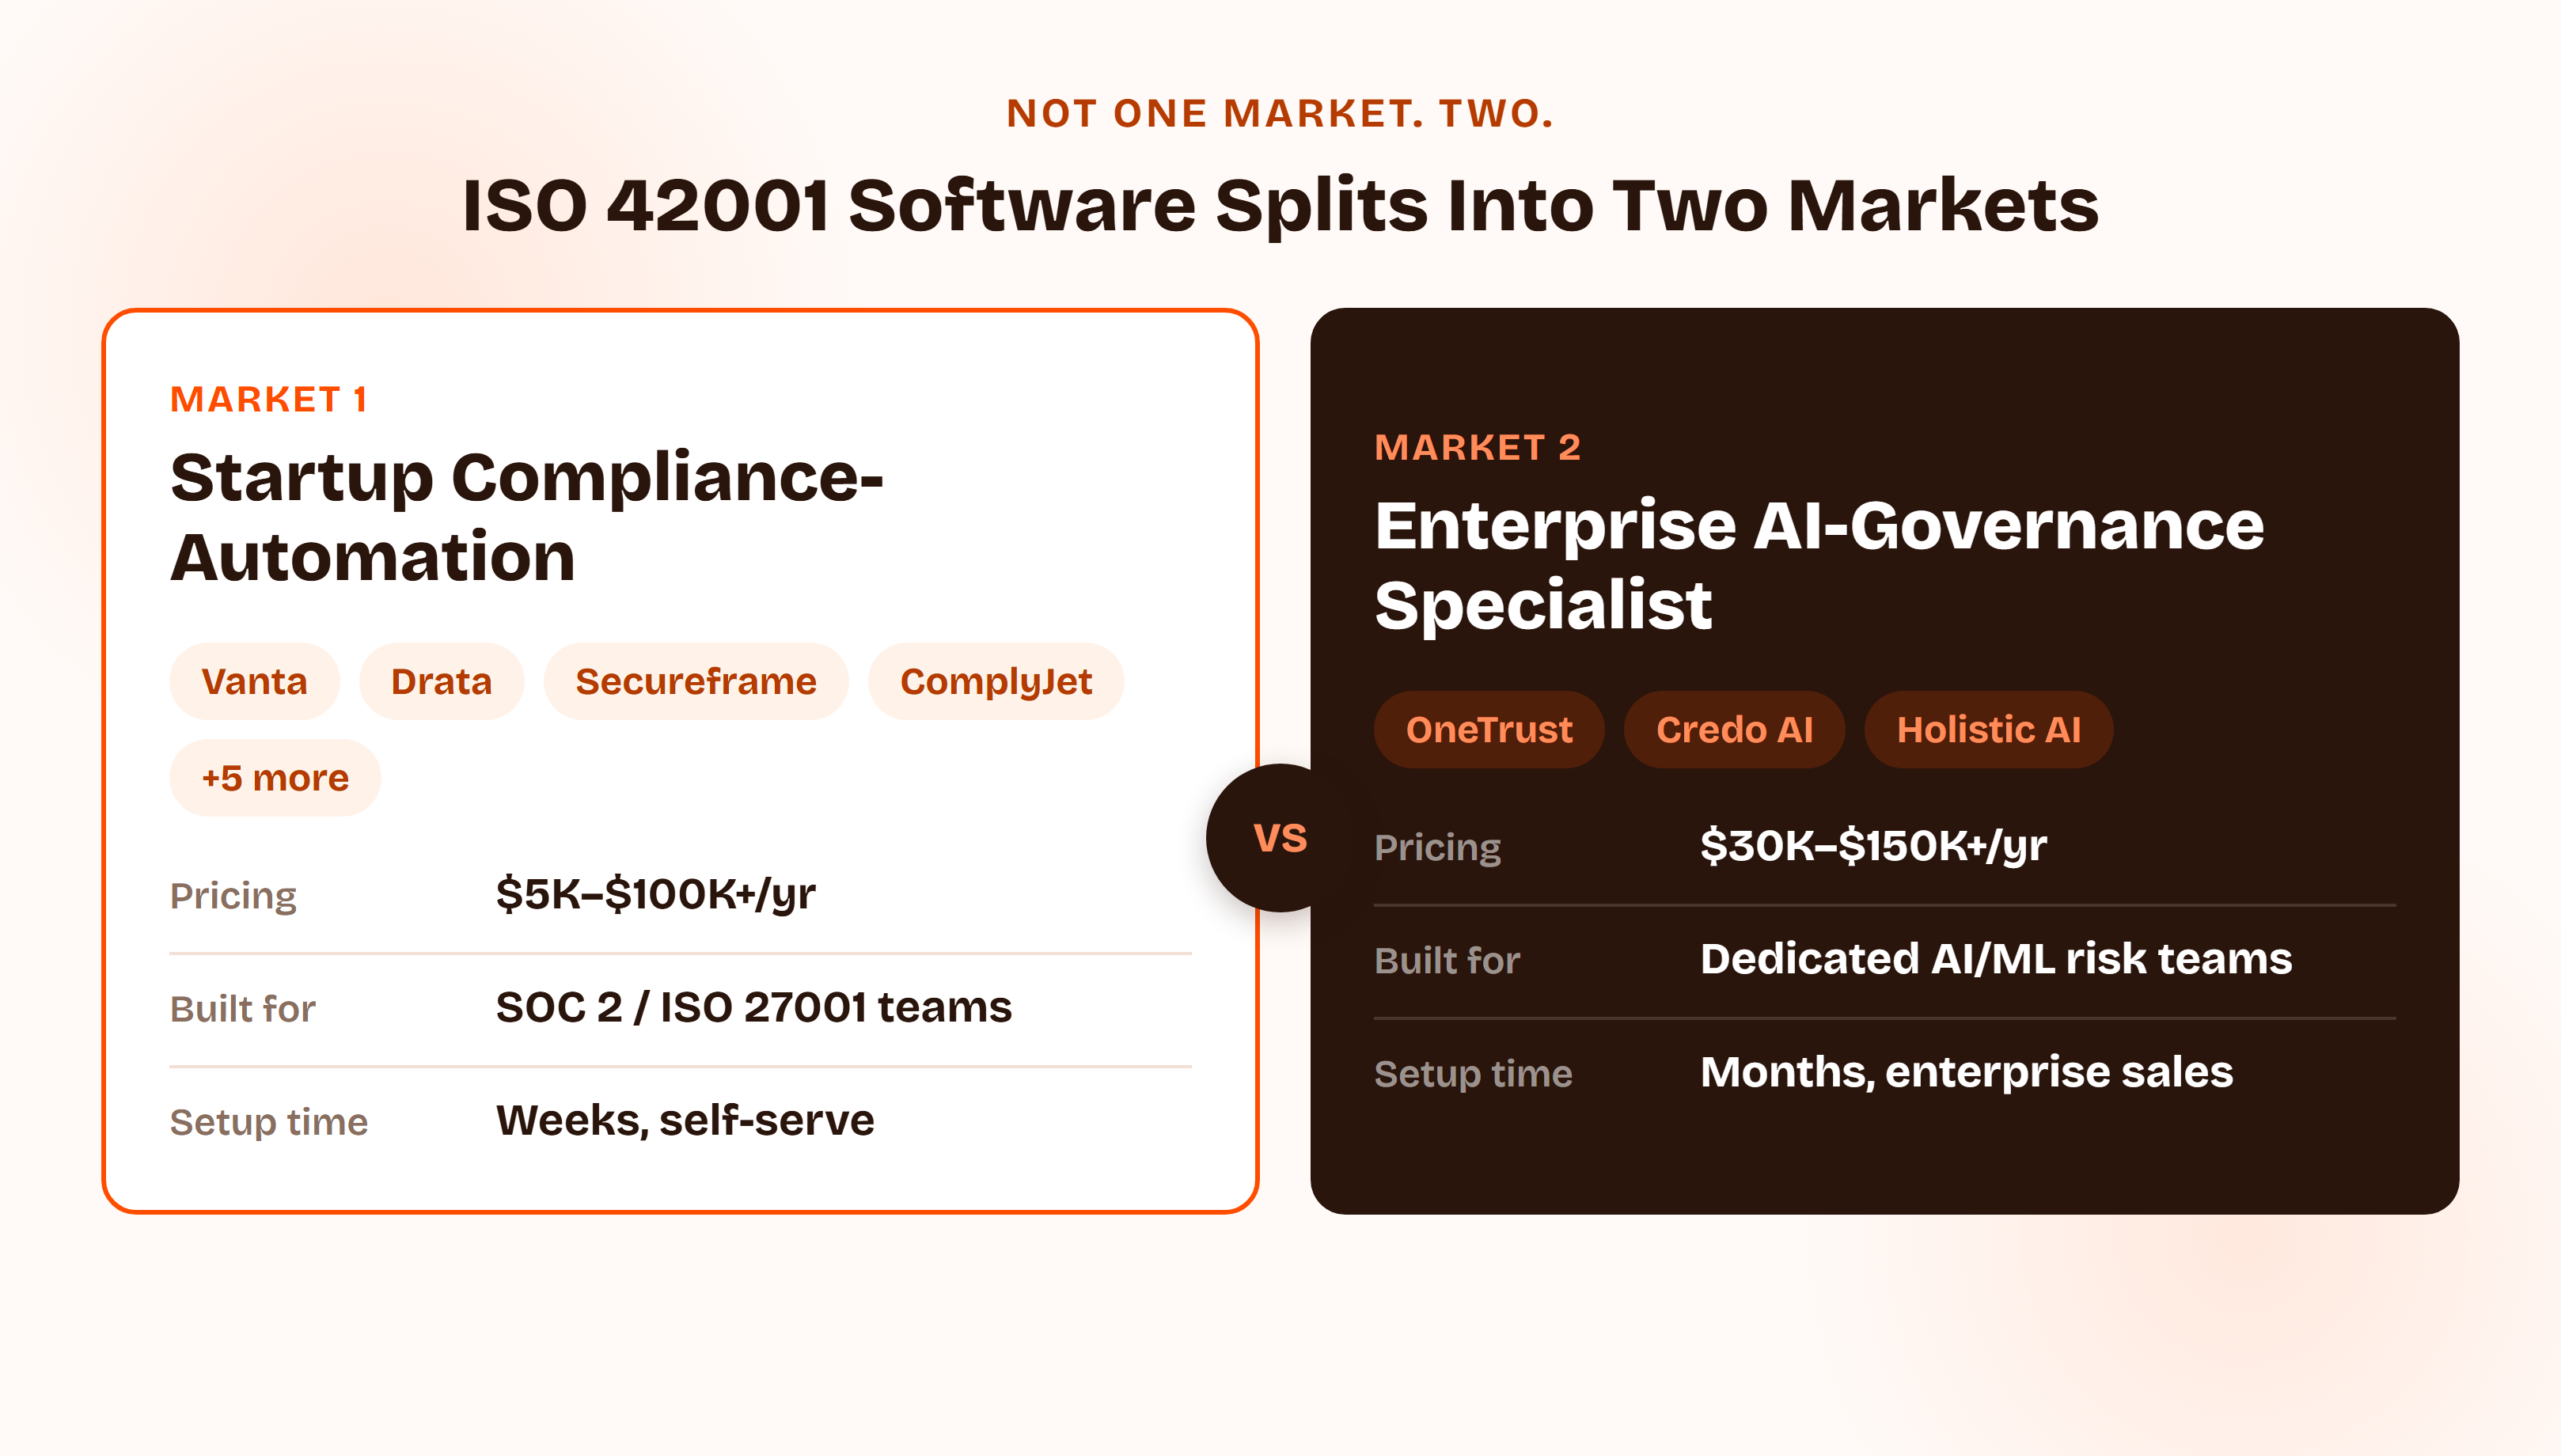
Here's the honest starting point, before any rankings: ISO 42001 software isn't one market. It's two, and they don't overlap as much as the marketing pages suggest. A handful of the compliance-automation platforms you already know from SOC 2 and ISO 27001 shopping — Vanta, Drata, Secureframe — added ISO 42001 as one more framework module.
Separately, a newer, genuinely enterprise-priced AI-governance specialist category — built around AI model and agent inventories, not general security evidence collection — has grown up fast around ISO 42001, the EU AI Act, and NIST's AI RMF. That split, not a single ranked list, is the frame this whole comparison runs on.
What Is ISO 42001 Compliance Software and AI Governance Compliance Software? Why It Splits Into Two Markets
ISO 42001 compliance software — also searched as AI governance compliance software — is the platform layer that operationalizes an AI Management System, or AIMS: the standard's governance, risk-assessment, and lifecycle controls for how an organization designs, develops, deploys, and monitors AI systems, mapped to ISO/IEC 42001:2023's clauses and its 38 Annex A controls across 9 objectives.
That's the mechanics. The structural reality that matters more is this: two genuinely different kinds of vendor have converged on the same search term. Startup-familiar compliance-automation platforms — Vanta, Drata, Secureframe, ComplyJet, Scrut Automation, Hyperproof, Sprinto, Scytale, ISMS.online — added ISO 42001 as one more framework module inside the same multi-framework evidence-collection engine they already run SOC 2 and ISO 27001 on.
Separately, a newer enterprise AI-governance specialist category — OneTrust, Credo AI, Holistic AI — has built entire platforms specifically around AI system and agent discovery, model risk scoring, and bias/safety testing, not general security compliance evidence. These aren't the same buy. One reviewer's third-party pricing estimate for Credo AI puts real enterprise contracts in the $30,000–$150,000+/year range — a different budget conversation entirely from a startup's first ISO 42001 push.
Not what this article is
This is a software comparison, not a framework explainer. For what ISO 42001 actually is, its 10-clause structure, and the Annex A control breakdown, read ComplyJet's ISO 42001 guide. This article picks up where that one leaves off: which platforms to actually buy.
Which Market Has the Best ISO 42001 Software for You?
Most readers who land on "best iso 42001 software" coming from a SOC 2 or ISO 27001 background actually want the compliance-automation category — a platform that runs ISO 42001 alongside the frameworks they already have, not a dedicated AI-governance suite built for a Fortune 500 AI/ML risk function with its own model-inventory team. But most existing "best AI governance software" content only covers the enterprise specialist category, because that's who's driving the loudest AI-governance marketing right now.
Knowing which market you're actually in before you start requesting demos saves real time and a genuinely different budget conversation. A five-figure annual compliance-automation add-on and a six-figure dedicated AI-governance platform solve related but different problems, even though both say "ISO 42001" on the page.
Worth Checking First
Is this really an ISO 42001 mandate, or a SOC 2/ISO 27001 AI-governance question in disguise?
If a customer's asking about your AI governance program as part of a SOC 2 or ISO 27001 review, not a dedicated ISO 42001 certification requirement, ComplyJet helps you build and evidence that AI-governance documentation as part of the audit you're already running.
How I Evaluated These 12 Best ISO 42001 Software Platforms (ISO 42001 Software Comparison Method)
I didn't rank these off a blog mention or a features-page skim. This ISO 42001 software comparison checked each platform's own current site directly for a real listing — a dedicated product page, a named framework in a live frameworks list, or explicit AIMS/ISO 42001 product content — not an educational blog post that merely explains what ISO 42001 is.
I looked at which market each platform actually belongs to, since that's the distinction most existing "best AI governance software" content skips entirely: startup-familiar compliance-automation platform, or dedicated enterprise AI-governance specialist. Where relevant, I checked whether ISO 42001 runs on the same connected program as an existing SOC 2 or ISO 27001 build.
I checked pricing transparency, and I looked for real AI-specific tooling — model/agent inventory, AI-specific risk scenarios, bias or safety testing — rather than general GRC evidence collection with an "AI" label added to a framework list.
ComplyJet is included in this comparison on the same terms as every other vendor here — checked for real, current support directly against complyjet.com/frameworks, not a blog mention or an assumption carried over from a sibling comparison.
I also checked, and excluded, two names that show up in adjacent "best compliance software" listicles. Thoropass's frameworks page was checked directly and names SOC 1/2, HIPAA, HITRUST, GDPR, NIST CSF 2.0, PCI DSS, CMMC, Cyber Essentials, CIS, and NYCRR 500 — no ISO 42001 or AI-governance framework anywhere.
Oneleet's frameworks page lists eight named frameworks (SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, CIS IG1, NIST 800-171, EU DORA) plus an unnamed custom bucket — ISO 42001 isn't among them.
Quick Comparison: 12 Best ISO 42001 Software Platforms at a Glance
| Tool | Best for | Pricing | Standout feature |
|---|---|---|---|
| Vanta | Startups running ISO 42001 on the same platform as SOC 2/ISO 27001 | Not public (est. $14K–$100K+/yr) | Dedicated ISO 42001 product page with AI-specific risk scenarios and a Vanta AI Agent |
| OneTrust | Enterprises needing a full AI-system discovery and governance platform | Not public, module-metered | Named a Visionary in Gartner's 2026 Magic Quadrant for AI Governance Platforms |
| Drata | Existing Drata customers adding ISO 42001 to a SOC 2/ISO 27001 program | Not public (est. $9.6K–$60K/yr) | ISO 42001 confirmed live on Drata's frameworks page |
| Secureframe | Startups wanting ISO 42001 grouped with other AI-specific frameworks | Not public (est. $7.5K–$70K+/yr) | Dedicated "AI frameworks" category on Secureframe's site |
| ComplyJet | Early-stage startups adding ISO 42001 to an existing SOC 2/ISO 27001 program | $5,000/yr (1 framework), $8,000/yr (2+) | Flat, publicly listed per-company pricing |
| Scrut Automation | Teams wanting a vendor that's itself gone through ISO 42001 certification | ~$15,000/yr (AWS Marketplace, ≤20 employees) | Scrut is itself ISO 42001 certified |
| Hyperproof | Multi-framework GRC teams managing ISO 42001 alongside many other standards | Not public | Out-of-the-box ISO 42001 template with ISO 27001/NIST CSF/NIST AI RMF cross-mapping |
| Sprinto | Teams wanting dedicated ISO 42001 content, not just a framework-list mention | Not public (est. $11.5K–$19.3K/yr) | Multiple dedicated ISO 42001 pages, built around the standard's 38 controls |
| Scytale | Existing Scytale customers wanting ISO 42001 on the same hands-on GRC relationship | Not public (tiered packages) | Confirmed live on Scytale's own frameworks page |
| ISMS.online | Teams wanting ISO 27001 + ISO 42001 documentation depth in one system | Not public, bespoke quote | Dedicated ISO 42001 page, G2 4.5/5, named a GRC Leader (Fall 2026) |
| Credo AI | Enterprises needing AI agent/model risk intelligence across a large AI estate | Not public (est. $30K–$150K+/yr) | Purpose-built AI registry with shadow-AI detection |
| Holistic AI | Enterprises needing bias, safety, and fairness testing alongside governance | Not public | 40+ automated tests for bias, hallucination, privacy, and robustness |
The 12 Best ISO 42001 Software Platforms in 2026
1. Vanta
Vanta is the clearest fit on this list for a startup that already runs SOC 2 or ISO 27001 and needs ISO 42001 without adding a second vendor relationship. Its dedicated ISO 42001 product page maps the standard directly, with document and policy templates, mapped controls, and AI-specific risk scenarios built in rather than left for you to construct from scratch.
Vanta pitches this around its AI Agent, which can summarize policies, flag evidence gaps, and speed up remediation — plus adaptive scoping, so a team can define and adjust which AI systems and people actually fall inside ISO 42001's boundary as their AI footprint grows. Evidence reuses across related standards, including a stated 50% control alignment with the EU AI Act, plus NIST AI RMF and CPS 234.
The tradeoff is the one every "best compliance software" list eventually lands on with Vanta: nothing here comes with a public number attached, and the gap between the quote you sign at and the one you renew at is a documented pattern across reviewers, not a rumor.
Key features:
- Dedicated ISO 42001 product page with mapped controls and AI-specific risk scenarios
- Vanta AI Agent for policy summarization and evidence-gap flagging
- Adaptive scoping for which AI systems and people fall under ISO 42001
- Evidence cross-mapping to the EU AI Act (~50% alignment), NIST AI RMF, and CPS 234
- Hourly automated control testing across 400+ integrations
Pros
- Purpose-built ISO 42001 product page and workflow, not a bolt-on framework listing
- Fastest path to ISO 42001 for a team already running SOC 2 or ISO 27001 on Vanta
- Genuine cross-mapping to the EU AI Act and NIST AI RMF, useful if you're facing more than one AI regulation at once
- Largest auditor ecosystem of any vendor on this list
Cons
- No public pricing anywhere; third-party deal data puts real contracts anywhere from roughly $14,000 to $100,000+ a year
- Documented pattern of steep year-two renewal increases
- No dedicated AI model/agent inventory or bias-testing tooling the way Credo AI or Holistic AI have
- Requires a monitoring agent install some engineering teams push back on
Pricing: Not public. Contact sales for a quote; third-party estimates and AWS Marketplace list prices put real contracts in the $14,000–$100,000+/year range depending on frameworks and headcount.
Best for: SaaS teams that already run SOC 2 or ISO 27001 and want ISO 42001 added to the same connected program rather than a separate vendor relationship.
2. OneTrust
OneTrust is the enterprise AI-governance specialist of this list, and it's the platform genuinely built to discover, inventory, and govern AI at scale — models, agents, datasets, vendors, and projects brought into one program center, with continuous discovery of AI systems and agents rather than a static, self-reported inventory.
OneTrust's AI governance module explicitly builds assessments from EU AI Act, NIST AI RMF, and ISO 42001 templates, and the company was named a Visionary in the inaugural 2026 Gartner Magic Quadrant for AI Governance Platforms — a genuine third-party recognition, not a self-issued claim. As of March 2026, OneTrust added continuous AI-agent discovery, a prebuilt AI policy library, and real-time guardrail enforcement that can inspect and limit personal-data exposure from AI systems as risks arise.
What this isn't is a lightweight startup buy. This is enterprise privacy-and-risk-platform infrastructure, priced and scoped for a company with a dedicated AI governance or privacy function — not a 20-person startup's first AI compliance push, and it has no native SOC 2/ISO 27001 automation core, so a startup pursuing all three would be pairing it with a separate compliance-automation platform.
Key features:
- Continuous discovery of AI systems, models, agents, datasets, and vendors
- Assessments built from EU AI Act, NIST AI RMF, and ISO 42001 templates
- Real-time guardrail enforcement that can block or limit AI-driven data exposure
- Prebuilt AI policy library (added March 2026)
Pros
- Independently recognized as a Visionary in Gartner's 2026 AI Governance Platforms Magic Quadrant
- Genuine, continuous AI system/agent discovery — not a manual, self-reported inventory
- Real-time guardrail enforcement, a level of active risk control most vendors on this list don't offer
Cons
- No SOC 2/ISO 27001 automation core; a startup pursuing all three would need a separate platform for those
- Pricing is module-metered and entirely opaque, adding real quoting complexity
- Sized and priced for a dedicated AI-governance or privacy function most early-stage startups don't have yet
Pricing: Not public. Module-based, metered pricing; contact sales for a quote.
Best for: Larger or scaling companies with a real AI estate — multiple models, agents, or vendors — that need continuous AI discovery and active guardrail enforcement, not just framework-level evidence collection.
3. Drata
Drata's live frameworks page confirms ISO 42001 plainly: "Govern responsible AI with a standardized management system." That's a real, current, in-product listing, not an inferred claim from a blog post.
Where Drata earns its ranking is everything around the framework, not the framework itself. It has one of the widest integration libraries on this list — 300+ connections — and a support reputation that shows up consistently across reviews as the thing customers mention unprompted. If your evaluation weighs "will someone answer me fast when something breaks" as heavily as framework depth, that's a real point in Drata's favor.
What I couldn't find is any ISO 42001-specific customer story, dedicated landing page, or AI-specific risk tooling beyond the general framework listing — a real gap worth knowing about, not a dealbreaker on its own for a team that mainly wants ISO 42001 to run on the same connected program as an existing SOC 2 or ISO 27001 build.
Key features:
- ISO 42001 listed and described directly on Drata's live frameworks page
- 300+ integrations, one of the deepest libraries in this comparison
- Broad named framework list (30+, including NIST AI RMF)
- Agentic AI for vendor risk management
Pros
- Highest-volume, most consistently positive support reputation across reviewers
- Very wide integration coverage reduces manual evidence gaps
- Strong general framework breadth beyond just ISO 42001
Cons
- No ISO 42001-specific customer proof point found on its own marketing pages
- Pricing fully gated behind a sales call; documented renewal increases reported by customers
- No AI-specific risk-scenario library or model/agent inventory beyond general framework mapping
Pricing: Not public. Contact sales; third-party deal data shows observed contracts from roughly $9,600 to $60,000/year.
Best for: Mid-market teams that want the deepest integration library and the strongest support reputation, and for whom ISO 42001 specifically isn't the primary reason they're buying.
4. Secureframe
Secureframe treats ISO 42001 as exactly what it is structurally — an AI-specific framework — and groups it that way on its site under a dedicated "AI frameworks" category: "Secureframe helps organizations comply with ISO 42001, and manage responsible development and use of AI systems."
That categorization choice is honest, and it's also the clearest signal of what you're actually buying: ISO 42001 on Secureframe isn't a first-class category with dedicated tooling the way it is on Vanta or OneTrust — it's a well-organized addition on top of a strong SOC 2/ISO 27001 core. For a startup that's already decided to run all three frameworks on one platform, that's a reasonable tradeoff, not a red flag.
I found no ISO 42001-specific customer story or standalone product page beyond the AI-frameworks category listing — the same class of gap Drata has, worth knowing before you assume the marketing depth matches SOC 2's.
Key features:
- Dedicated "AI frameworks" category including ISO 42001
- 35+ supported frameworks total on one platform
- Dedicated compliance manager plus human auditor support included
- Automated evidence collection tied to the same controls that back SOC 2/ISO 27001
Pros
- Honest categorization of ISO 42001 alongside other AI-specific frameworks, not buried in a generic list
- Human support from actual auditors, repeatedly cited as a strength in reviews
- Strong integration coverage across cloud and dev tooling
Cons
- ISO 42001 is positioned as a category addition, not a first-class product with its own dedicated tooling
- Pricing entirely opaque; third-party estimates range from roughly $7,500/year for small startups to $70,000+/year for larger teams
- No AI model/agent inventory or bias-testing tooling
Pricing: Not public. Contact sales for a quote; third-party estimates start around $7,500/year for a small single-framework build.
Best for: Startups already committed to SOC 2 and ISO 27001 who want ISO 42001 added on the same platform, organized clearly alongside other AI-specific frameworks.
5. ComplyJet
ComplyJet is the fit for an early-stage SaaS or AI-product startup that already runs, or is about to run, SOC 2 or ISO 27001 and wants ISO 42001 added to that same connected program instead of opening a second vendor relationship just for AI governance.
ISO 42001 is confirmed live on complyjet.com/frameworks, described as the "international standard for AI management systems," alongside NIST AI RMF and the EU AI Act — joining ComplyJet's 25+ framework library that also includes SOC 2, ISO 27001, HIPAA, GDPR, and PCI DSS.
Where ComplyJet differs from Vanta, OneTrust, and the other vendors here with dedicated AI-governance depth is pricing and process, not AI-specific tooling. Pricing is flat and publicly listed — $5,000/year for one framework, $8,000/year for two or more, per company rather than per seat — so it doesn't creep up as headcount grows within the plan, and it stays predictable as a team grows from five people to thirty or forty.
Every other vendor in this comparison requires a sales call before you see a number; ComplyJet is the one that doesn't.
The rest of the pitch is the same connected-program story that runs through the rest of this list. Evidence collected for an existing SOC 2 or ISO 27001 audit — access logs, vendor reviews, policy sign-offs — gets reused against ISO 42001's overlapping governance and risk-management requirements instead of managed a second time in a separate system.
That's paired with AI-assisted drafting help for the AI-governance documentation itself, white-glove support through setup, and a Trust Center to share audit-ready evidence with the enterprise buyer whose questionnaire likely triggered this search in the first place.
Key features:
- ISO 42001 confirmed live on complyjet.com/frameworks, running on the same connected program as an existing SOC 2 or ISO 27001 build
- Flat, publicly listed per-company pricing — no sales call required to see a number
- AI-assisted drafting for AI-governance policy and program documentation
- Evidence reuse across overlapping SOC 2/ISO 27001/ISO 42001 controls instead of duplicate collection
- Trust Center for sharing audit-ready evidence directly with customers
- White-glove implementation support, 350+ integrations
Pros
- One of a small number of vendors on this list with a publicly listed price, and the only one with a truly flat, per-company number
- Fastest path to ISO 42001 for a startup already running SOC 2 or ISO 27001 on ComplyJet
- Pricing framed as a growth-journey guarantee — stays flat as headcount grows within the plan, not a hard cutoff
- White-glove support model, a real differentiator against fully self-serve platforms for a team doing this for the first time
Cons
- No dedicated ISO 42001 landing page or standalone AI-governance marketing content the way Vanta, OneTrust, or ISMS.online have built
- No AI-specific risk-scenario library, model/agent inventory, or bias and safety testing the way Credo AI, Holistic AI, or OneTrust offer — those are genuinely different, deeper products in that specific dimension
- Smaller company with a shorter AI-framework track record than Vanta or Drata
- No independently verifiable G2 rating found during this research
Pricing: $5,000/year for one framework, $8,000/year for two or more, flat per company. Publicly listed, no sales call required for a base number.
Best for: Early-stage SaaS or AI-product startups already running, or about to run, SOC 2 or ISO 27001 on ComplyJet that want ISO 42001 added to the same connected, flat-priced program — not teams that need dedicated AI model/agent risk tooling.
Flat, Connected Pricing
Want ISO 42001 on the same program as SOC 2 or ISO 27001?
ComplyJet runs ISO 42001 on the same connected program as an existing SOC 2 or ISO 27001 build — flat, publicly listed pricing, no sales call required to see a number. See ComplyJet's full entry above, or read does SOC 2 cover AI for the underlying adjacency either way.
6. Scrut Automation
Scrut is worth noting for something no other vendor on this list can claim: it's itself ISO 42001 certified. Its own site states it "never uses your data to train shared models" and is "opt-in and configurable," positioning its own certification as proof the platform can be trusted with the AI governance work it's also selling — a real, checkable credibility marker.
Beyond that, Scrut offers a systematic framework to navigate AI Management System (AIMS) requirements aligned with ISO/IEC 42001:2023's Plan-Do-Check-Act structure, with its "Teammates" feature detecting evidence from your existing tech stack and mapping controls across 70+ frameworks — a real time saver for a team managing several overlapping standards at once, not just ISO 42001 in isolation.
What's less clear is standalone ISO 42001 pricing. Scrut's general frameworks page returned a 404 on direct check, and AWS Marketplace lists its broader Compliance Automation module at a flat $15,000 for 12 months for organizations up to 20 employees — a real, sourced figure, but not confirmed as ISO-42001-specific.
Key features:
- Scrut is itself ISO 42001 certified, not just selling support for it
- Systematic AIMS framework aligned to the standard's Plan-Do-Check-Act structure
- Evidence detection and control mapping across 70+ frameworks
- Explicit, publicly stated data-use policy (no training on customer data without opt-in)
Pros
- Itself ISO 42001 certified — a genuine, checkable credibility marker, not a marketing claim
- Broad cross-framework control mapping (70+ frameworks) useful for teams juggling several standards
- Very high review scores across G2 and Capterra
Cons
- General frameworks page 404'd on direct check; ISO 42001-specific pricing wasn't independently confirmed, only the broader Compliance Automation module figure
- No AI-specific risk-scenario library or model/agent inventory beyond general control mapping
- Reviewers cite a learning curve on advanced configuration
Pricing: Not public specifically for ISO 42001. AWS Marketplace lists Scrut's Compliance Automation module at $15,000 per 12 months for organizations up to 20 employees, plus a separate onboarding fee.
Best for: Multi-framework shops that want a vendor with genuine, first-party ISO 42001 credibility and broad cross-framework mapping across many standards at once.
7. Hyperproof
Hyperproof's framework library is one of the largest on this list — 160+ frameworks — and it ships an out-of-the-box ISO 42001 template built specifically so a team can start managing AI risk quickly rather than building a program from a blank page.
Its actual strength, consistent with how it shows up on ComplyJet's other listicles, is cross-framework control mapping rather than depth on any single standard: once ISO 42001 is implemented, Hyperproof shows how those controls map to ISO 27001 and NIST CSF, and its Jumpstart feature lets a team map existing ISO 42001 controls across NIST AI RMF too, avoiding duplicated work.
Hyperproof actively supports NIST AI RMF, ISO 42001, and the EU AI Act as live frameworks — a genuinely broad AI-risk surface for a single platform.
That breadth-first design carries the same tradeoff here it does elsewhere on this list: Hyperproof is consistently described by reviewers as less intuitive for first-time users, with a real setup learning curve, and I found no ISO 42001-specific customer story or AI-specific risk-scenario library beyond the general framework and cross-mapping engine.
Key features:
- Out-of-the-box ISO 42001 framework template
- Cross-mapping between ISO 42001, ISO 27001, NIST CSF, and NIST AI RMF
- Active support for NIST AI RMF and the EU AI Act alongside ISO 42001
- Task-assignment and collaboration tooling for cross-team compliance work
Pros
- Broadest framework coverage of any vendor here, reducing the odds of hitting an unsupported standard later
- Genuine, active cross-mapping across ISO 42001, ISO 27001, NIST CSF, and NIST AI RMF
- Out-of-the-box template reduces the blank-page problem for a first AI-governance build
Cons
- No dedicated ISO 42001 product page or case study found beyond the general framework template
- UI and initial setup consistently described as less intuitive than Vanta or Drata
- No public pricing; no dollar figures shown anywhere on its pricing page
Pricing: Not public. No tiers or figures shown; the pricing page routes to demo or proposal requests only.
Best for: Larger or multi-framework organizations that need ISO 42001 mapped against several other overlapping standards — ISO 27001, NIST CSF, NIST AI RMF — at once.
8. Sprinto
Sprinto has built out more dedicated ISO 42001 content than most vendors on this list — multiple standalone pages, not a single frameworks-list mention, positioning itself as "an AI risk and compliance operating system, built for ISO 42001." That's a real, specific product claim, and it's backed by content built around the standard's actual 38 controls rather than a generic compliance pitch with "AI" appended.
Sprinto's pitch centers on operationalizing ISO 42001's requirements as live, trackable, automated systems — risk registers, lifecycle oversight spanning AI design through decommissioning, vendor due diligence, and policy enforcement — rather than a static document set. That lifecycle framing (design, development, deployment, decommissioning) is more AI-specific than most of the startup-compliance vendors on this list manage.
What I couldn't independently confirm is Sprinto's general pricing page, which returned an access error on direct check — third-party deal data is the best available estimate here, same limitation this comparison flags honestly wherever a vendor's own numbers aren't reachable.
Key features:
- Multiple dedicated ISO 42001 pages built around the standard's 38 controls
- AI-lifecycle risk framing spanning design, development, deployment, and decommissioning
- Risk registers and vendor due diligence tooling built for AI-specific risk
- Cross-framework evidence reuse across GDPR, SOC 2, and other supported standards
Pros
- More dedicated ISO 42001 content than most vendors on this list, built around the standard's real 38-control structure
- AI-lifecycle-specific risk framing, not just general GRC evidence collection
- Very high satisfaction scores across G2 and Capterra
Cons
- General pricing page returned an access error on direct check; only third-party estimates could be sourced
- Pricing fully gated behind a sales call; some reviewers cite cost as steep for smaller companies
- No confirmed AI model/agent inventory or bias-testing tooling beyond risk-register and policy features
Pricing: Not public. Contact sales; third-party deal data shows a broader estimated range of roughly $11,500–$19,300/year depending on tier.
Best for: Startups wanting genuinely AI-lifecycle-specific ISO 42001 content and risk tooling, not just a framework added to a general compliance dashboard.
9. Scytale
Scytale confirms ISO 42001 directly on its live all-frameworks page, with a real, current description: "Defines requirements for managing AI systems responsibly, covering governance, risk, and ethical use of AI." That's the bar this comparison holds every vendor to — a current, in-product listing, not an inferred claim.
Scytale's identity is built around hands-on GRC-expert support layered on top of automation, and reviewers notice it enough to name specific staff members by name in reviews — not something people bother doing when support is merely adequate. Its broader framework library covers 40+ standards, including SOC 2, ISO 27001, PCI DSS, and GDPR alongside ISO 42001.
What I couldn't find is anything ISO 42001-specific beyond that one frameworks-page listing — no dedicated product page, no case study naming it, no AI-specific risk-scenario description. That doesn't mean the support isn't real; it means the depth is currently unverified beyond the base listing, worth knowing before assuming it's as built out as SOC 2 or ISO 27001 are on the same platform.
Key features:
- ISO 42001 listed directly under Scytale's live frameworks catalog
- 40+ frameworks automated, including SOC 2, ISO 27001, and GDPR
- AI GRC Agent for automated evidence collection
- Hands-on GRC-expert model layered on top of automation
Pros
- Genuine, current, direct confirmation of ISO 42001 support, not an inferred or blog-only mention
- Strong, consistently positive support reputation with specific staff named in reviews
- Broad framework automation (40+) beyond just this one standard
Cons
- No dedicated ISO 42001 product page or case study found; depth beyond the base framework listing is unverified
- Pricing entirely opaque even by this list's standard — three unpriced tiers plus separate paid consulting add-ons
- Primarily known and marketed as a SOC 2/ISO 27001 specialist, so ISO 42001 reads as a secondary addition
Pricing: Not public. Tiered packages (Build, Scale, Enterprise) with additional consulting add-ons; contact sales or request a demo for a quote.
Best for: Teams that already like Scytale's hands-on GRC-expert model for SOC 2 or ISO 27001 and want ISO 42001 added to that same relationship.
10. ISMS.online
ISMS.online is one of only two vendors on this list with a dedicated, named ISO 42001 product page — pre-configured templates aligned to the standard's requirements, dynamic risk management tailored for AI-specific risks, and document management built specifically to organize certification materials, with "built-in workflows to help you govern AI responsibly."
ISMS.online positions ISO 42001 as part of a broader compliance platform — it supports over 100 standards and regulations — and the standard gets prominent placement in its solutions menu alongside ISO 27001, SOC 2, and NIS 2. Its G2 rating sits at 4.5/5, and it was named a Leader in Governance, Risk & Compliance for Fall 2026, a real independent recognition rather than a self-issued badge.
Where ISMS.online differs from Vanta or the compliance-automation platforms is positioning: it's an ISO-management-system documentation specialist first, not a broad multi-framework automation platform, and it doesn't have hourly automated evidence collection the way SOC 2-native platforms do.
Key features:
- Dedicated ISO 42001 product page with pre-configured templates
- Dynamic risk management specifically tailored for AI-specific risks
- Document management for certification materials
- 100+ supported standards and regulations in one connected system
Pros
- One of only two vendors here with a purpose-built ISO 42001 product page, not a framework-list mention
- Independently recognized as a GRC Leader (Fall 2026), G2 rating of 4.5/5
- Dynamic, AI-specific risk-management tooling, not generic risk templates relabeled
Cons
- No hourly automated evidence collection the way SOC 2-native platforms are built around
- Pricing is bespoke and quote-only, adding sales friction versus more self-serve competitors
- No confirmed multi-framework breadth on the SOC 2/ISO 27001 side the way Vanta or Hyperproof offer
Pricing: Not public. Bespoke, pay-for-what-you-use model based on selected frameworks and modules; requires a quote form or demo.
Best for: Teams that want deep ISO 42001/ISO 27001 documentation structure and audit-prep depth in one system, more than fast, self-serve, integration-heavy automation.
11. Credo AI
Credo AI is the first of two true AI-governance specialists on this list, and it's built for a different problem entirely than the startup-compliance platforms above it: discovering, cataloging, and governing an organization's full AI estate — agents, models, applications, and vendors — with an "AI Registry" that includes shadow-AI detection, plus a purpose-built agentic risk and control library for tool misuse, scope drift, and inter-agent risk.
Credo AI explicitly supports EU AI Act, NIST AI RMF, and ISO 42001 through pre-built policy packs it describes as developed by "the team in the room where AI governance standards are made" — a claim worth taking with appropriate skepticism as marketing copy, but the framework support itself is real and specific, not vague. The company has real third-party recognition, named a Leader by Forrester and a Cool Vendor by Gartner.
The honest limitation is scale and price. Third-party pricing estimates put real Credo AI contracts in the $30,000–$150,000+/year range, squarely enterprise territory, and reviewers note that configuring custom policy packs against complex internal enterprise hierarchies takes real time and training — this isn't a lightweight first buy for a startup's first ISO 42001 push.
Key features:
- AI Registry cataloging agents, models, applications, and vendors, including shadow-AI detection
- Purpose-built agentic risk and control library for tool misuse, scope drift, and inter-agent risk
- Pre-built policy packs mapped to EU AI Act, NIST AI RMF, and ISO 42001
- Policy engine for automating compliance workflows and evidence recording
Pros
- Genuine AI-specific inventory tooling (agents, models, shadow AI) none of the startup-compliance platforms on this list offer
- Real third-party recognition (Forrester Leader, Gartner Cool Vendor)
- Explicit, specific framework support (EU AI Act, NIST AI RMF, ISO 42001), not a vague AI-governance pitch
Cons
- Third-party pricing estimates put real contracts at $30,000-$150,000+/year — well outside a typical early-stage startup's compliance budget
- No SOC 2/ISO 27001 automation core; would run alongside a separate compliance platform, not replace one
- Reviewers note real setup/configuration time for complex enterprise policy hierarchies
Pricing: Not public. Third-party pricing estimates (sourced to co-aims.com) put real contracts in the $30,000–$150,000+/year range, plus implementation costs.
Best for: Enterprises with a real, sprawling AI estate — many models, agents, and AI vendors in production — that need active discovery and risk scoring across all of it, not a startup buying its first ISO 42001 program.
12. Holistic AI
Holistic AI is the second dedicated AI-governance specialist on this list, and its differentiator is testing depth: 40+ automated tests for bias, hallucination, privacy, and robustness, layered under a three-part platform — Identify (a living AI inventory across cloud, code, and SaaS), Protect (the bias/safety/security testing itself), and Enforce (policy application and automated compliance documentation).
Its controls are explicitly mapped to the EU AI Act, NIST AI RMF, and ISO/IEC 42001 — real, specific framework coverage, not a generic "we help with AI compliance" claim — and the platform states EU AI Act penalties (up to €35M) directly on its own site as part of the case for why this testing depth matters.
Like Credo AI, this is enterprise AI/ML-risk infrastructure, not a startup's first compliance buy. No public pricing exists anywhere on the site, and there's no SOC 2/ISO 27001 automation core — the fit here is a company that already has, or is actively building, models and AI products serious enough to need dedicated bias and safety testing, not just governance documentation.
Key features:
- 40+ automated tests for bias, hallucination, privacy, and robustness
- Living AI inventory across cloud, code, and SaaS (Identify)
- Policy enforcement with automated audit-trail documentation (Enforce)
- Controls explicitly mapped to EU AI Act, NIST AI RMF, and ISO/IEC 42001
Pros
- Deepest confirmed bias/safety/fairness testing of any vendor in this comparison — a genuinely different capability than framework-evidence automation
- Explicit, specific mapping to EU AI Act, NIST AI RMF, and ISO 42001 controls
- Living AI inventory across cloud, code, and SaaS, not a manual spreadsheet
Cons
- No public pricing anywhere on its own site; no third-party estimate could be independently confirmed for this research
- No SOC 2/ISO 27001 automation core; a startup pursuing all three would need a separate platform
- Built and positioned for enterprise AI/ML risk teams, not a first-time buyer's ISO 42001 program
Pricing: Not public. Custom, tiered enterprise pricing; contact sales for a quote.
Best for: Companies with real production AI systems that need dedicated bias, safety, and fairness testing alongside AI-governance documentation, not just framework-level evidence collection.
How to Choose ISO 42001 Compliance Software (Platforms Supporting ISO 42001 and ISO 27001)
This section covers how to choose ISO 42001 compliance software based on where you're actually starting from, not a generic checklist. If you take one thing from this guide, make it the market question below — it decides everything else.
Do You Actually Need Dedicated AI-Governance Software, or Is This a SOC 2/ISO 27001 AI-Risk Question in Disguise?
Start here, honestly, before shopping. If the trigger was a single questionnaire line asking about your AI governance program as part of a broader SOC 2 or ISO 27001 review — not a customer or regulator specifically requiring ISO 42001 certification — you may not need dedicated AIMS software at all yet.
A well-documented AI governance policy, evidenced inside the audit you're already running, often answers the question that actually got asked. ComplyJet's own does SOC 2 cover AI and AI governance policy guides cover that path directly.
If ISO 42001 certification itself is the explicit requirement — a specific customer contract clause, an investor or enterprise-due-diligence mandate, or a genuine strategic decision to certify — then you're in the market this article covers, and the rest of this section applies directly.
Startup Compliance-Automation Fit vs. Enterprise AI-Governance-Specialist Fit
This is the single most important filter on this list, and it's a genuine version of the "smart choice vs. safe choice" question that runs through every buying decision in this category. Vanta, Drata, Secureframe, ComplyJet, Scrut, Hyperproof, Sprinto, Scytale, and ISMS.online are built by and for the same startup-compliance buyer who's already evaluating SOC 2 and ISO 27001 platforms — reasonable pricing relative to company size, fast setup, self-serve or lightly-guided onboarding.
OneTrust, Credo AI, and Holistic AI are a different species of vendor. They're built for organizations with a dedicated AI/ML risk or privacy function, sized and priced accordingly — tens to well over a hundred thousand dollars a year, real setup and configuration time. None of that makes them worse software. It makes them the wrong shop for a 30-person SaaS startup buying its first ISO 42001 program.
Do You Need ISO 42001 on the Same Connected Program as an Existing SOC 2/ISO 27001 Build?
If you already run SOC 2 or ISO 27001 on a compliance-automation platform, check first whether that platform — or one of the confirmed ISO-42001-capable ones here — can run ISO 42001 alongside it before evaluating a completely separate AI-governance suite. Shared evidence and a single vendor relationship is usually the faster, cheaper path when it's available.
Reality check
Two names that show up in other ComplyJet compliance-automation listicles — Thoropass and Oneleet — do not currently support ISO 42001, confirmed by checking their own frameworks pages directly. If your platform isn't one of the nine confirmed here, you're choosing between adding a second vendor or waiting for your current one to build it.
The Best ISO 42001 Software Platforms Supporting ISO 42001 and ISO 27001 on One Connected Program
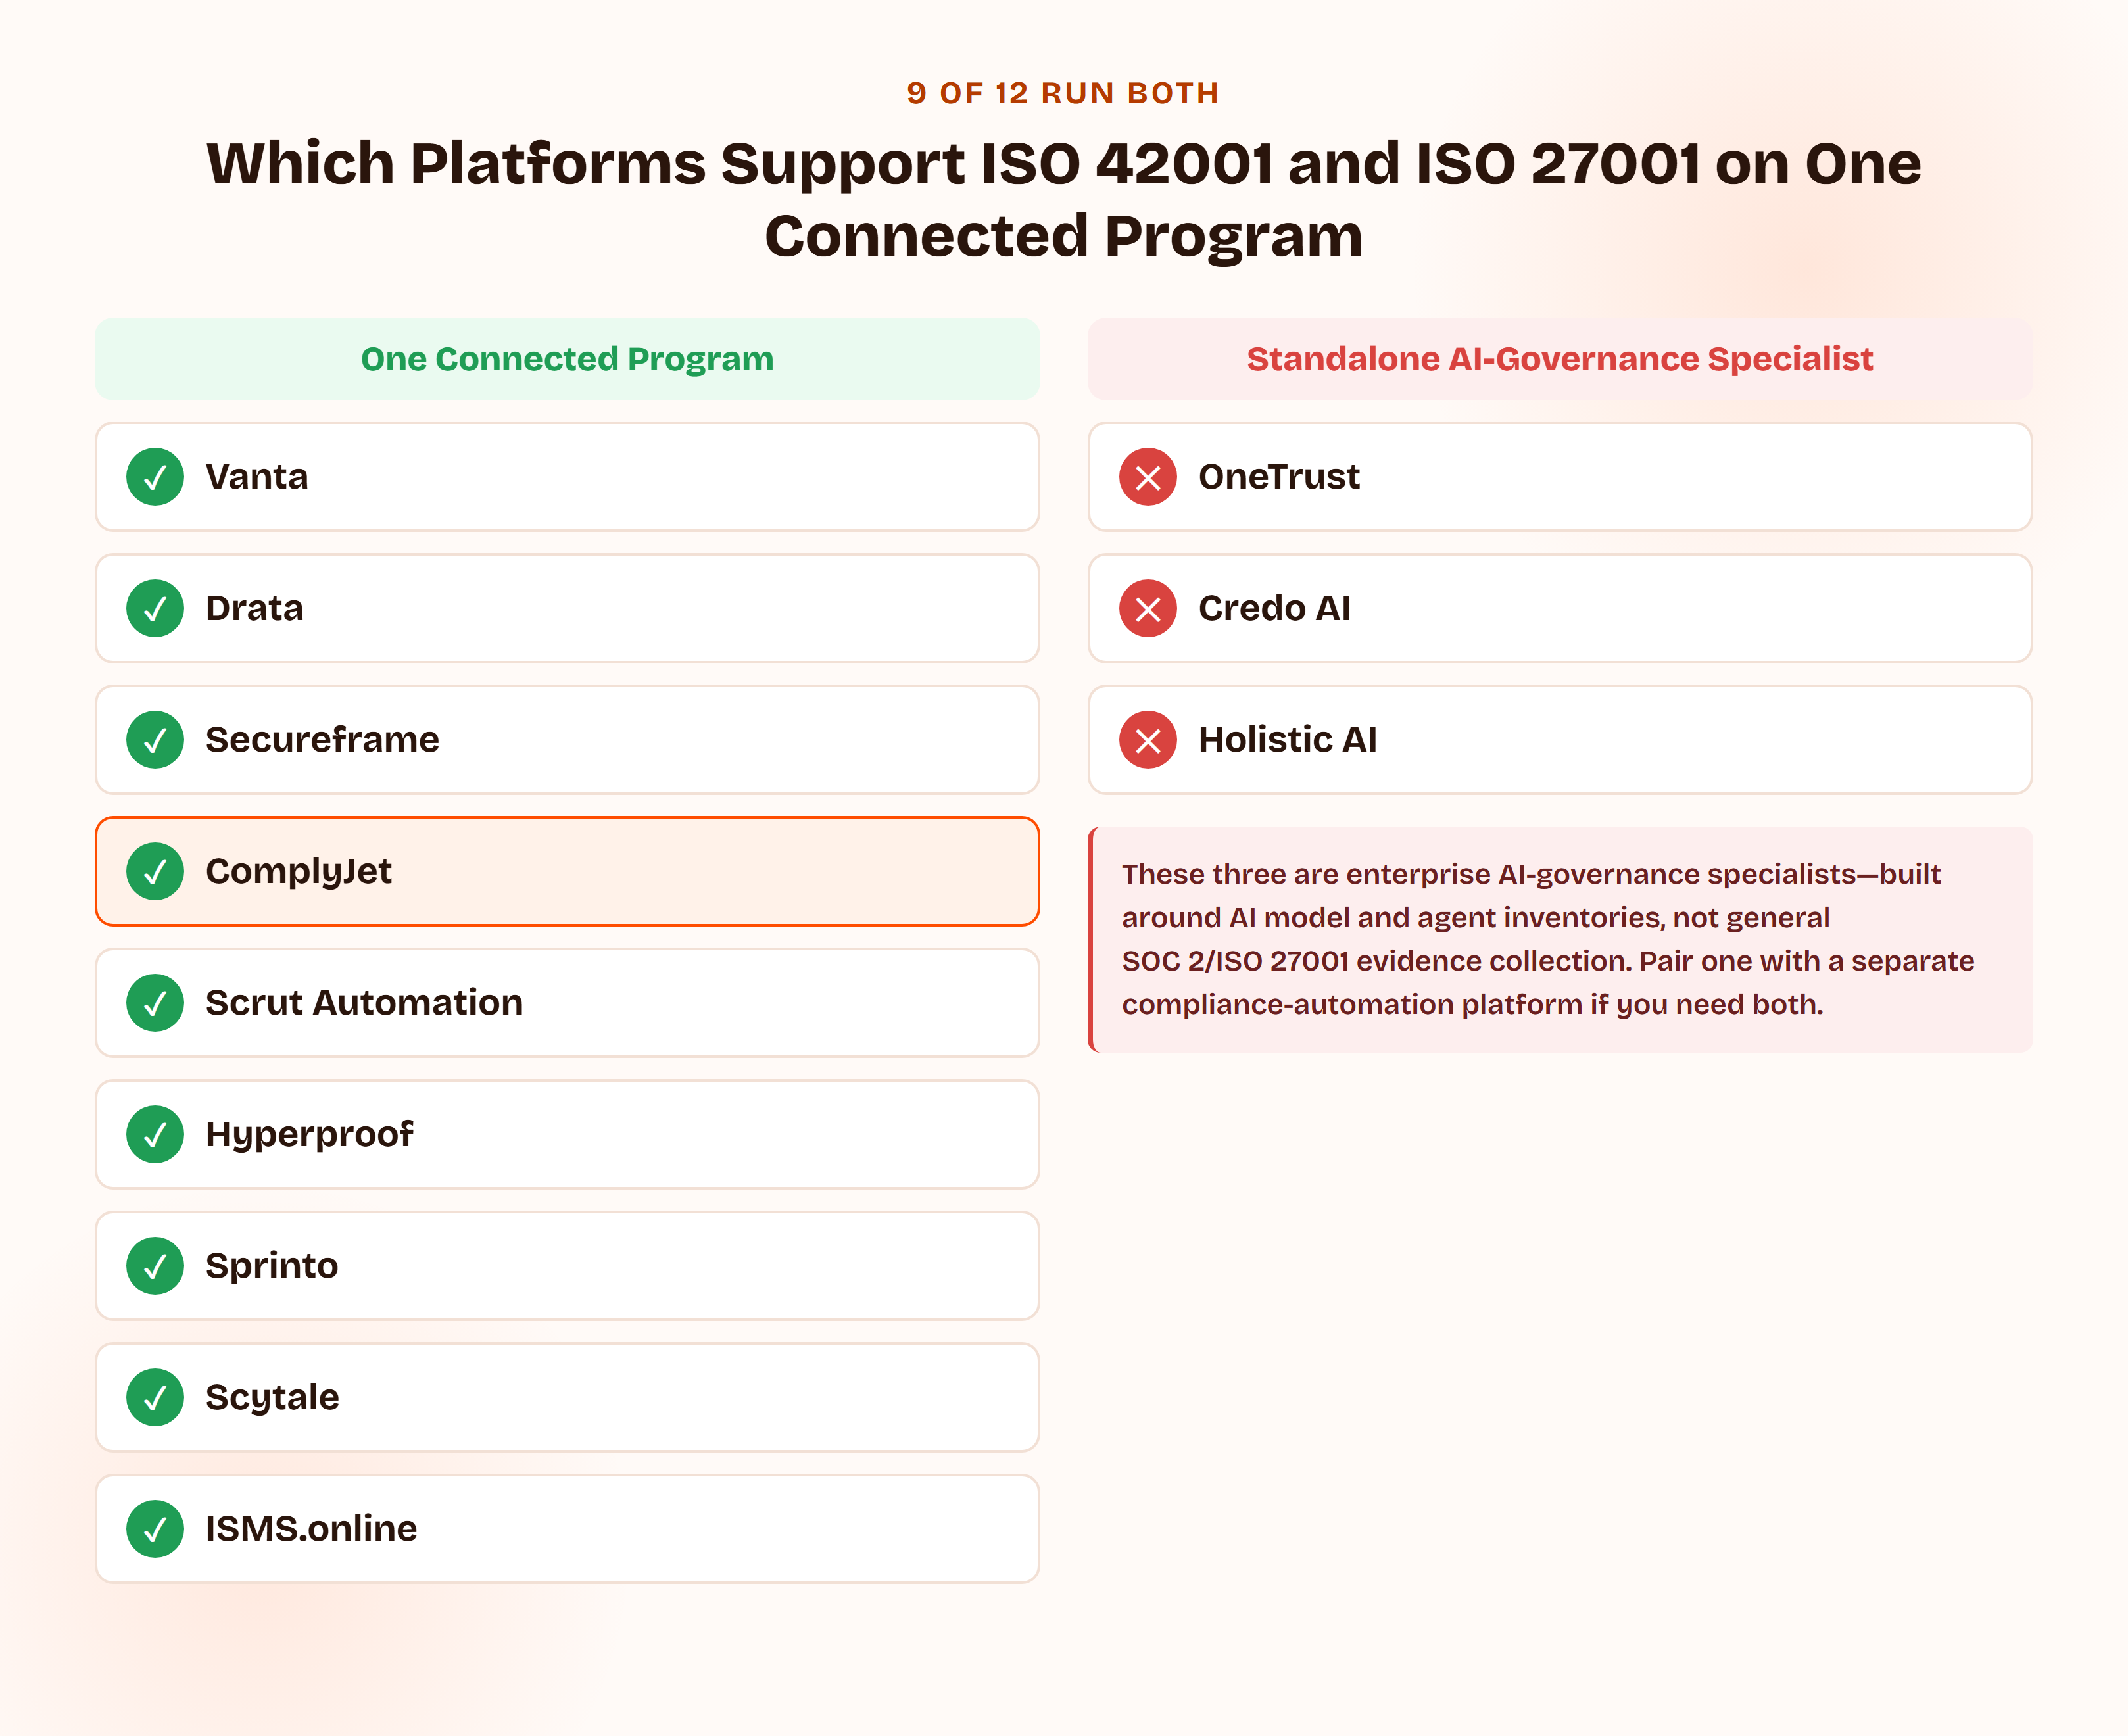
Of the twelve platforms compared here, nine run both on a genuinely connected compliance-automation program: Vanta, Drata, Secureframe, ComplyJet, Scrut Automation, Hyperproof, Sprinto, Scytale, and ISMS.online. OneTrust, Credo AI, and Holistic AI are standalone AI-governance specialist systems without a native SOC 2/ISO 27001 automation core — pairing one of them with a separate security-compliance platform is the realistic path if you need both and land in this group.
SOC 2 & ISO 27001
Already choosing a platform for SOC 2 or ISO 27001?
ComplyJet runs SOC 2, ISO 27001, and ISO 42001 on one connected, flat-priced program — shared evidence across all three instead of a separate purchase or a second vendor relationship.
FAQs
What Is ISO 42001 Compliance Software?
It's the platform layer that operationalizes an AI Management System — governance, risk-assessment, and lifecycle controls for how an organization designs, develops, deploys, and monitors AI systems, mapped to ISO/IEC 42001:2023's clauses and Annex A controls.
Some vendors market it as ai governance compliance software rather than a straight framework module, which is a useful signal of which of the two markets in this comparison they actually belong to: startup-familiar compliance-automation platforms that added it as one more framework, and enterprise-priced AI-governance specialists built around AI model and agent discovery.
Is AI Governance Software Different from ISO 42001 Software?
Not always, but sometimes. Most of the startup-compliance platforms on this list (Vanta, Drata, Secureframe, ComplyJet, Scrut, Hyperproof, Sprinto, Scytale, ISMS.online) sell ISO 42001 as a specific framework module inside a broader compliance-automation product. The three enterprise AI-governance specialists (OneTrust, Credo AI, Holistic AI) sell a broader "AI governance platform" that maps to ISO 42001 alongside the EU AI Act and NIST AI RMF, rather than treating any single framework as the whole product.
Do I Need ISO 27001 Before ISO 42001?
No. ISO 42001 is its own independent management-system standard, not an extension that requires ISO 27001 certification first. In practice, most SaaS companies pursuing ISO 42001 already have or are pursuing ISO 27001 or SOC 2 alongside it, since the standards share governance structure and a meaningful amount of evidence — but there's no formal prerequisite.
How Much Does ISO 42001 Certification Cost?
Certification cost varies by organization size, AI system scope, and whether a related management system (like ISO 27001) already exists. For the full cost discussion and what drives the range, see ComplyJet's ISO 42001 guide.
Does ISO 42001 Software Help with the EU AI Act?
Indirectly, yes, where the platform supports both. Vanta, OneTrust, Hyperproof, Credo AI, and Holistic AI all explicitly cross-map ISO 42001 controls to the EU AI Act's requirements in this comparison, reusing overlapping evidence rather than duplicating it. ISO 42001 certification is meaningful supporting evidence for an EU AI Act compliance program, but it doesn't replace the Act's own legal obligations, which sit outside what any ISO certification covers on its own.
Which Platforms Support Both ISO 42001 and ISO 27001?
Nine of the twelve platforms compared here run both on one connected compliance-automation program: Vanta, Drata, Secureframe, ComplyJet, Scrut Automation, Hyperproof, Sprinto, Scytale, and ISMS.online. See the "Platforms Supporting ISO 42001 and ISO 27001" section above for the full breakdown, including the three enterprise-specialist exceptions.
Is AI Governance Software Worth It for Startups?
If a customer, investor, or enterprise security review has made ISO 42001 or a documented AI governance program an explicit, contractual requirement, yes — the alternative is scrambling to build one manually once a deal is already stalled on it. If nobody's asked yet, it's reasonable to hold off on dedicated ISO 42001 software and address the underlying AI-governance question inside a SOC 2 or ISO 27001 program you're already running first.
What Does the Best ISO 42001 Software Include?
At minimum: confirmed, current ISO 42001 support stated directly on the vendor's own product page (not an inferred claim), evidence reuse with an existing SOC 2/ISO 27001 program if you have one, and pricing you can actually plan around before a sales call.
The deeper differentiator, if your organization has a real, sprawling AI estate, is genuine AI-specific tooling — model/agent inventory, bias and safety testing, AI-specific risk scenarios — which only a few platforms in this comparison, mostly the enterprise-tier specialists, genuinely have.
Final Thoughts on the Best ISO 42001 Software
There isn't one "ISO 42001 software" market to shop in — there are two, and confusing them wastes real time and, in the enterprise-specialist category's case, a very different budget. A set of startup-familiar compliance-automation platforms — Vanta, Drata, Secureframe, ComplyJet, Scrut Automation, Hyperproof, Sprinto, Scytale, and ISMS.online — added ISO 42001 as a framework module you can run alongside SOC 2 or ISO 27001.
Separately, a newer, enterprise-priced AI-governance specialist category — OneTrust, Credo AI, Holistic AI — exists for organizations with a real, sprawling AI estate and a dedicated AI/ML risk function to match.
Figure out honestly which market you're actually shopping in before you request a single demo. If what triggered this search was a SOC 2 or ISO 27001 questionnaire line asking about AI governance, not a hard ISO 42001 certification mandate, it's worth checking whether your existing compliance platform can answer that question before buying anything new at all.
Free Demo
Not sure if you need dedicated ISO 42001 software, or just a documented AI governance program?
Talk to ComplyJet either way — it runs ISO 42001 on the same connected program as SOC 2 and ISO 27001, with flat, per-company pricing and a team that guides you through it.
Related Reading on the Best ISO 42001 Software
- What Is ISO 42001? The Complete AI Management System Guide, for the framework explainer this comparison links out to throughout.
- AI Governance Policy, for building the program-level policy document this article's Mode A vendors help operationalize.
- Does SOC 2 Cover AI?, for readers whose real trigger is an AI question inside an existing SOC 2 review, not a hard ISO 42001 mandate.
- Top SOC 2 Compliance Platforms for AI Companies, the closely related comparison for AI companies weighing SOC 2 into the same platform decision.
- Best ISO 27001 Compliance Software, the parallel comparison for the ISMS standard ISO 42001 shares governance structure with.
- Best GRC Software, for readers evaluating a broader governance, risk, and compliance platform beyond any single framework.
Sources: Vendor ISO 42001 support verified directly against each platform's own site — Vanta's ISO 42001 compliance software page, Drata's frameworks page, Secureframe's frameworks page, OneTrust's AI Governance solution page, Hyperproof's supported frameworks page, Scytale's frameworks page, ISMS.online's ISO 42001 page, Sprinto's ISO 42001 pages, Credo AI, and Holistic AI.
Also verified: Scrut Automation's ISO 42001 certification announcement, Thoropass's frameworks page (checked directly, ISO 42001/AI-governance absent), and Oneleet's frameworks page (checked directly, ISO 42001 absent from its 8 named frameworks). Credo AI pricing estimate sourced to co-aims.com's Credo AI review, flagged in-text as a third-party estimate, not a vendor-published figure. ComplyJet's ISO 42001 support and pricing confirmed directly against complyjet.com/frameworks as of publish (checked 2026-09-28).