Related Articles
No items found.

A customer's security team sends back a vendor questionnaire, and one line asks whether you hold ISO 22301 or have a certified business continuity program. You've got SOC 2, maybe ISO 27001 too — that part's covered. But this is a different question, and it deserves a real answer, not a guess. So you search for the best ISO 22301 software, expecting the kind of startup-relevant comparison you'd find for SOC 2 or ISO 27001.
What you find instead is strange. Half the results are "best business continuity software" roundups full of names you've never heard of — Fusion, Riskonnect, Archer — quoting six-figure annual contracts aimed at Fortune 500 resilience teams. The other half barely mention ISO 22301 by name at all.
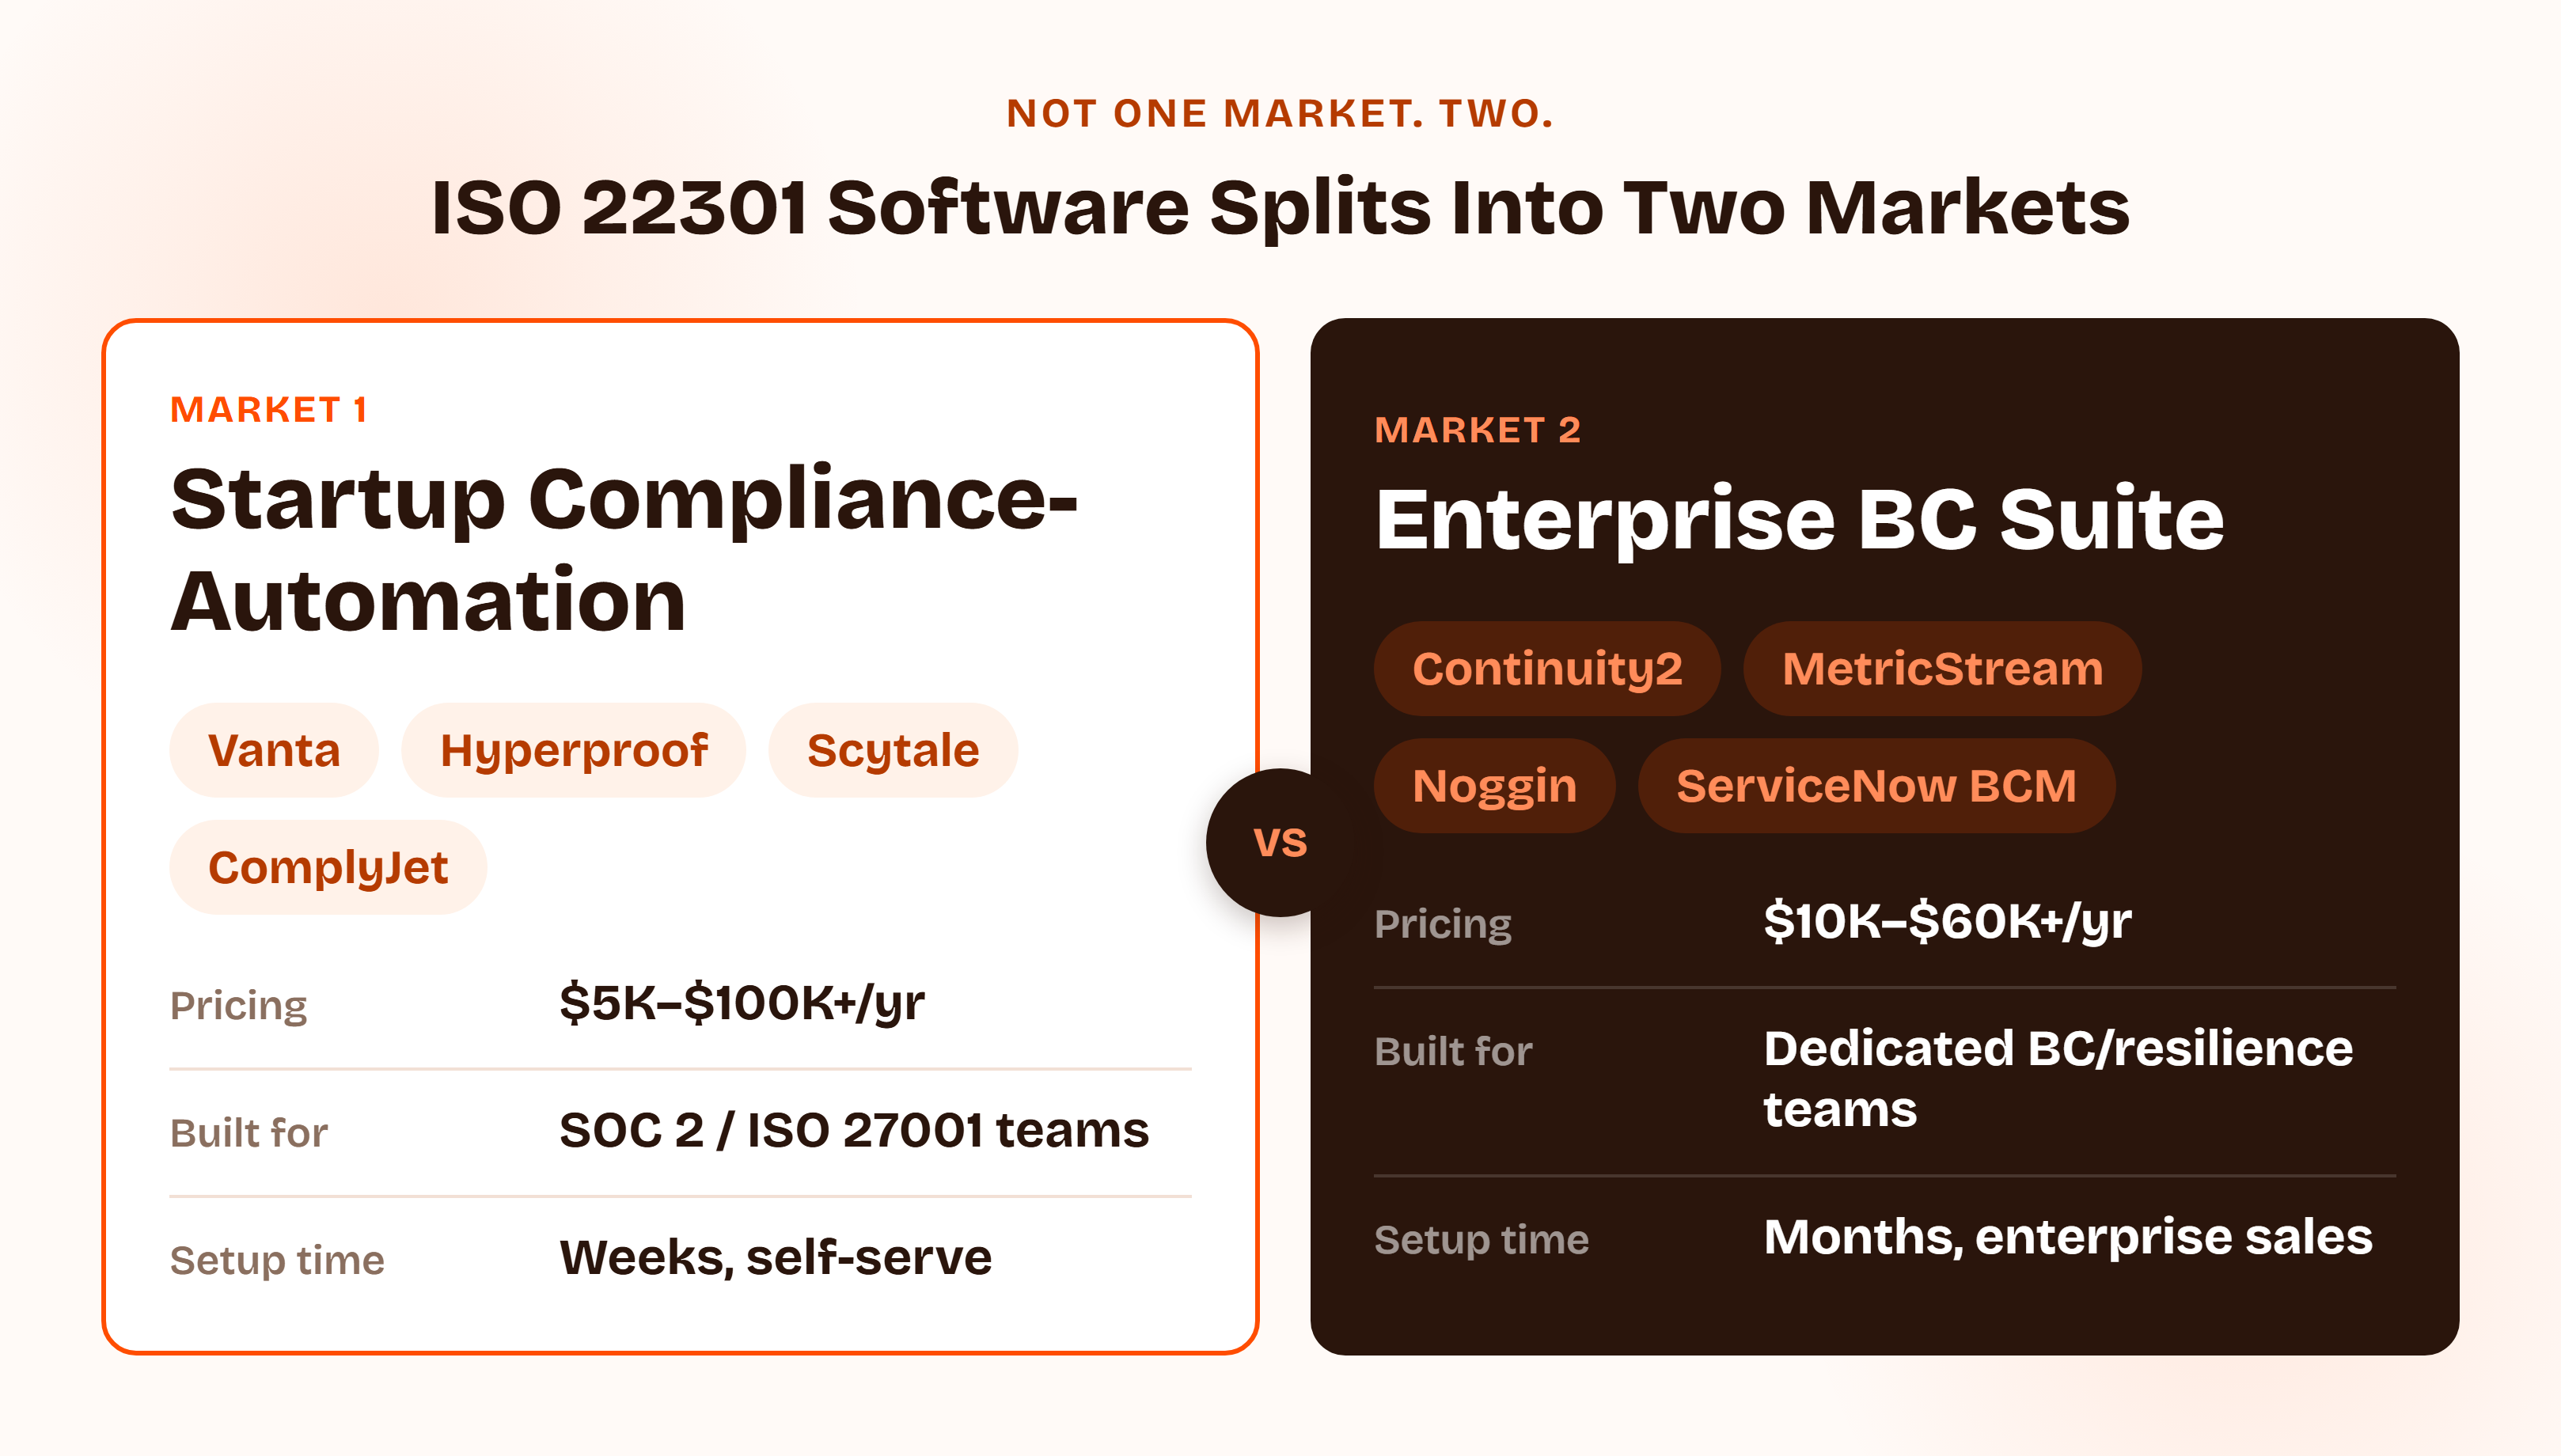
Here's the honest starting point, before any rankings: ISO 22301 software isn't one market. It's two, and they don't overlap much. A handful of the compliance-automation platforms startups already use for SOC 2 and ISO 27001 — Vanta, Hyperproof, Scytale — added ISO 22301 as one more framework module.
Separately, there's a much older, enterprise-priced business continuity suite category that most SaaS buyers researching "best iso 22301 software" have simply never encountered before. That split, not a single ranked list, is the frame this whole comparison runs on.
ISO 22301 compliance software — also searched as iso 22301 business continuity software — is the platform layer that operationalizes a Business Continuity Management System, or BCMS: business impact analysis, continuity and recovery plans, exercise and testing programs, and the audit-ready evidence a certification body actually checks, mapped to the standard's clauses.
That's the mechanics. The structural reality that matters more is this: business continuity management software, the broader category ISO 22301 tooling sits inside, has existed for over two decades as an enterprise discipline, built for organizations with a dedicated resilience or BC function. Vendors like Continuity2, MetricStream, and Noggin were built for that world — six-figure contracts, FTSE 100 and Fortune 500 customer bases, implementation timelines measured in months.
The compliance-automation platforms most SaaS startups already run — Vanta, Drata, Secureframe, Sprinto — came from a completely different direction: SOC 2 first, then ISO 27001, then a growing list of framework modules bolted onto the same evidence-collection engine. Only a few of them have actually added ISO 22301 to that list. Most haven't.
Most readers who land on "best iso 22301 software" coming from a SOC 2 or ISO 27001 background actually want the compliance-automation category — a platform that runs ISO 22301 alongside the frameworks they already have, not a dedicated resilience suite built for a company ten times their size. But most existing "best business continuity software" content only covers the enterprise suite category, because that's who's historically bought this software.
Knowing which market you're actually in before you start requesting demos saves real time. A five-figure annual compliance-automation add-on and a six-figure dedicated BC platform solve genuinely different problems, even though they both say "ISO 22301" on the page.
I didn't rank these off a blog mention or a features page skim. This ISO 22301 software comparison checked each platform's own current site directly for a real listing — a product page, a named framework in a live framework list, or a stated content library built around the standard — not an educational blog post that merely explains what ISO 22301 is.
I looked at which market each platform actually belongs to, since that's the distinction most existing content skips entirely: startup-familiar compliance-automation platform, or an older enterprise business-continuity suite. Where relevant, I checked whether ISO 22301 runs on the same connected program as an existing SOC 2 or ISO 27001 build. I checked pricing transparency, and I looked for real BIA/RTO/RPO-specific workflow rather than general GRC evidence collection with a privacy-style label slapped on it.
ComplyJet is included in this comparison on the same terms as every other vendor here — checked for real, current support, not a blog mention. ISO 22301 is a newer addition to its framework library, so it's disclosed as such rather than presented as a longstanding specialty the way Continuity2's is.
I also checked, and excluded, every other startup-compliance name that shows up in ComplyJet's own adjacent listicles. Drata, Secureframe, Scrut Automation, and Thoropass were all checked directly against their current frameworks or product pages — none show ISO 22301 support anywhere.
Sprinto's frameworks page returned an access error on my check and I found no product-page confirmation elsewhere, so it's excluded rather than guessed at. OneTrust is privacy-first with no business continuity product line. Oneleet's frameworks page names eight frameworks plus "10 more" and doesn't name ISO 22301 among them.
Two enterprise names deserve a specific note. Fusion Risk Management and Riskonnect both show up in general "best business continuity software" roundups, and both publish real educational content about ISO 22301. Neither one's own site states that its software supports or maps to the standard directly, the way Continuity2 or MetricStream do. I excluded both rather than inferring support that isn't stated plainly.
| Tool | Best for | Pricing | Standout feature |
|---|---|---|---|
| Vanta | Startups running ISO 22301 on the same platform as SOC 2/ISO 27001 | Not public (est. $14K–$100K+/yr) | Dedicated "Build and maintain your ISO 22301 BCMS" product page |
| ISMS.online | Teams wanting ISO 27001 + ISO 22301 certified together in one system | Not public, bespoke quote | Only vendor besides Vanta with a dedicated ISO 22301 product page |
| ComplyJet | Early-stage startups adding ISO 22301 to an existing SOC 2/ISO 27001 program | $5,000/yr (1 framework), $8,000/yr (2+) | Flat, publicly listed per-company pricing |
| Continuity2 | Larger organizations wanting a BC specialist that's itself ISO 22301 certified | Not public | 20+ years as a dedicated business-continuity software vendor |
| Hyperproof | Multi-framework GRC teams managing ISO 22301 alongside many other standards | Not public | 146–160+ frameworks with shared control mapping |
| Scytale | Existing Scytale customers wanting ISO 22301 on the same hands-on GRC relationship | Not public (tiered packages) | Confirmed live on Scytale's own frameworks page |
| MetricStream | Large enterprises with a dedicated GRC function needing a BCM module | Enterprise, 5-figures+/yr (no public figure) | BCM content library explicitly built on ISO 22301 standards |
| Noggin | Mid-market resilience teams wanting BC bundled with incident/crisis management | ~$10,000–$11,760/yr starting | Applies ISO 22301, 22313, and 22317 standards directly |
| ServiceNow BCM | Organizations where ServiceNow is already the platform of record | ~$60,000/yr starting | BIA/RTO/RPO workflow built on the ServiceNow AI Platform |
Vanta is the clearest fit on this list for a startup that already runs SOC 2 or ISO 27001 and needs ISO 22301 without adding a second vendor relationship. Its own product page — headlined "Build and maintain your ISO 22301 BCMS" — maps the standard's Clauses 4 through 10 directly, with templates for business impact analysis, continuity plans, exercises, and management reviews built in rather than left for you to construct from scratch.
Vanta pitches this explicitly around automation and AI-assisted evidence review: the platform flags missing approvals and incomplete sections automatically rather than leaving that check to a manual audit prep sprint. If you're already on Vanta for SOC 2 or ISO 27001, adding ISO 22301 reuses a meaningful amount of the same underlying evidence and workflow rather than starting a parallel program.
The tradeoff is the one every "best compliance software" list eventually lands on with Vanta: nothing here comes with a public number attached, and the gap between the quote you sign at and the one you renew at is a documented pattern across reviewers, not a rumor.
Key features:
Pricing: Not public. Contact sales for a quote; third-party estimates and AWS Marketplace list prices put real contracts in the $14,000–$100,000+/year range depending on frameworks and headcount.
Best for: SaaS teams that already run SOC 2 or ISO 27001 and want ISO 22301 added to the same connected program rather than a separate vendor relationship.
ISMS.online is the only other vendor on this list with a dedicated, named ISO 22301 product page, and it leads with the same overlap Vanta does: "easily combine ISO 27001 and ISO 22301... and obtain certification for both in our powerful all-in-one platform." Its page describes "a comprehensive and intuitive range of Business Continuity Management tools to help you plan for the unexpected, and then respond accordingly," with built-in policy and documentation templates it calls "Headstart content."
Where ISMS.online differs from Vanta is positioning: it's an ISO-management-system specialist first, not a broad multi-framework automation platform. That shows up in its review pattern — Capterra reviewers specifically credit it with making "the annual ISO 27001 audit much less painful," and the platform's overall Capterra rating sits at 4.5 from a small sample of 8 reviews.
The honest downside shows up in the same review set: at least one reviewer states the product costs $1,000+ a year more than Vanta while sitting behind it on sophistication and functionality — a real, specific criticism worth knowing before you assume "ISO specialist" automatically means "better fit."
Key features:
Pricing: Not public. Bespoke, pay-for-what-you-use model based on selected frameworks and modules; requires a quote form or demo.
Best for: Teams that want ISO 27001 and ISO 22301 certified together inside one ISO-specialist platform, and value documentation depth over broad multi-framework automation.
ComplyJet is the fit for an early-stage SaaS startup that already runs, or is about to run, SOC 2 or ISO 27001 and wants ISO 22301 added to that same connected program instead of opening a second vendor relationship just for business continuity. ISO 22301 is a newer addition to ComplyJet's framework library — the team confirmed it directly, and it joins the 25+ frameworks ComplyJet already supports, including SOC 1, SOC 2, ISO 27001, HIPAA, GDPR, and PCI DSS.
Where ComplyJet differs from Vanta and ISMS.online, the two other vendors here with the most direct ISO 22301 support, is pricing and process rather than framework-specific tooling depth. Pricing is flat and publicly listed — $5,000/year for one framework, $8,000/year for two or more, per company rather than per seat — so it doesn't creep up as headcount grows within the plan.
Every other vendor in this comparison requires a sales call before you see a number; ComplyJet is the one that doesn't.
The rest of the pitch is the same connected-program story that runs through the rest of this list. Evidence collected for an existing SOC 2 or ISO 27001 audit — access logs, vendor reviews, policy sign-offs — gets reused against ISO 22301's overlapping requirements instead of managed a second time in a separate system.
That's paired with AI-assisted drafting help for the business continuity and disaster recovery documentation itself, white-glove support through setup, and a Trust Center to share audit-ready evidence with the customer whose questionnaire likely triggered this search in the first place.
Key features:
Pricing: $5,000/year for one framework, $8,000/year for two or more, flat per company. Publicly listed, no sales call required for a base number.
Best for: Early-stage SaaS startups already running, or about to run, SOC 2 or ISO 27001 on ComplyJet that want ISO 22301 added to the same connected, flat-priced program.
Continuity2 is the genuine business-continuity specialist on this list, and it's worth understanding as a different category of vendor from everything else here. The company describes itself as "World Leading Business Continuity Software," built specifically to be "compliant with the ISO standards for Business Continuity" — and it's ISO 22301 certified itself, with over 20 years in the category. Its CEO is credited with helping standardize the discipline's predecessor standard, BS 25999, ahead of ISO 22301's own publication.
Its customer base tells you who this is really built for: Continuity2 states its "software's versatility enables us to work with the world's largest organisations," naming FTSE 100 and Fortune 500 customers, and it holds G-Cloud registration for UK government work. This is not a startup-first product, and it doesn't pretend to be.
What you get for that scale is real depth: business impact analysis, IT disaster recovery, scenario testing and exercise management, and an operational resilience platform built around dynamic templates rather than copy-paste document management. If your organization genuinely has a dedicated BC function and complex, multi-site continuity requirements, that depth is the point. If you're a 30-person SaaS startup, it almost certainly isn't what you need yet.
Key features:
Pricing: Not public. Enterprise sales process; no self-serve pricing tier found.
Best for: Larger organizations with a dedicated business-continuity function that need the deepest ISO 22301-specific tooling available, not startups buying their first BC program.
Hyperproof's framework library is one of the largest on this list — 146 to 160+ frameworks depending on the source checked — and ISO 22301 sits inside it, confirmed two ways: a live customer case study describing how OutSystems uses Hyperproof for compliance across multiple frameworks including ISO 22301, and a product update noting that DORA has been remapped with ISO 27001 and ISO 22301 controls and crosswalked to Hyperproof's mapping engine.
Its actual strength, consistent with how it shows up on ComplyJet's other listicles, is cross-framework control mapping rather than depth on any single standard: evidence collected for ISO 27001 gets reused against ISO 22301 and other overlapping frameworks automatically, which matters most to a compliance team already juggling several standards rather than a first-time ISO 22301 buyer.
That breadth-first design carries the same tradeoff here it does elsewhere: Hyperproof is consistently described by reviewers as less intuitive for first-time users, with a real setup learning curve, and I found no ISO 22301-specific product page or dedicated BC tooling beyond the general framework and control-mapping engine.
Key features:
Pricing: Not public. No tiers or figures shown; the pricing page routes to demo or proposal requests only.
Best for: Larger or multi-framework organizations that need ISO 22301 mapped against several other overlapping standards at once, not a first BC purchase.
Scytale confirms ISO 22301 directly on its live all-frameworks page, under a description built around the standard's actual purpose: "Focuses on business continuity, ensuring organizations can operate during disruptions." That's a real, current, in-product listing — the bar this comparison holds every vendor to — sitting alongside its broader 40+-framework automation catalog.
Scytale's identity is built around hands-on GRC-expert support layered on top of automation, and reviewers notice it enough to name specific staff members by name in reviews — not something people bother doing when support is merely adequate. Its G2 rating, 4.8 from 578 reviews, is the highest of any vendor on this list, though those reviews reflect Scytale's platform broadly, not ISO 22301 specifically.
What I couldn't find is anything ISO 22301-specific beyond that single frameworks-page listing — no dedicated product page, no case study naming it, no BC-specific feature description. That doesn't mean the support isn't real. It means the depth is currently unverified beyond the base listing, worth knowing before assuming it's as built out as SOC 2 or ISO 27001 are on the same platform.
Key features:
Pricing: Not public. Tiered packages (Build, Scale, Enterprise) with additional consulting add-ons; contact sales or request a demo for a quote.
Best for: Teams that already like Scytale's hands-on GRC-expert model for SOC 2 or ISO 27001 and want ISO 22301 added to that same relationship.
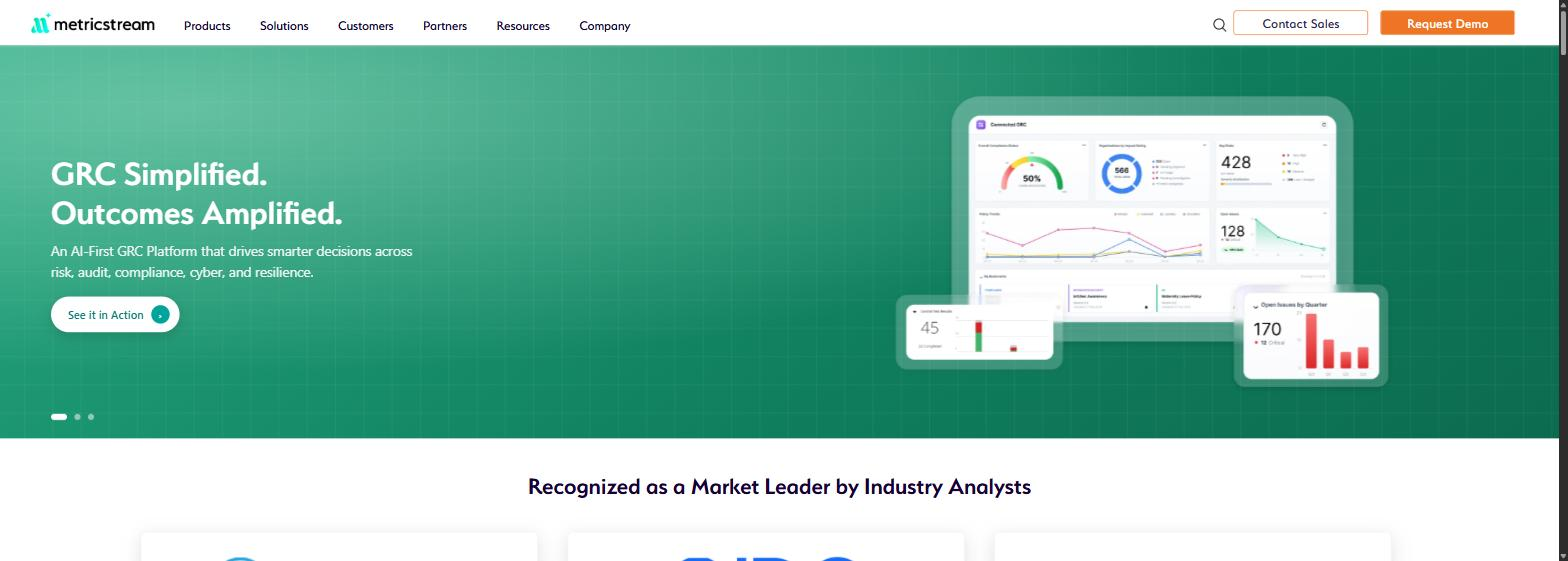
MetricStream is a genuine enterprise GRC platform, and its Business Continuity Management module is explicitly built around the standard: it ships with "a pre-built and configurable BCM content library based on ISO 22301 standards," designed to align BCM processes with ISO 22301 inside the broader M7 Integrated Risk Platform — business continuity planning, risk assessments, disaster tracking, and recovery action management in one system.
Reviewer sentiment is real but thin. G2 lists MetricStream's Business Continuity Management product specifically at 4.3 out of 5, drawn from only 4 reviews — a real number, but not one to over-index on given the sample size. Broader MetricStream GRC reviews describe a platform that's powerful but genuinely complex to configure and navigate, with training requirements heavier than most of the startup-familiar names on this list.
Pricing is the clearest enterprise signal here: one verified user review describes implementation costs running "upwards of 5 figures a year," with no public number published anywhere. This is a platform built and priced for an enterprise GRC function, not a first ISO 22301 purchase for a small team.
Key features:
Pricing: Not public. Enterprise quote required; one verified reviewer reports implementation costs "upwards of 5 figures a year."
Best for: Large enterprises with an existing GRC function that want business continuity management built on the same platform as broader enterprise risk management.
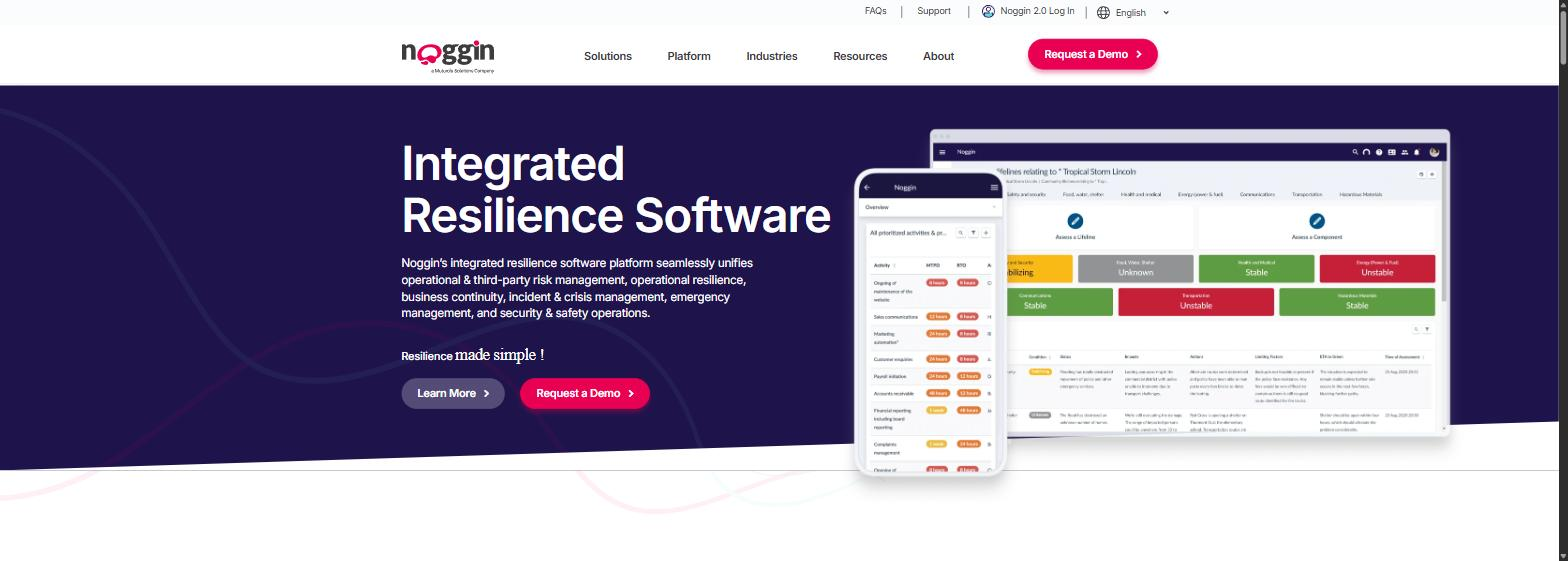
Noggin is worth including specifically because it's the most affordable of the true BC-specialist platforms on this list. It "applies industry standards drawn from the latest versions of ISO 22301, ISO 22313, ISO 22317" directly, per its own product content, combining business continuity with crisis, emergency, and work-safety management in a single all-hazards platform.
Pricing estimates put Noggin starting around $10,000 to $11,760 a year, with additional per-user or per-hour costs on top depending on license tier — meaningfully lower than Continuity2, MetricStream, or ServiceNow BCM, even if it's still a real step up from a compliance-automation add-on. Reviewers consistently praise its flexibility and ease of use, with users specifically noting they can build and test their own workflow changes before pushing them live.
The honest caveat, raised directly by reviewers: the distinction between "lite" and "full" user licenses creates real cost-planning friction, and it's worth getting a clear breakdown of who on your team needs which license type before you sign.
Key features:
Pricing: Estimated starting around $10,000–$11,760/year, plus additional per-user or per-hour costs depending on license tier; no fully public rate card found.
Best for: Mid-market teams that need a genuine, standards-built BC platform without Continuity2 or MetricStream's enterprise price tag.
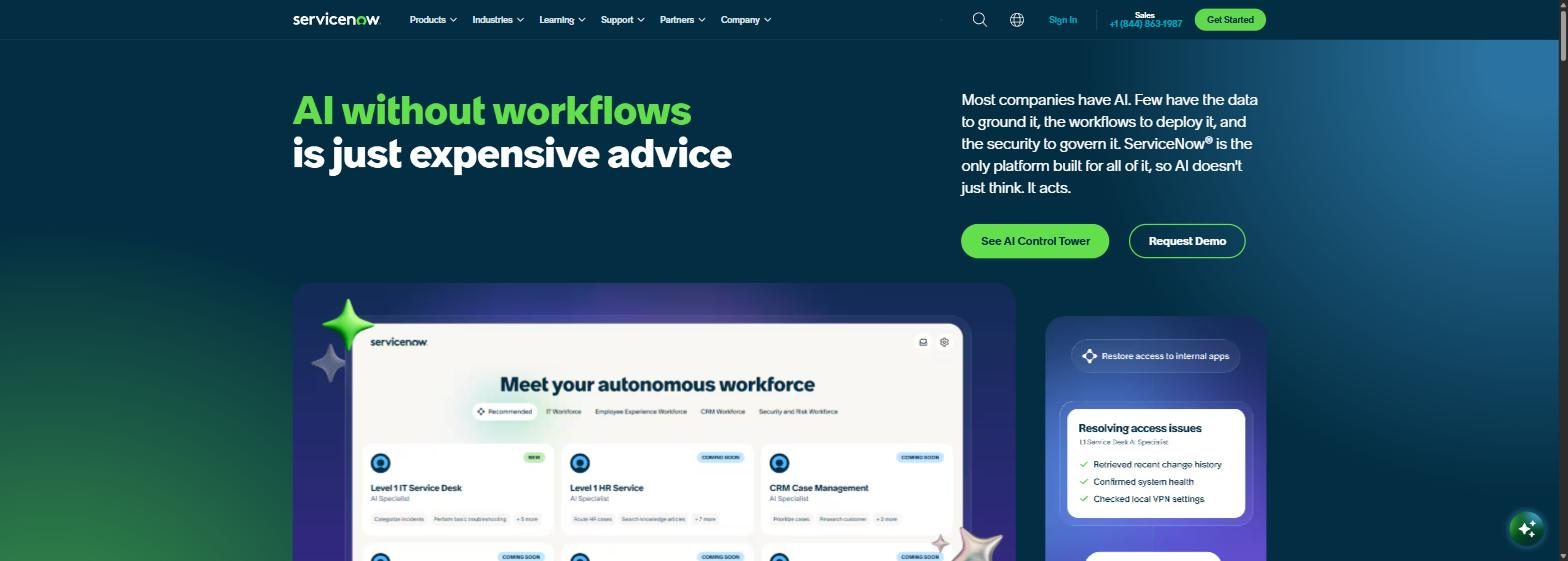
ServiceNow's Business Continuity Management module, built on the ServiceNow AI Platform, gives you business impact analysis and recovery time/recovery point objective (RTO/RPO) tracking — functionality that maps directly onto what an ISO 22301 auditor will actually want to see. It's worth being precise about what that means, though: ServiceNow's own site does not explicitly brand or certify this module as "ISO 22301 support." The functional overlap is real; the marketing claim isn't made.
Where ServiceNow BCM genuinely earns a place on this list is for organizations where ServiceNow is already the platform of record for IT and operations. Building business continuity workflows on top of a system your team already lives in avoids a second tool with its own login, its own data model, and its own integration project.
Pricing estimates put ServiceNow BCM starting around $60,000 a year — squarely enterprise territory, and not a reasonable first purchase for a team evaluating ISO 22301 for the first time without an existing, heavy ServiceNow footprint already justifying the cost.
Key features:
Pricing: Not public in detail; third-party estimates put it starting around $60,000/year. No free trial available.
Best for: Organizations that already run ServiceNow as their IT/ops platform of record and want business continuity workflows built on the same system.
This section covers how to choose ISO 22301 compliance software based on where you're actually starting from, not a generic checklist. If you take one thing from this guide to how to choose ISO 22301 compliance software, make it the market question below — it decides everything else.
Start here, honestly, before shopping. If the trigger was a single questionnaire line asking about business continuity as part of a broader SOC 2 or ISO 27001 review — not a customer or regulator specifically requiring ISO 22301 certification — you may not need dedicated BCMS software at all yet. A well-built business continuity and disaster recovery plan, evidenced inside the audit you're already running, often answers the question that actually got asked.
If ISO 22301 certification itself is the explicit requirement — a specific customer contract clause, a regulated-industry mandate, or a genuine strategic decision to certify — then you're in the market this article covers, and the rest of this section applies directly.
This is the single most important filter on this list. Vanta, Hyperproof, Scytale, and ComplyJet are built by and for the same startup-compliance buyer who's already evaluating SOC 2 and ISO 27001 platforms — reasonable pricing relative to company size, fast setup, self-serve or lightly-guided onboarding.
Continuity2, MetricStream, Noggin, and ServiceNow BCM are a different species of vendor. They're built for organizations with a dedicated business-continuity or resilience function, sized and priced accordingly — five to six figures a year, implementation measured in months, not weeks. None of that makes them worse software. It makes them the wrong shop for a 40-person SaaS company buying its first ISO 22301 program.
If you already run SOC 2 or ISO 27001 on a compliance-automation platform, check first whether that platform — or one of the four confirmed ISO 22301-capable ones here — can run ISO 22301 alongside it before evaluating a completely separate BC suite. Shared evidence and a single vendor relationship is usually the faster, cheaper path when it's available.
Of the nine platforms compared here, four run both on a genuinely connected compliance-automation program: Vanta, Hyperproof, Scytale, and ComplyJet. ISMS.online combines ISO 27001 and ISO 22301 certification support in one system, though it's positioned as an ISO-documentation specialist rather than the same kind of automated evidence-collection platform.
Continuity2, MetricStream, Noggin, and ServiceNow BCM are standalone business-continuity systems without a native SOC 2/ISO 27001 automation core — pairing one of them with a separate security-compliance platform is the realistic path if you need both and land in this group.
It's the platform layer that operationalizes a Business Continuity Management System — business impact analysis, continuity and recovery plans, exercise programs, and audit-ready evidence, mapped to ISO 22301's clauses.
Some vendors market it plainly as iso 22301 business continuity software rather than a compliance-suite module, which is a useful signal of which of the two markets in this comparison they actually belong to: startup-familiar compliance-automation platforms that added it as a framework module, and older, enterprise-priced dedicated business continuity management software built for a dedicated BC function.
Yes. A business continuity and disaster recovery (BCDR) plan is a document — what your team does when something breaks. ISO 22301 software supports the certifiable system behind that plan: how it's built, tested, evidenced, and kept current against an internationally recognized standard, not just the document itself.
Not necessarily right away. If a customer's security questionnaire is really asking about business continuity as part of a SOC 2 or ISO 27001 review, a solid BCDR plan evidenced inside that existing audit may answer the question. If ISO 22301 certification itself is the explicit requirement, yes — you'll need software built around the standard's clauses, evidence requirements, and exercise program, whether that's a compliance-automation platform's module or a dedicated BC suite.
Certification cost is genuinely undocumented across most sources and varies widely by organization size and scope. For the full cost discussion and what drives the range, see ComplyJet's ISO 22301 guide.
Indirectly, yes, where the platform supports all three. Vanta, Hyperproof, Scytale, and ComplyJet can run ISO 22301 on the same connected program as an existing SOC 2 or ISO 27001 build, reusing overlapping evidence rather than duplicating it. The dedicated BC suites on this list (Continuity2, MetricStream, Noggin, ServiceNow BCM) don't have a native SOC 2/ISO 27001 automation core, so they'd run alongside a separate security-compliance platform rather than replacing it.
Four of the nine platforms compared here run both on one connected compliance-automation program: Vanta, Hyperproof, Scytale, and ComplyJet. ISMS.online also supports certifying both, positioned as an ISO-documentation specialist rather than an automated evidence-collection platform. See the "Platforms Supporting ISO 22301 and ISO 27001" section above for the full breakdown.
If a customer or regulator has made ISO 22301 certification an explicit, contractual requirement, yes — the alternative is scrambling to build a BCMS manually once a deal is already stalled on it. If what actually got asked was a general business-continuity question inside a SOC 2 or ISO 27001 review, it's reasonable to hold off on dedicated ISO 22301 software and address it inside the audit you're already running first.
At minimum: confirmed, current ISO 22301 support stated directly on the vendor's own product page (not an inferred claim), evidence reuse with an existing SOC 2/ISO 27001 program if you have one, and pricing you can actually plan around before a sales call. The deeper differentiator, if your organization has a genuine dedicated BC function, is real BIA/RTO/RPO-specific workflow — which only a few platforms in this comparison, mostly the enterprise-tier ones, genuinely have.
There isn't one "ISO 22301 software" market to shop in — there are two, and confusing them wastes real time. A handful of startup-familiar compliance-automation platforms — Vanta, Hyperproof, Scytale, and ComplyJet — added ISO 22301 as a framework module you can run alongside SOC 2 or ISO 27001. Separately, an older, enterprise-priced business continuity suite category — Continuity2, MetricStream, Noggin, ServiceNow BCM — exists for organizations with a dedicated resilience function and a budget to match.
Figure out honestly which market you're actually shopping in before you request a single demo. If what triggered this search was a SOC 2 or ISO 27001 questionnaire line, not a hard ISO 22301 mandate, it's worth checking whether your existing compliance platform can answer that question before buying anything new at all.
Sources: Vendor ISO 22301 support verified directly against each platform's own site — Vanta's ISO 22301 compliance software page, Drata's frameworks page (checked directly, ISO 22301 not listed), Secureframe's frameworks page (checked directly, ISO 22301 not listed), Hyperproof's supported frameworks page, Scytale's frameworks page (lists ISO 22301 under business continuity), ISMS.online's ISO 22301 page, and Continuity2.
Also verified: Scrut Automation's ISO standards post (educational content only, ISO 22301 absent from its own supported-framework lists), Thoropass, OneTrust's products page (no BC product line), Oneleet's frameworks page, MetricStream's Business Continuity Management product, Noggin's business continuity solution page, and ServiceNow's Business Continuity Management page.
Pricing estimates for platforms without public pricing sourced to third-party listicle Fortiv's "10 Best Business Continuity Software Compared in 2026" where cited, plus AWS Marketplace listings and verified user reviews. Review sentiment and ratings sourced to G2 and Capterra listings for each respective vendor, checked directly rather than taken from a vendor's own review-quote selection. ComplyJet's ISO 22301 support and pricing confirmed directly by the ComplyJet team; reflected on complyjet.com/frameworks as of publish.


© 2026 ComplyJet. All rights reserved.

