A customer's security team sends back a vendor questionnaire, and one line asks whether you hold ISO 27701. You've got ISO 27001 — that part's done. But this is a different question, and you know it deserves a real answer, not a guess. So you do what anyone would do: you search for the best ISO 27701 software, expecting a ranked list the way you'd find one for SOC 2 or ISO 27001.
What you find instead is a lot of ISO 27001 listicles wearing an ISO 27701 label, and a couple of single-vendor pages that never name a competitor. Nobody has actually written the comparison you're looking for — which is a strange gap, given how often this question shows up in security reviews now.
Here's the honest starting point, before any rankings: ISO 27701 isn't sold as its own software category by any vendor I checked. It's a framework module inside the same multi-framework compliance platforms already competing on SOC 2 and ISO 27001 — Vanta, Drata, Secureframe, and the rest. That's not a caveat buried at the end of this piece. It's the frame the whole comparison runs on.
What Is ISO 27701 Compliance Software? The ISO 27701:2025 Compliance Software Change
ISO 27701 defines a Privacy Information Management System, or PIMS — the controller/processor-specific extension to an Information Security Management System (ISO 27001's ISMS). In practice, ISO 27701 compliance software is the platform layer that operationalizes a PIMS: evidence collection, control mapping, and — for the vendors that go deeper — DPIA and ROPA tracking specifically.
That's the mechanics. The framing that actually matters right now is the 2025 revision. ISO 27701:2025 compliance software now needs to support standalone certification — an organization no longer has to hold ISO 27001 first to pursue ISO 27701 on its own. For years the practical reality was the opposite: ISO 27001 certification was step zero. The 2025 update removed that gate.
Most readers here still fall into the other group, though: you already have ISO 27001, or you're mid-certification, and a customer or DPA review has started asking privacy-specific questions your ISO 27001 certificate doesn't fully answer. For that reader, the standalone-certification change matters less than one practical question: does the platform you're already running ISO 27001 on also cover ISO 27701, or are you about to manage two separate tools for two standards that share most of their evidence?
What the Best ISO 27701 Software Actually Automates (Privacy Information Management System Software)
Strip away the marketing language, and privacy information management system software does three things worth caring about: it maps ISO 27701's controls (many of which extend existing ISO 27001 controls rather than replacing them), it collects and stores privacy-specific evidence (data subject request handling, sub-processor tracking, retention schedules), and — for a smaller subset of vendors — it gives you dedicated tooling for DPIAs and a Record of Processing Activities.
Most of the platforms in this list do the first two well. Fewer do the third one deeply.
Not what this article is
This is a software comparison, not a framework explainer. For what ISO 27701 actually is, its clauses, the controller-vs-processor split, and full certification cost, read ComplyJet's ISO 27701 guide. This article picks up where that one leaves off: which platforms to actually buy.
Extend, Don't Duplicate
Already running ISO 27001 somewhere? Start there before buying new tooling
ComplyJet runs ISO 27701 on the same connected program as an existing ISO 27001 build, so the overlapping evidence gets collected once instead of managed in two separate places.
How I Evaluated These 11 Best ISO 27701 Software Platforms (ISO 27701 Software Comparison Method)
I didn't rank these off a blog mention or a features page skim. For each platform, I checked its own frameworks or help-center page directly for a real, current ISO 27701 listing — not a glossary entry, not an inferred claim. I looked at whether ISO 27001 and ISO 27701 run on one connected program or need separate setups, since that's the operational question that actually matters once you're past the sales call.
I checked 2025-edition and standalone-certification readiness, and looked for real pricing transparency versus a "contact sales" wall. I tried to find whether each platform does genuine privacy-specific evidence work — DPIA, ROPA, controller/processor mapping — or just general ISMS evidence with a privacy label on it. And I weighed support model: self-serve software access versus a guided process with a human on the other end.
Two vendors that show up in adjacent "best ISO 27001 software" lists didn't make this one, at least not at first. Scytale's ISO 27701 mention, when I first checked, looked like a glossary entry rather than a confirmed in-product framework. Oneleet had no ISO 27701 evidence at all.
I went back and re-verified both directly before finalizing this list. Scytale now has a real answer: its live frameworks page lists ISO 27701 under "Privacy Frameworks" with a direct product description, not just a content topic, so it's in the ranking below.
Oneleet's frameworks page still lists SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, CIS, NIST 800-171, and DORA, with an un-itemized "+10 more" bucket and no ISO 27701 named anywhere I could find — it stays out, with this note instead of a silent drop.
Quick Comparison: 11 Best ISO 27701 Software Platforms at a Glance
| Tool | Best for | Pricing | Standout feature |
|---|---|---|---|
| Vanta | Broadest automated multi-framework privacy + security stack | Not public (est. $14K–$100K+/yr) | Dedicated ISO 27701 product track with DSR/DPIA/DPA templates |
| Drata | Deepest integration library, strongest support reputation | Not public (est. $7.5K–$100K+/yr) | 300+ integrations, agentic AI for vendor risk |
| Secureframe | Startups adding ISO 27701 onto an existing SOC 2/ISO 27001 build | Not public (est. $7.5K–$70K+/yr) | Dedicated ISO 27701 page, 35+ frameworks in one platform |
| OneTrust | Larger teams needing enterprise-grade DPIA/ROPA tooling | Not public, module-metered | World's first ISO 27701 certification holder |
| ComplyJet | Early-stage startups pursuing ISO 27001 + ISO 27701 together for the first time | $5,000/yr (1 framework), $8,000/yr (2) | Flat, publicly listed per-company pricing |
| Sprinto | Startups wanting one platform across a large framework stable | Not public (est. $11.5K–$19.3K/yr) | 200+ frameworks with cross-framework evidence reuse |
| Scrut Automation | Multi-ISO-variant shops wanting flat-rate bundled pricing | ~$15,000/yr (AWS Marketplace, ≤20 employees) | 1,400+ pre-mapped ISO 27701 controls |
| Thoropass | Teams that want an in-house audit firm bundled with the software | Not public (custom quote) | ISO 27701 added in its May 2025 platform release |
| Scytale | Existing Scytale customers adding ISO 27701 to a SOC 2/ISO 27001 relationship | Not public (tiered packages) | Hands-on GRC-expert model, 40+ frameworks automated |
| Hyperproof | Larger orgs managing many overlapping frameworks at once | Not public (custom quote) | 160+ frameworks with shared control mapping |
| ISMS.online | Teams wanting deep ISO 27001/27701 documentation structure | Not public, bespoke quote | The only vendor with dedicated ISO 27701 product content |
The 11 Best ISO 27701 Software Platforms in 2026
1. Vanta
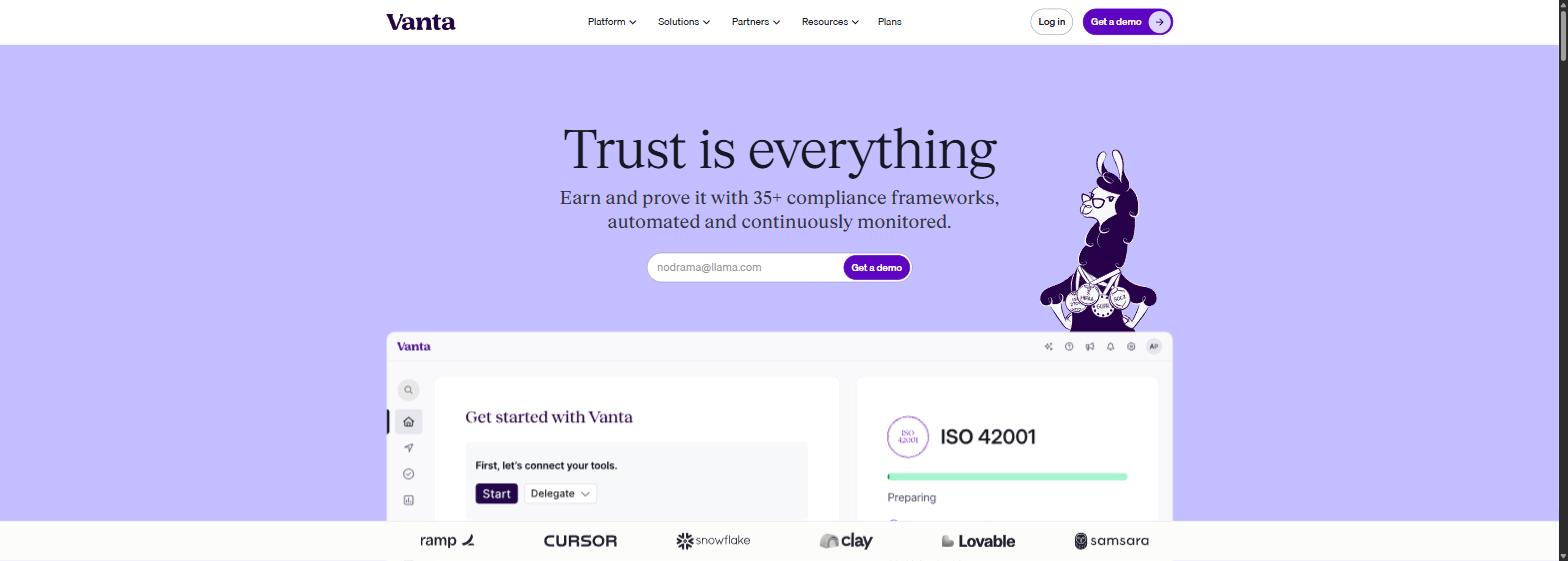
Vanta is the category default for a reason, and ISO 27701 is one of the few places it's actually built a dedicated product track instead of folding the framework into a general list. Its own product page — headlined "Certify your privacy program with ISO 27701" — maps the framework's clauses and its controller/processor/shared-role structure directly, with templates for data subject requests, DPIAs, and DPAs baked in rather than left for you to build from scratch.
If you're already running SOC 2 or ISO 27001 on Vanta, adding ISO 27701 is a genuinely light lift — the platform reuses evidence across the ISO 27017/27018/27701 extensions rather than treating each as a separate project. That overlap is real, and it's the same reason most of this list's top entries cluster around the platforms that already dominate SOC 2 and ISO 27001.
The tradeoff is the one every "best ISO software" list eventually lands on with Vanta: none of this comes with a public number attached, and the gap between what you're quoted at signature and what you're quoted at renewal is a documented pattern, not a rumor.
Vanta made it easier to implement privacy controls under ISO 27701 by centralizing privacy-related policies, controls, and evidence in a single platform, which reduced coordination overhead, improved traceability, and enabled more consistent enforcement of privacy practices across the organization. — Kevin Mercado, Chief of Staff, Sunthetics
Key features:
- Dedicated ISO 27701 product track with DSR, DPIA, and DPA templates
- Controller/processor/shared-role filtering built into the framework mapping
- Evidence reuse across ISO 27001, 27017, 27018, and 27701 extensions
- Hourly automated control testing across 400+ integrations
- Trust Center for sharing live security and privacy posture
Pros of Vanta
- Purpose-built ISO 27701 product page and controls, not a bolt-on framework listing
- Fastest setup for standard cloud stacks among the platforms in this list
- Genuinely ISO 27701-specific customer proof point, not a general testimonial stretched to fit
- Largest auditor ecosystem of any vendor here, which matters when scheduling Stage 1/2 audits
Cons of Vanta
- No public pricing anywhere; third-party deal data puts real contracts anywhere from roughly $14,000 to $100,000+ a year
- Documented pattern of steep year-two renewal increases
- Add-ons like Trust Center and vendor risk management are often needed on top of the base plan, adding real cost
- Requires a monitoring agent install some engineering teams push back on
Pricing: Not public. Contact sales for a quote; third-party estimates and AWS Marketplace list prices put real contracts in the $14,000–$100,000+/year range depending on frameworks and headcount.
Best for: SaaS teams that want the most automated, most privacy-specific ISO 27701 build available and are comfortable paying a premium for it.
2. Drata
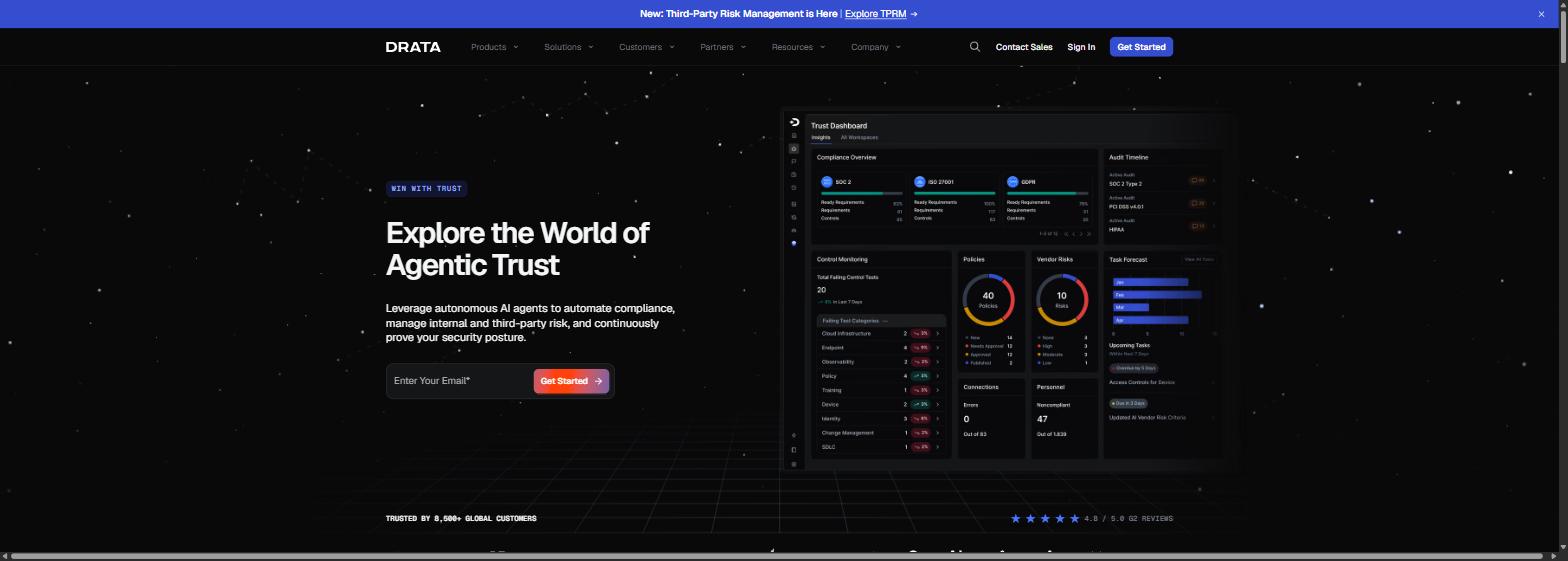
Drata shipped full ISO 27701:2019 framework support in mid-2024 — not a requirements-only checklist, but dedicated controls and mappings, and its current frameworks page still lists it plainly: "ISO 27701: Extend ISO 27001 with a privacy information management system."
Worth flagging directly: I found that description missing from one of Drata's own secondary marketing pages even though it's live on the primary frameworks page, which is a small but real signal that ISO 27701 isn't yet as consistently surfaced across Drata's own site as ISO 27001 or SOC 2 are.
Where Drata earns its ranking is everything around the framework, not the framework itself. It has the widest integration library on this list — 300+ connections — and a support reputation that shows up consistently across reviews as the thing customers mention unprompted. If your evaluation criteria weight "will someone answer me fast when something breaks" as heavily as framework depth, that's a real point in Drata's favor.
What it doesn't have, at least not that I could find, is an ISO 27701-specific customer story. Plenty of general compliance testimonials, nothing that names the privacy framework directly the way Vanta's does. That's a real gap worth knowing about going in, not a dealbreaker on its own.
Key features:
- Full ISO 27701:2019 framework support with dedicated controls and mappings
- 300+ integrations, one of the deepest libraries in this comparison
- Agentic AI for vendor risk management (added August 2025)
- Broadest named framework list of any vendor here (30+, including NIST AI RMF)
Pros of Drata
- Highest-volume, most consistently positive support reputation across reviewers
- Very wide integration coverage reduces manual evidence gaps
- Strong general framework breadth beyond just ISO 27701
Cons of Drata
- No ISO 27701-specific customer proof point found on its own marketing pages
- Pricing fully gated behind a sales call; documented renewal increases of 20–40% reported by customers
- Some reviewers describe support as inconsistent despite the strong average — "hit or miss" is the recurring phrase
- Initial setup and integration configuration take real time to work through
Pricing: Not public. Contact sales; third-party deal data (Vendr) shows observed contracts from roughly $9,600 to $60,000/year, median around $24,900.
Best for: Mid-market teams that want the deepest integration library and the strongest support reputation, and for whom ISO 27701 specifically isn't the primary reason they're buying.
3. Secureframe
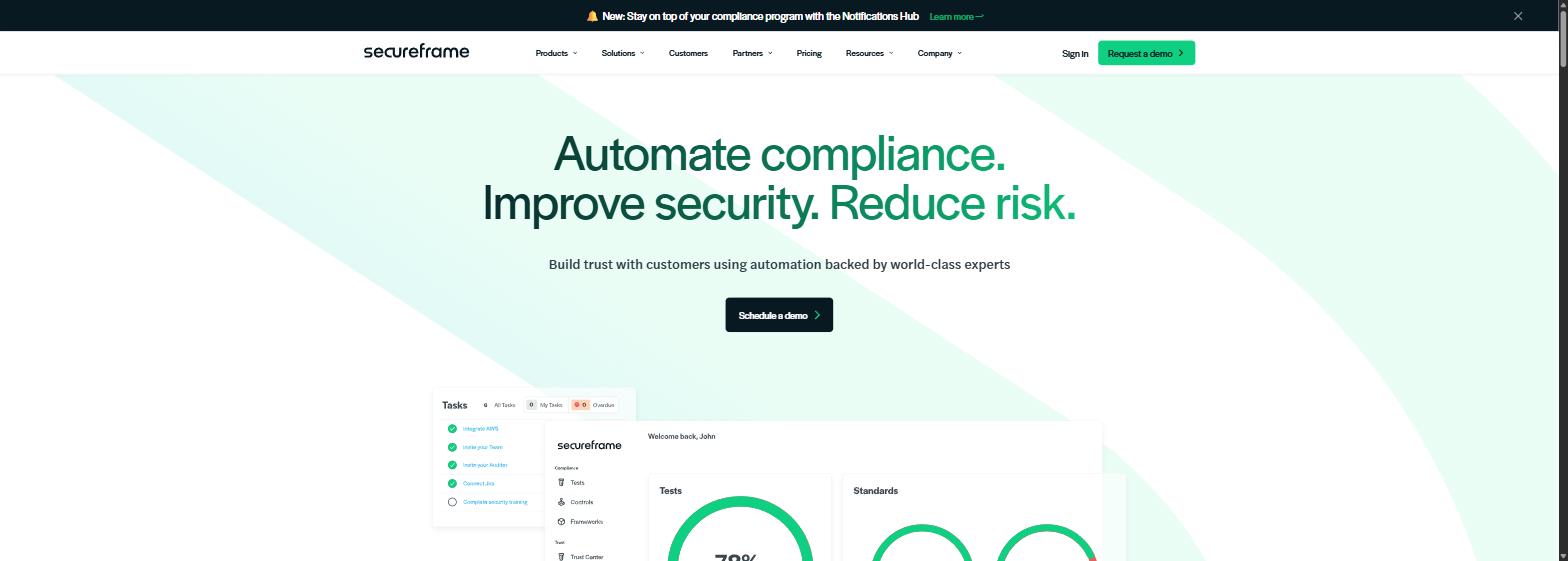
Secureframe treats ISO 27701 as exactly what it is structurally — a data privacy extension — and organizes it that way on its site, grouping it with GDPR, HIPAA, and CCPA under "Data privacy frameworks" rather than alongside SOC 2 and ISO 27001 in its "commercial security" bucket.
Its dedicated ISO 27701 page states plainly that the platform "enables companies to achieve and maintain ISO 27701 certification," and there's a real customer case backing it: Haystack pursued SOC 2, ISO 27001, and ISO 27701 together on Secureframe.
That categorization choice is honest, and it's also the clearest signal of what you're actually buying. ISO 27701 on Secureframe isn't a first-class category with its own dedicated tooling the way it is on Vanta or OneTrust — it's a well-supported add-on layer on top of a strong SOC 2/ISO 27001 core. For a startup that's already decided to run all three frameworks on one platform, that's a reasonable tradeoff, not a red flag.
We sell to enterprise clients that need security and privacy compliance; otherwise there is no sale. It's a requirement. — Yingsong Wang, Information System Security Engineer, Haystack (a customer that pursued SOC 2, ISO 27001, and ISO 27701 together via Secureframe)
Key features:
- Dedicated ISO 27701 framework page, categorized under data privacy alongside GDPR/HIPAA/CCPA
- 35+ supported frameworks total on one platform
- Dedicated compliance manager plus human auditor support included
- Automated evidence collection tied to the same controls that back SOC 2/ISO 27001
Pros of Secureframe
- Named, real customer example (Haystack) that pursued ISO 27701 specifically, not just a generic testimonial
- Human support from actual auditors, repeatedly cited as a strength in reviews
- Strong integration coverage across cloud and dev tooling
Cons of Secureframe
- ISO 27701 is positioned as a bolt-on privacy layer, not a first-class category with its own dedicated tooling
- Pricing entirely opaque; third-party estimates range from roughly $7,500/year for small startups to $35,000–$70,000+/year for larger, multi-framework teams
- Reviewers flag UX friction in document upload workflows and a questionnaire library limited to spreadsheet formats
Pricing: Not public. Three tiers (Fundamentals, Complete, Defense), contact sales for a quote; third-party estimates start around $7,500/year for a small single-framework build.
Best for: Startups already committed to SOC 2 and ISO 27001 who want ISO 27701 added as a privacy layer on the same platform, not teams shopping specifically for dedicated privacy-ops depth.
4. OneTrust
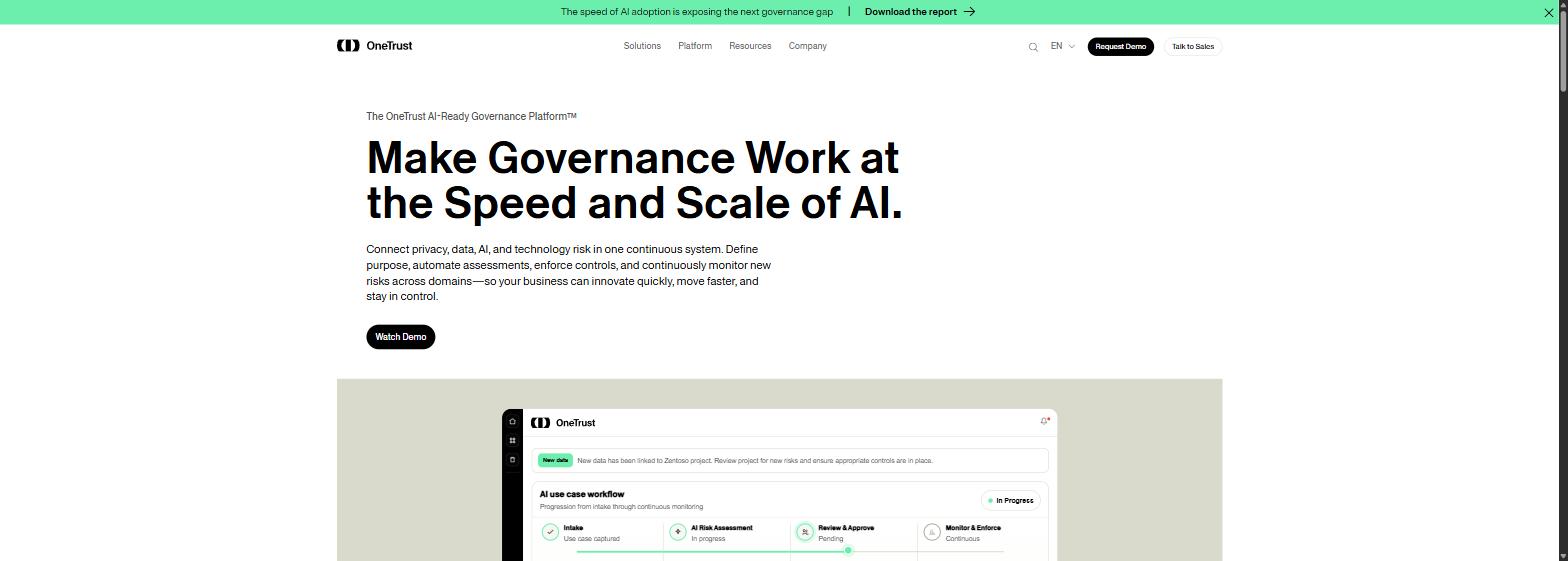
OneTrust is the privacy specialist of this list, and it's not a marketing claim — it holds the world's first ISO 27701 certification and has built out the deepest, most specific ISO 27701 content of any vendor here: a dedicated solution page and a standalone white paper, "ISO 27701: How OneTrust Helps."
Independent reviews back up the substance behind that positioning. Reviewers describe real DPIA and ROPA workflows, not just a feature list — one specifically calls out how "Privacy Assessments are easy to configure... Answers are collected and stored in the Data Mapping tool... for things like your RoPA."
That depth comes with real weight, though. This isn't a lightweight startup-first buy. Reviewers repeatedly describe it as overwhelming to implement, especially for smaller teams — a steep learning curve on top of a platform built around broader privacy-ops modules (consent management, vendor risk, data mapping) that most early-stage companies pursuing ISO 27701 for the first time don't need yet.
It also doesn't have a SOC 2/ISO 27001 automation core the way Vanta, Drata, or Secureframe do, so a startup would likely be pairing it with a separate security-compliance platform rather than running everything in one place.
Having software-based tools to help us streamline our privacy program is a crucial component of our ongoing GDPR readiness strategy. OneTrust technology will play an important role in helping us scale our privacy program across both customer and employee data. — Dr. Philipp Raether, Group Chief Privacy Officer, Allianz (a GDPR/privacy-program customer story — not ISO 27701-specific, the closest attributable quote found)
Key features:
- Dedicated ISO 27701 solution page and standalone white paper
- Genuine DPIA and ROPA tooling, independently confirmed by reviewers, not just vendor copy
- World's first holder of ISO 27701 certification
- Broader privacy stack (consent, DSAR, vendor risk, data mapping) under one roof
Pros of OneTrust
- Deepest confirmed DPIA/ROPA-specific tooling of any vendor in this comparison
- Genuinely unique credibility marker (first-ever ISO 27701 certification holder)
- Most purpose-built ISO 27701 content of any vendor here, including a startup wouldn't need to piece the story together from a generic frameworks page
Cons of OneTrust
- Reviewers describe it as overwhelming for new users or smaller teams, with a real learning curve
- No SOC 2/ISO 27001 automation core; a startup pursuing all three would likely need to run two platforms, not one
- Pricing is module-metered and opaque, adding real quoting complexity on top of the sales-gate every vendor here shares
- Sized and priced for a dedicated privacy function, which most early-stage startups don't have yet
Pricing: Not public. Module-based, metered pricing (admin users and inventory size for risk/compliance products; data volume for consent and privacy automation). Contact sales for a quote.
Best for: Larger or scaling companies with a dedicated privacy function that need enterprise-grade DPIA/ROPA/data-mapping tooling — not the lean, single-platform pick for a startup's first ISO 27701 push.
5. ComplyJet
I'm ranked here, so take the framing with that in mind — but the facts underneath it are checkable, and I'd rather you check them than take my word for it.
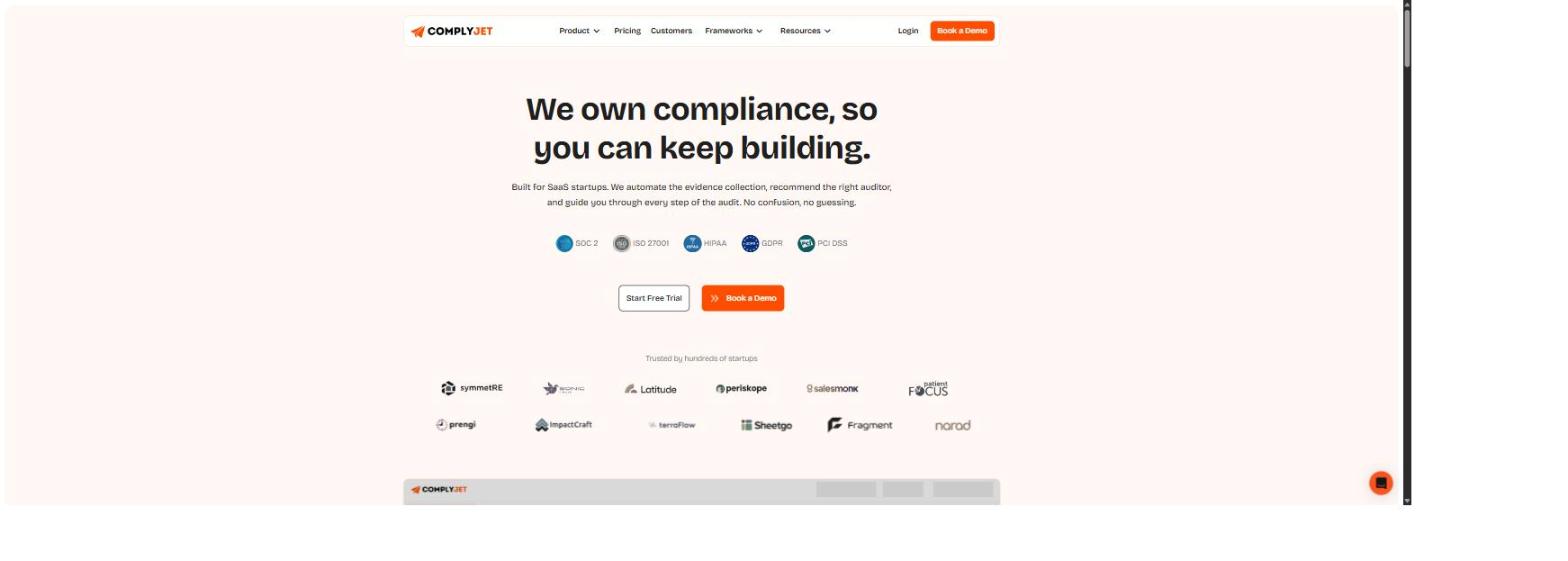
ComplyJet's frameworks page lists ISO 27701 directly: "Privacy extension to ISO 27001 for personal data processing." That's real support, confirmed on the live site. What ComplyJet doesn't have yet is what OneTrust and ISMS.online have built — a dedicated ISO 27701 landing page, a standalone white paper, or ISO 27701-specific marketing depth. If you're the kind of buyer who wants to read pages of framework-specific content before a demo call, that gap is worth knowing about upfront.
Where ComplyJet differs from nearly everyone else on this list is pricing and process, not framework-specific tooling. Pricing is flat and publicly listed — $5,000/year for one framework, $8,000/year for two, per company rather than per seat, so it doesn't creep up as your headcount grows within the plan's cap. Every other vendor in this comparison except ComplyJet requires a sales call before you see a number.
And the process is guided rather than self-serve: a team walks you through setup rather than handing you software and a login.
One honest caveat worth flagging directly, since it's easy to miss: the publicly listed Core and Plus plan pricing is explicitly scoped to a choice of "SOC 2, ISO 27001, HIPAA, or GDPR" — ISO 27701 isn't one of the four frameworks named on the pricing page itself, even though the frameworks page confirms it's supported.
If ISO 27701 specifically is the framework you're buying for, confirm at the demo whether it runs on the flat-rate Core/Plus pricing or requires the Custom tier, rather than assuming the advertised number applies automatically.
ComplyJet made SOC 2 and ISO 27001 readiness manageable with automated workflows, evidence collection, and expert support. The team was hands-on and flexible. — David Orr, COO, Romina Day (about SOC 2 and ISO 27001 readiness specifically — not an ISO 27701 case study, the closest real customer quote available)
Key features:
- ISO 27701 confirmed as a supported framework module on complyjet.com/frameworks
- Runs on the same connected program as an existing ISO 27001 build, so overlapping evidence isn't duplicated
- 350+ integrations included on every tier
- Team-guided process with 1:1 Slack support, not just software access
- Publicly listed, flat per-company pricing
Pros of ComplyJet
- Only vendor in this comparison with publicly listed pricing — every other platform requires a sales call to see a number
- Flat per-company pricing that doesn't scale with headcount inside the plan's employee cap
- ISO 27701 shares one connected program with an existing ISO 27001 build, not a separate tool or spreadsheet
- Guided, team-supported process rather than self-serve dashboard access
Cons of ComplyJet
- No dedicated ISO 27701 landing page or the standalone marketing depth OneTrust and ISMS.online have built for this specific framework
- Smaller company than Vanta or Drata, with a shorter track record in the category
- No independently verifiable G2 rating found during this research — I couldn't confirm one either way, so treat review-volume comparisons to Vanta or Drata's thousands of reviews accordingly
- Publicly listed flat pricing is explicitly scoped to SOC 2, ISO 27001, HIPAA, or GDPR on the Core/Plus tiers; confirm directly whether ISO 27701 runs on that pricing or requires a Custom quote
Pricing: $5,000/year for one framework, $8,000/year for two frameworks, flat per company (not per seat), for teams up to 50 employees. Larger teams or additional frameworks require a custom quote. Confirm ISO 27701's placement on this pricing directly, per the caveat above.
Best for: Early-stage startups pursuing ISO 27001 and ISO 27701 together for the first time, who want transparent pricing and a guided process over self-serve software access.
ISO 27001 & ISO 27701
Already building ISO 27001 on ComplyJet? ISO 27701 runs on the same program
No separate tool, no separate spreadsheet — ask us directly on a call whether your specific plan covers ISO 27701 before you commit.
6. Sprinto
Sprinto lists ISO 27701 among the 200+ frameworks on its public frameworks page, and its evidence-reuse story is genuinely strong across the board — privacy-relevant evidence gets automatically mapped and reused across GDPR, SOC 2, and ISO 27701 rather than collected three separate times. That's a real time saver for a team running multiple overlapping frameworks at once.
One thing worth flagging honestly, because Sprinto says it about itself: the platform distinguishes between roughly 25 frameworks it automates "out of the box" and 200+ it has "digitized." I couldn't confirm which bucket ISO 27701 falls into.
That distinction matters more than it sounds like it should — a digitized framework and a deeply automated one aren't the same level of product investment, and it's worth asking directly on a demo call rather than assuming ISO 27701 gets the full automation treatment.
Key features:
- ISO 27701 listed among 200+ supported frameworks
- Automated evidence collection across AWS, Okta, Google Workspace, and similar cloud tooling
- Cross-framework evidence reuse across GDPR, SOC 2, and ISO 27701
- High reviewer-reported ease of use
Pros of Sprinto
- Very high satisfaction scores across G2 and Capterra
- Broad framework library with real evidence-reuse mechanics, not just a shared dashboard
- Responsive customer support, frequently named directly in reviews
Cons of Sprinto
- Unclear whether ISO 27701 sits among the ~25 deeply automated frameworks or the broader 200+ digitized library — worth confirming directly before buying
- Pricing fully gated behind a sales call; some reviewers specifically cite cost as steep for smaller companies
- No confirmed dedicated DPIA/ROPA-specific tooling beyond general framework automation
- No EU data residency confirmed during this research
Pricing: Not public. Contact sales; third-party deal data (Vendr) shows a median around $15,000/year, with a broader estimated range of roughly $6,000–$25,000/year depending on tier.
Best for: Startups wanting one platform to manage a large stable of frameworks with heavy automation, comfortable with custom, sales-gated pricing.
7. Scrut Automation
Scrut's own published content on ISO 27701 is specific rather than generic: "1,400+ pre-mapped controls, 100+ integrations for automated evidence collection, and 75+ expert-vetted policy templates," aimed squarely at automating what it calls "a complex and time-consuming process" to implement manually. One of its named customers, e6data, is pursuing ISO 27001, 27017, 27018, 27701, SOC 2, and GDPR together through the platform — a genuine multi-framework case, even without a quoted testimonial attached to name.
Scrut's pricing model is also one of the more concretely sourced on this list, if not the friendliest: AWS Marketplace lists its Compliance Automation module at a flat $15,000 for 12 months, for organizations up to 20 employees, bundling 60+ frameworks rather than charging per framework. That's a real number from a real source, which is more than most of this list offers, even if it's not cheap for a small team.
Key features:
- 1,400+ pre-mapped controls specifically for ISO 27701
- 60+ frameworks bundled under one flat-rate structure
- 100+ integrations for automated evidence collection
- Real multi-ISO-variant customer example (e6data) pursuing 27701 alongside 27001/27017/27018
Pros of Scrut Automation
- Very high review scores across G2 and Capterra
- Flat-rate pricing bundling many frameworks, rather than charging per framework added
- Specific, sourced control count for ISO 27701 rather than a vague "we support it" claim
- Customers report measurable audit-timeline reductions
Cons of Scrut Automation
- No public pricing on Scrut's own site; the AWS Marketplace figure ($15,000/12 months, ≤20 employees) is the only directly sourced number, plus a separate onboarding fee
- No confirmed dedicated DPIA/ROPA-specific tooling beyond general control and evidence automation
- Reviewers cite a learning curve on advanced configuration and slower policy-update cycles
Pricing: Not public on Scrut's own site. AWS Marketplace lists its Compliance Automation module at $15,000 per 12 months for organizations up to 20 employees, plus a separate onboarding fee reported between $1,000–$5,000.
Best for: Multi-framework shops already juggling three or more ISO variants alongside SOC 2 and GDPR, wanting flat-rate bundled pricing over per-framework costs.
8. Thoropass
Thoropass added ISO/IEC 27701 in its May 2025 platform release, alongside NIS 2, ISO 9001, CMMC Level 2, and CIS Controls v8 — a real, sourced addition, stated plainly in its own product-update notes.
Worth being direct about what that means in practice: when I checked Thoropass's general frameworks page, ISO 27701 wasn't yet showing up in the visible framework grid, only ISO 27001 under "ISO Certifications." The support is real and current; it just isn't fully surfaced across the site's top-level marketing yet, which tracks with it being a genuinely newer addition rather than a long-established part of the platform.
Thoropass's real differentiator has never been framework count anyway — it's the bundled audit firm. You're not just buying software; Thoropass pairs the platform with its own in-house auditors, which is a meaningfully different buying decision than every platform-only vendor on this list.
Key features:
- ISO/IEC 27701 added in the platform's May 2025 release
- In-house audit firm bundled with the software, not sourced separately
- 30+ supported frameworks including SOC 2, ISO 27001, ISO 42001, HIPAA, HITRUST, GDPR, and CMMC
- Responsive, collaborative support repeatedly cited across reviews
Pros of Thoropass
- Audit and software bundled under one relationship, removing a separate auditor-sourcing step
- Broad, recently-expanding framework list added quickly (five frameworks in one release)
- Consistently praised support across review platforms
Cons of Thoropass
- ISO 27701 is a newly-added framework (May 2025) and, as of this research, less prominent on Thoropass's own top-level frameworks page than ISO 27001 is
- No ISO 27701-specific or privacy-specific customer quote found
- Pricing entirely opaque; no third-party estimate range could be independently confirmed beyond "tailored quote"
Pricing: Not public. Thoropass states pricing "varies based on factors such as the frameworks pursued, audit scope, company size, and required services," with a tailored quote for each organization.
Best for: Companies that want compliance software bundled with an in-house audit firm, adding ISO 27701 onto an existing ISO 27001 or SOC 2 program.
9. Scytale
Scytale is the one addition to this ranking I didn't expect going in. My first pass found only a glossary entry for ISO 27701 — educational content, not a product claim, which is exactly the kind of soft mention that shouldn't count toward a real "supports this framework" claim.
Going back and checking Scytale's live frameworks page directly changed that: ISO 27701 is listed under "Privacy Frameworks" with its own descriptor — "Extends ISO 27001 to include privacy management, helping organizations manage personal data and meet privacy regulations" — sitting alongside ISO 27018, GDPR, and CCPA. That's a real, current, in-product listing, which is the bar this comparison holds every vendor to.
Scytale's broader identity is a SOC 2 and ISO 27001 specialist built around hands-on GRC-expert support rather than pure self-serve software — reviewers notice this enough that they frequently name specific support staff by name, which isn't something people bother doing when support is merely adequate.
What I couldn't find is anything ISO 27701-specific beyond that one frameworks-page listing: no dedicated product page, no case study naming it, no privacy-specific customer story. That doesn't mean the support isn't real. It means the depth is currently unverified beyond the base framework listing, which is worth knowing before you assume it's as built-out as ISO 27001 is on the same platform.
Key features:
- ISO 27701 listed directly under "Privacy Frameworks" on Scytale's live frameworks page
- 40+ frameworks automated, including SOC 2, ISO 27001, ISO 42001, PCI DSS, and GDPR
- AI GRC Agent for automated evidence collection
- Hands-on GRC-expert model layered on top of automation
Pros of Scytale
- Genuine, current, direct product confirmation of ISO 27701 support, not a glossary-only mention
- Strong, consistently positive support reputation — reviewers naming specific staff members is a real trust signal
- Broad framework automation (40+) beyond just this one privacy standard
Cons of Scytale
- No dedicated ISO 27701 product page or case study found; privacy-specific depth beyond the base framework listing is unverified
- Pricing is entirely opaque even by this list's standard — three unpriced package tiers (Build, Scale, Enterprise) plus separate paid consulting add-ons
- Primarily known and marketed as a SOC 2/ISO 27001 specialist, so ISO 27701 reads as a recent addition rather than a core strength
Pricing: Not public. Tiered packages (Build, Scale, Enterprise) with additional consulting add-ons (LaunchReady, StayReady); contact sales or request a demo for a quote.
Best for: Teams that already like Scytale's hands-on GRC-expert model for SOC 2 or ISO 27001 and want to add ISO 27701 to that same relationship, rather than buyers shopping specifically for privacy-tooling depth.
10. Hyperproof
Hyperproof's framework library is one of the largest on this list — 160+ frameworks — and its own content confirms ISO 27701 by name alongside SOC 2, ISO 27001, NIST, HIPAA, and GDPR, with a dedicated explainer resource on the standard itself.
Its actual strength, though, is what it does across frameworks rather than within any single one: shared control mapping means evidence collected for ISO 27001 gets reused against ISO 27701 and SOC 2 automatically, which matters most to teams managing several overlapping standards at once rather than a single framework in isolation.
That breadth-first design shows up as a real tradeoff in reviews. Hyperproof is consistently described as less intuitive for first-time users, with a setup process that takes real time to work through, and its integration feature ("Hypersyncs") reportedly needs some trial and error to configure well. This reads more like a platform built for a compliance team already managing complexity than a lightweight first buy for a startup doing its first ISO 27701 push.
Key features:
- 160+ supported frameworks, one of the largest libraries in this comparison
- Shared control mapping across ISO 27001, ISO 27701, SOC 2, and GDPR
- Built-in Risk Register with third-party/vendor assessment integration
- Task-assignment and collaboration tooling for cross-team compliance work
Pros of Hyperproof
- Very broad framework coverage reduces the odds of hitting an unsupported standard later
- Genuine cross-framework control mapping, specifically called out for the ISO 27001/27701/SOC 2/GDPR overlap
- Strong risk-register and vendor-assessment tooling beyond core evidence collection
Cons of Hyperproof
- UI and initial setup are consistently described as less intuitive than other platforms on this list
- Integration configuration ("Hypersyncs") reportedly requires real trial and error
- Reporting and analytics flexibility described as limited by reviewers
- No public pricing; no dollar figures shown anywhere on its pricing page, only demo/proposal requests
Pricing: Not public. No tiers or figures shown; the pricing page routes to "Get a Demo" or "Request Proposal" only.
Best for: Larger or multi-framework organizations managing several overlapping standards through shared control mapping, not startups wanting a lighter, audit-bundled first experience.
11. ISMS.online
ISMS.online is the only vendor in this comparison that's actually built dedicated ISO 27701 product content — two separate pages specifically targeting "best ISO 27701 compliance software," which is more than any of the ten platforms above it have done.
It's also, honestly, the reason this article exists: neither of those two pages names a single competing vendor or includes a real comparison table. Both fold into a "why choose ISMS.online" pitch instead. That's a real gap in the market, and it's the gap this article is written to fill.
ISMS.online itself isn't narrowly ISO-focused, despite the name — it markets a broad 100+-framework platform, positioned as "one connected system, not three silos," covering ISO 27001, ISO 42001, SOC 2, GDPR, ISO 27701, NIS2, DORA, and more.
What it's genuinely good at, per its reviewers, is structured ISMS and PIMS documentation: one Capterra review specifically credits it with making "the annual ISO 27001 audit much less painful," and its built-in policy templates ("Headstart content") reduce the blank-page problem a lot of first-time implementers hit.
The honest downside shows up in the same review set. Value-for-money was the weakest sub-score in Capterra's breakdown (3.8 out of 5, against a 4.0–4.1 range on everything else), and the review sample there is small (8 reviews).
One reviewer stated directly that they "switched to Vanta when we realized how much better it was" — real evidence of losing a head-to-head comparison against a broader automation platform, from a company whose own marketing leans hard on being the ISO specialist.
Key features:
- Two dedicated ISO 27701-focused content pages, more purpose-built content than any other vendor here
- 100+ supported frameworks positioned as one connected system
- Built-in policy and documentation templates ("Headstart content")
- Bespoke, pay-for-what-you-use pricing model
Pros of ISMS.online
- Deepest ISO 27701-specific content and documentation structure of any vendor in this comparison
- Strong reviewer sentiment around audit-prep support specifically
- Broad framework coverage despite the ISO-focused name
Cons of ISMS.online
- Its own "best ISO 27701 software" pages are single-vendor advocacy with no real competitor comparison — the exact gap this article exists to close
- Weakest value-for-money sub-score in its Capterra review breakdown (3.8/5)
- Small review sample size on Capterra (8 reviews) limits how much confidence to put in the ratings
- At least one documented case of a customer switching to Vanta after a direct comparison
- Pricing is bespoke and quote-only, adding sales friction versus more self-serve competitors
Pricing: Not public. Bespoke, "pay only for what you use" model based on which frameworks and modules you select; requires a quote form or demo.
Best for: Organizations that want deep ISO 27001/27701 management-system documentation and audit-prep structure in one platform, more than fast, self-serve, integration-heavy automation.
How to Choose the Best ISO 27701 Software (Platforms Supporting ISO 27701 and ISO 27001)
This section covers how to choose ISO 27701 compliance software based on where you're actually starting from, not a generic checklist.
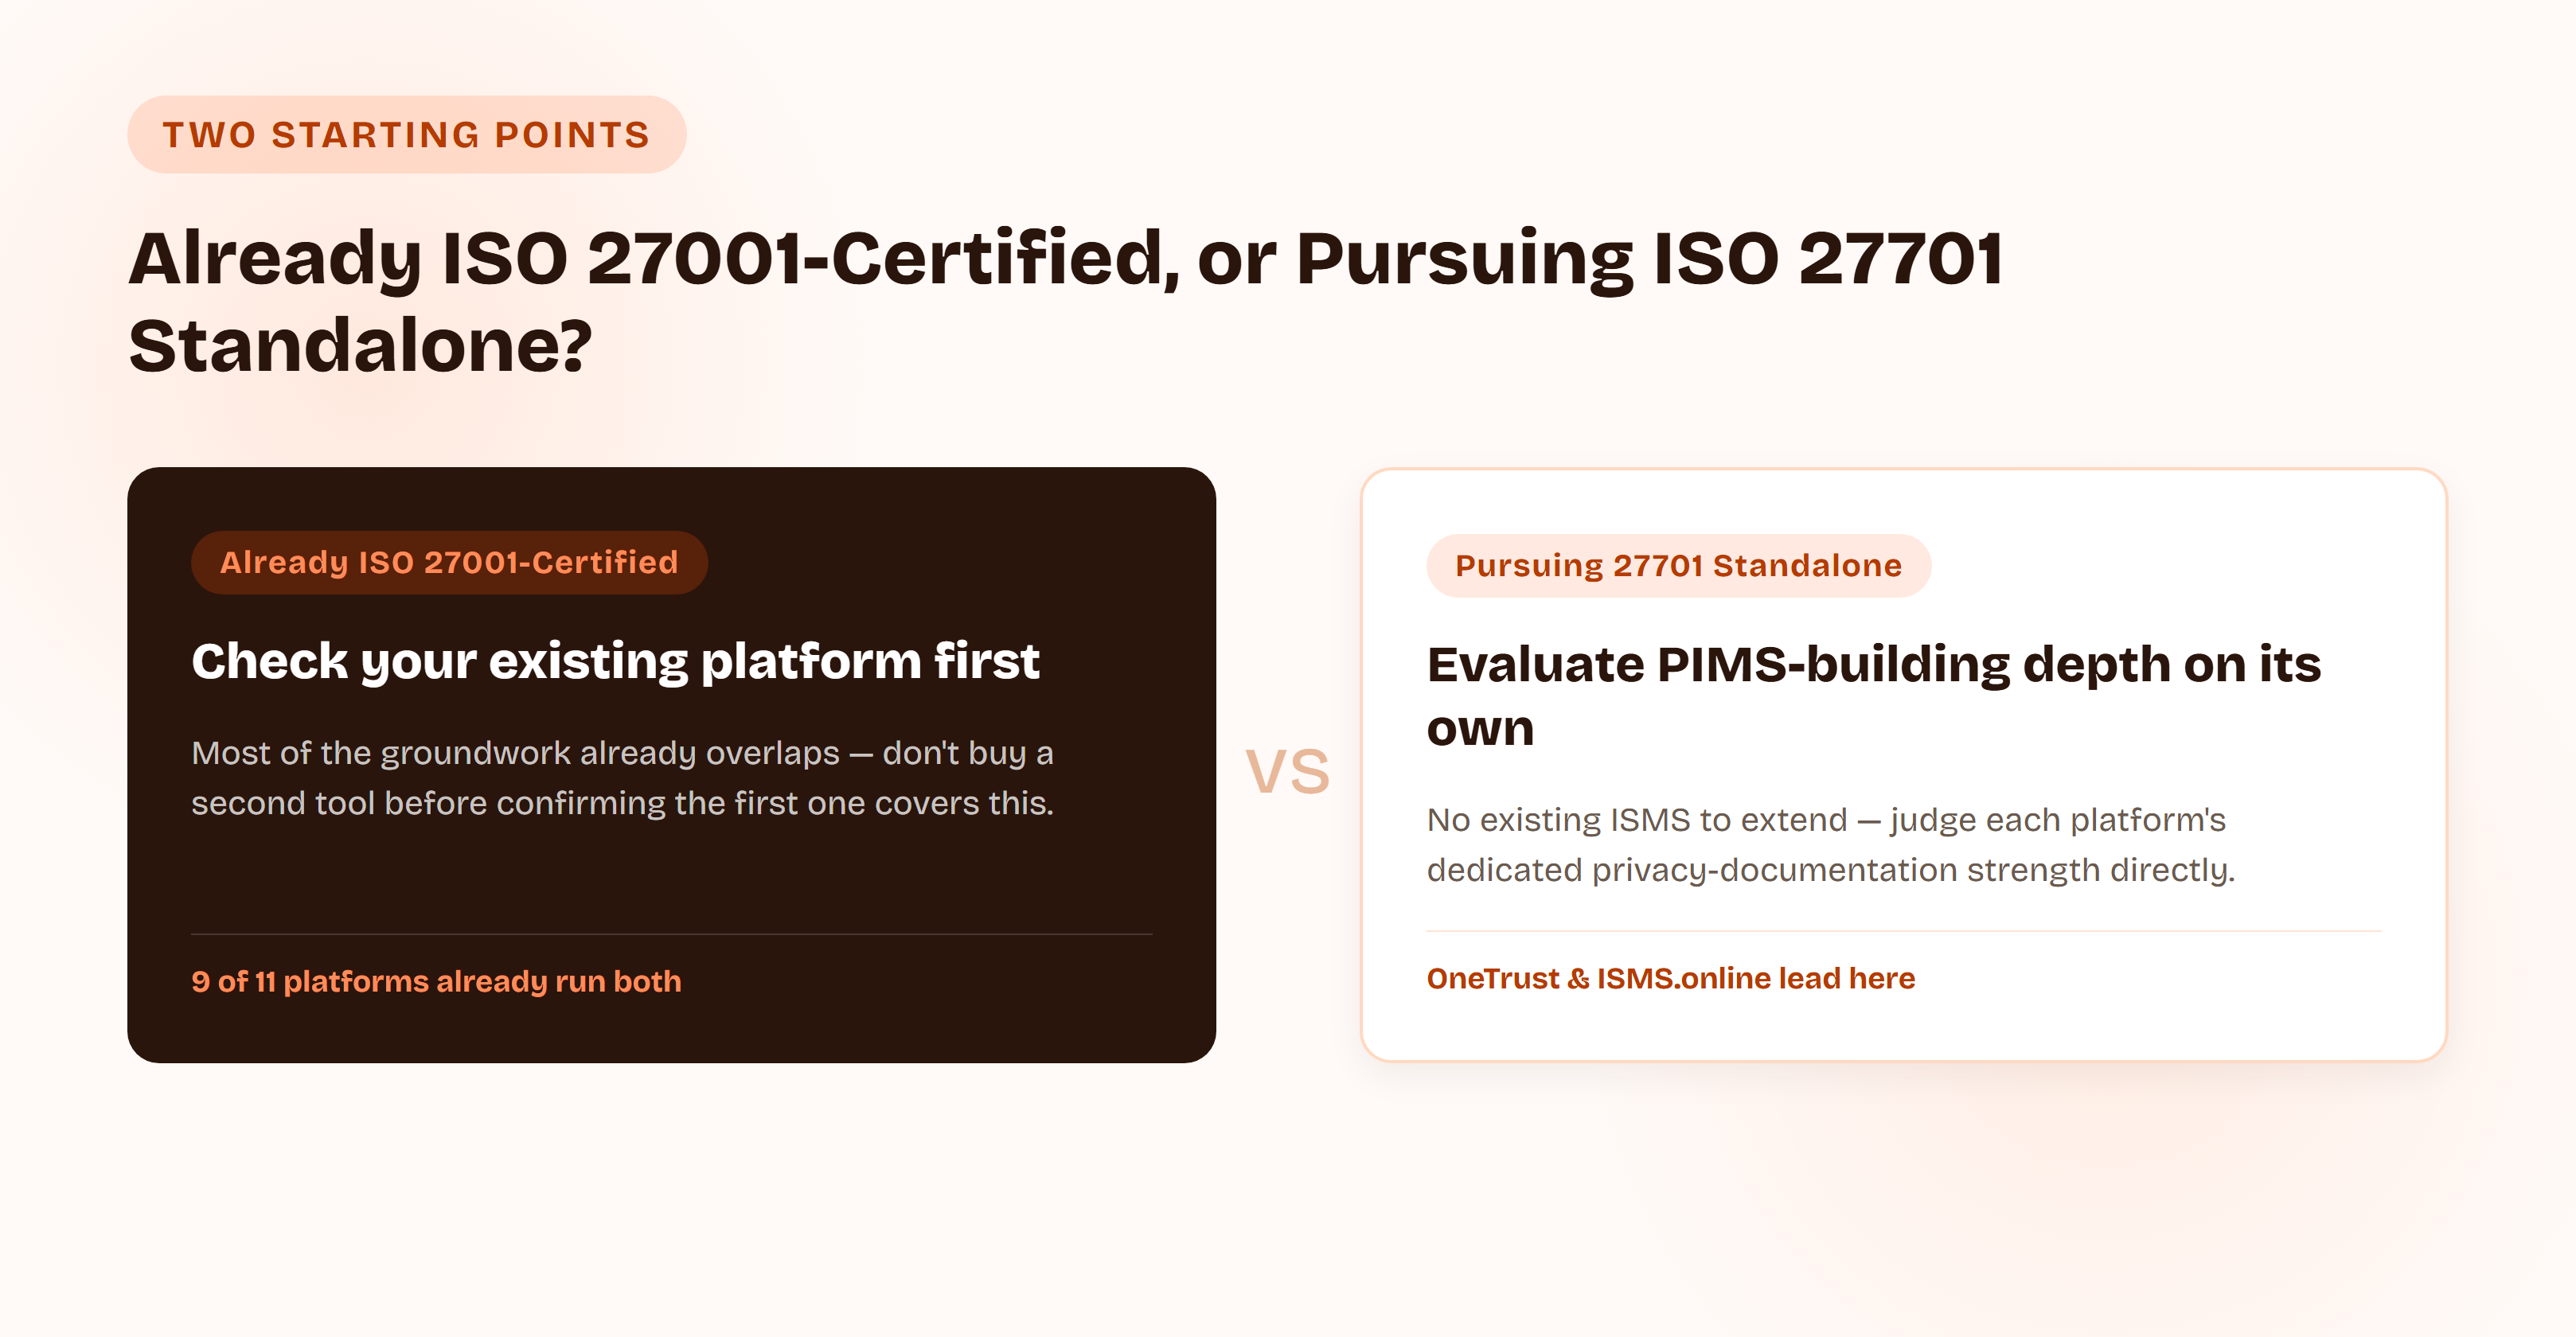
Already ISO 27001-Certified vs. Pursuing ISO 27701 Standalone Under the 2025 Edition
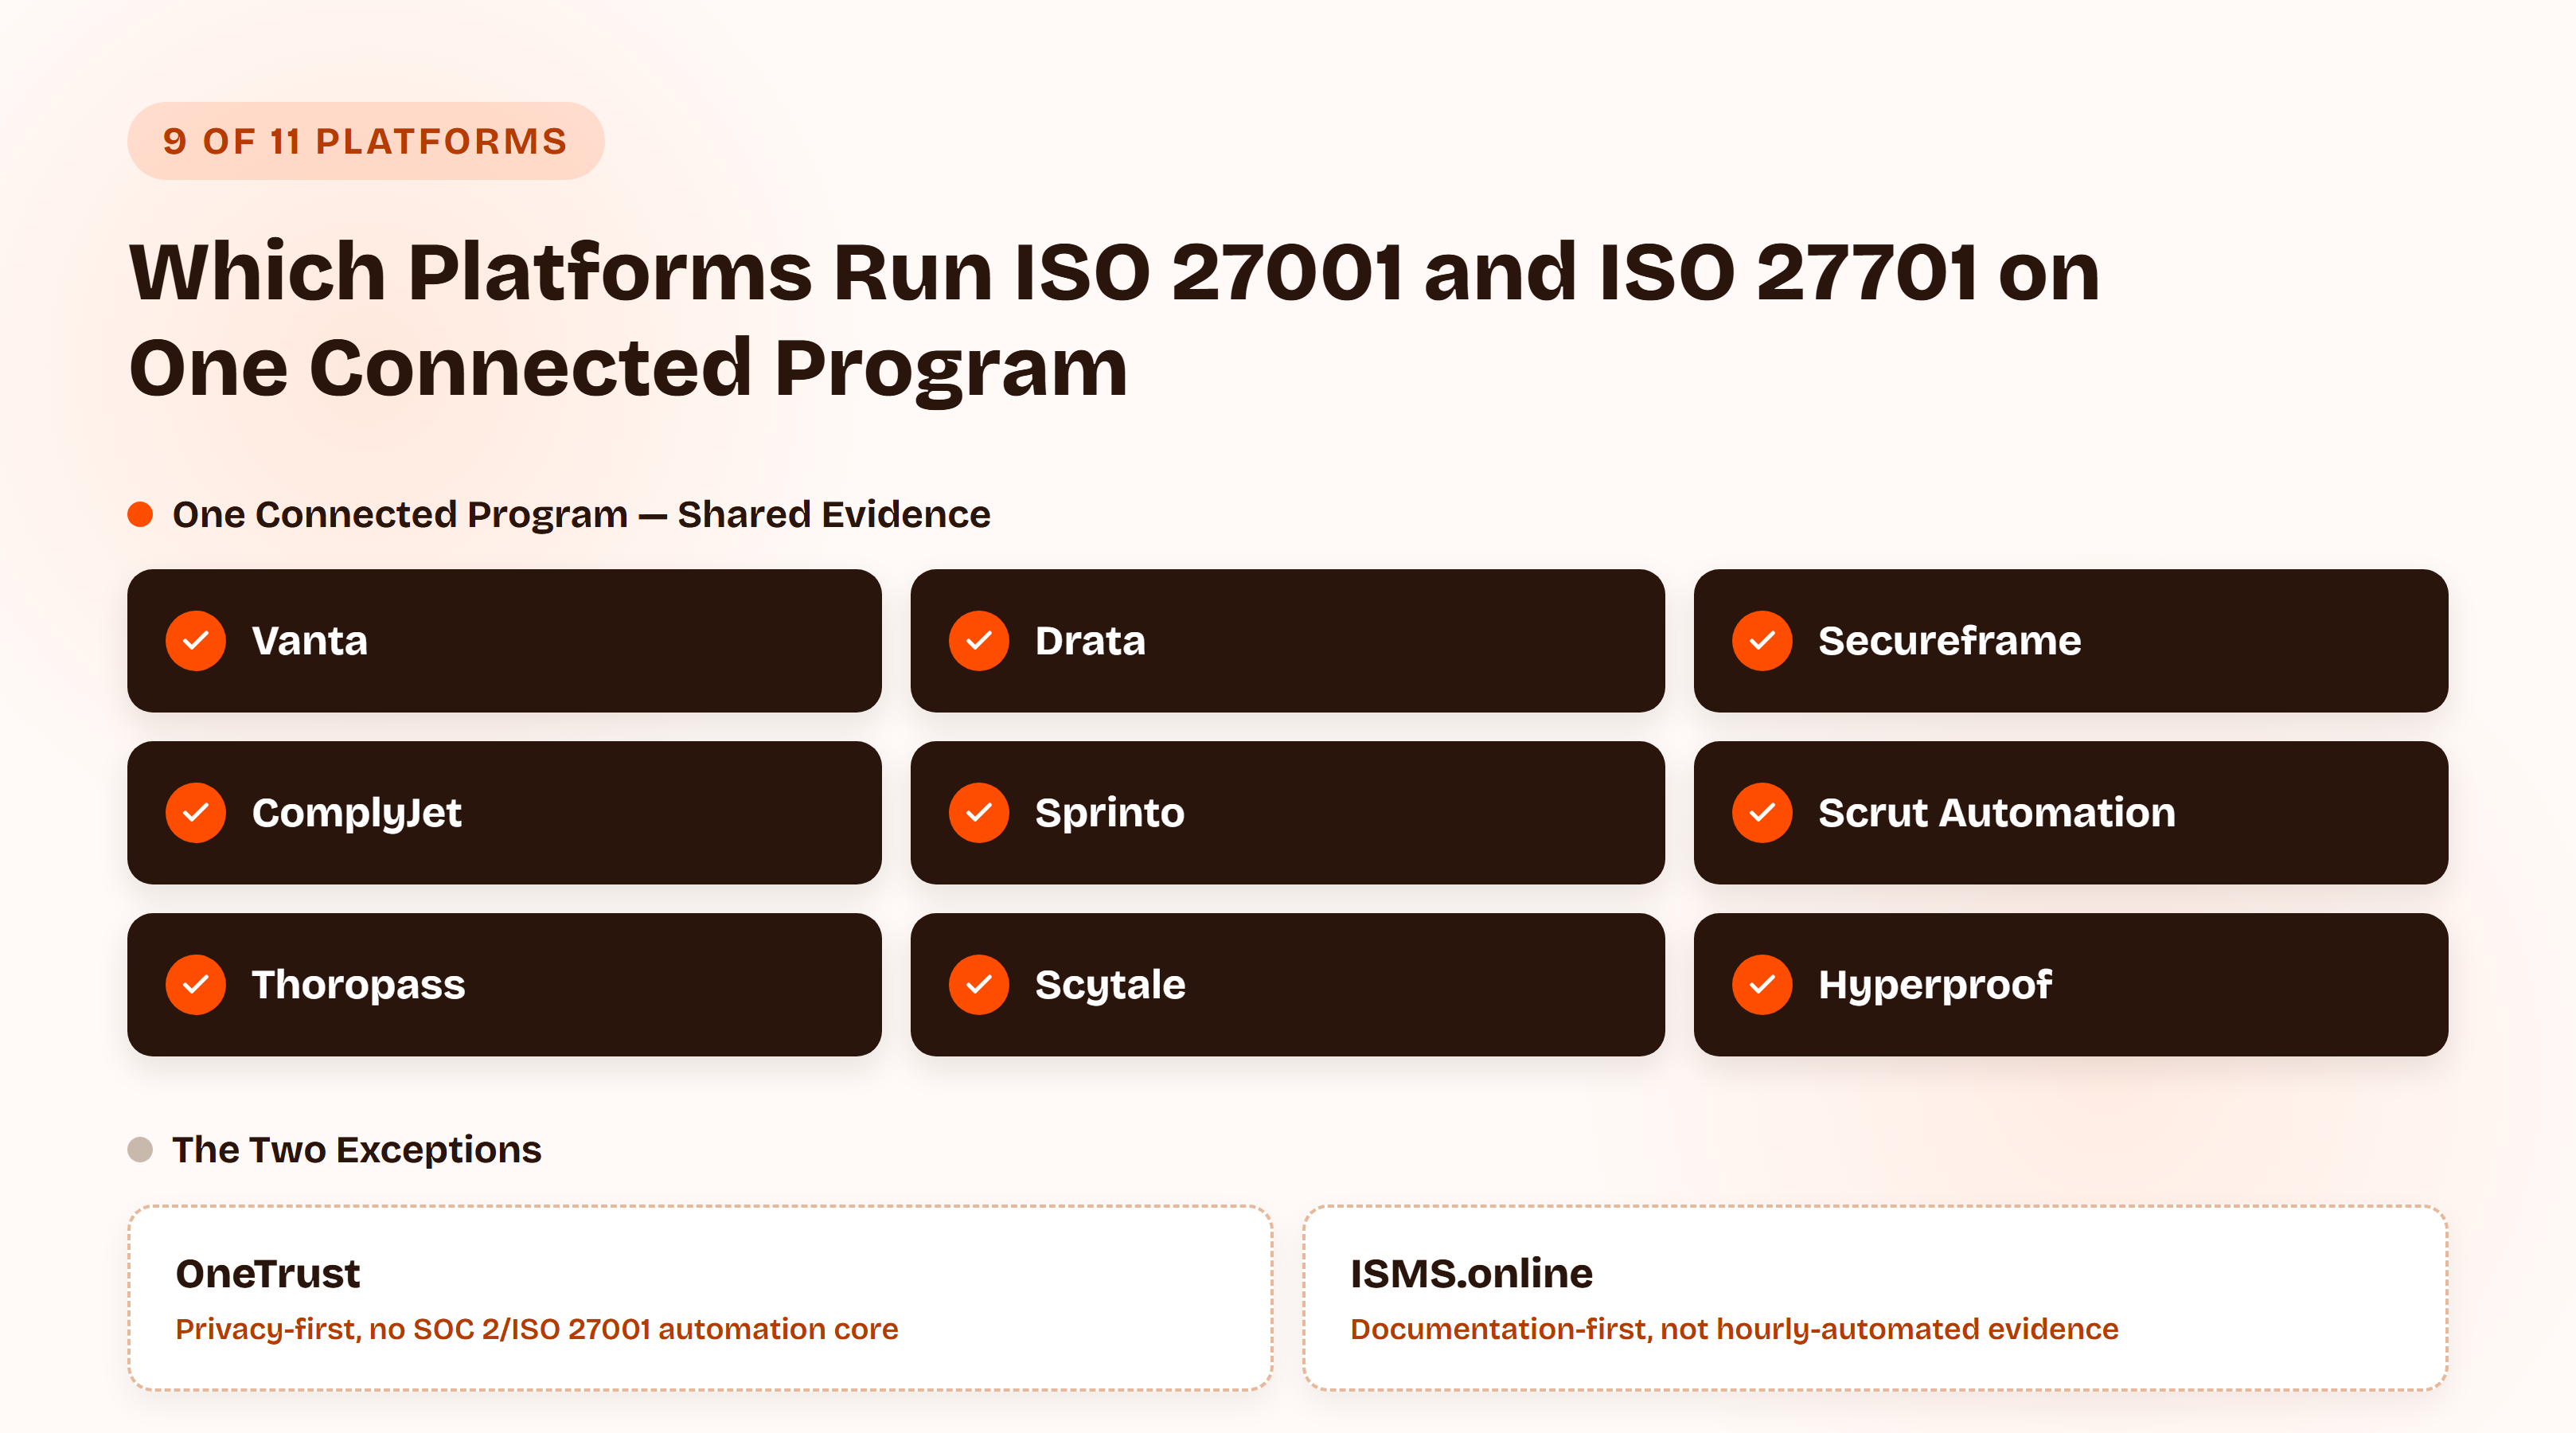
If you already hold ISO 27001, the honest first move is checking whether your existing platform supports ISO 27701 before shopping for a new one. Vanta, Drata, Secureframe, Sprinto, Scrut, Thoropass, Scytale, Hyperproof, and ComplyJet all run ISO 27001 and ISO 27701 on the same connected program.
That overlap is the whole point, and buying a second tool to manage a framework that shares most of its evidence with the first one you already have is usually the wrong call.
If you're pursuing ISO 27701 standalone under the 2025 edition, without an existing ISMS, the calculus shifts. You're not looking for "does this extend what I already have" — you're evaluating each platform's PIMS-building capability on its own terms, which is where OneTrust's and ISMS.online's dedicated privacy-documentation depth genuinely earns more weight than it would for a reader in the first group.
Do You Need Dedicated Privacy Tooling, or Is the Best ISO 27701 Software Just Framework-Level Coverage?
Most early-stage SaaS companies land in the PII processor role — you're handling your customers' end-user data, not making the underlying decisions about how it's used. For that reader, framework-level coverage (control mapping, evidence collection, the audit-readiness mechanics) is usually enough. You don't need OneTrust's deep DPIA/ROPA-specific tooling if your privacy program is still relatively simple.
If you're a PII controller — you directly own the relationship with the people whose data you're processing — or if your privacy program has real complexity (multiple sub-processors, cross-border transfers, active DPIAs), the calculus changes. That's when OneTrust's genuinely deeper tooling, or ISMS.online's structured documentation approach, starts to justify its added weight and cost.
Team Size, Budget, and the Best ISO 27701 Software for Your Stage
Nine of the eleven platforms in this comparison require a sales call before you see a number. That's not a criticism specific to any one vendor — it's simply the category norm, and it means your actual buying process will likely include a real negotiation regardless of which platform you pick. Go in with a sense of your framework count and headcount, since both variables move the quote significantly across every vendor here.
If pricing transparency itself is a deciding factor — not wanting to spend a sales cycle just to learn the number — ComplyJet is the one platform in this list with a publicly listed figure, with the caveat noted in its entry above about confirming ISO 27701's exact placement on that pricing.
That's ultimately how to choose ISO 27701 compliance software with confidence: start from what you already have and what you can actually verify, not from whichever page ranks first.
Platforms Supporting ISO 27701 and ISO 27001 on One Connected Program
This is worth answering directly, since it's the practical question underneath most of the decision above. Of the eleven platforms compared here, nine run ISO 27001 and ISO 27701 on one connected program with shared evidence: Vanta, Drata, Secureframe, Sprinto, Scrut Automation, Thoropass, Scytale, Hyperproof, and ComplyJet.
OneTrust is the exception in the other direction — it's privacy-first without a native SOC 2/ISO 27001 automation core, so pairing it with a separate security-compliance platform is the realistic path if you need both. ISMS.online sits in between: broad framework coverage in one system, but structured more around documentation and audit prep than the hourly automated evidence collection the SOC 2-native platforms are built around.
Pricing
Skip the sales-call-just-to-see-a-number step
ComplyJet is the one platform in this comparison with a publicly listed price. See exactly what $5,000–$8,000/year covers before you book anything.
FAQs
What Is ISO 27701 Compliance Software?
It's the platform layer that operationalizes a Privacy Information Management System — the controller/processor-specific extension ISO 27701 adds on top of an ISO 27001 ISMS. In practice, that means control mapping, evidence collection, and, for a subset of vendors, dedicated DPIA and ROPA tooling.
Is ISO 27701 Software Different from ISO 27001 Software?
Not as a separate product category. Every platform in this comparison sells ISO 27701 as a framework module inside the same multi-framework compliance-automation software it already sells for ISO 27001 and SOC 2, not as a standalone tool. The exception worth knowing is OneTrust, which is privacy-first and doesn't have a native SOC 2/ISO 27001 automation core the way the others do.
Do I Need ISO 27001 Before ISO 27701?
Not anymore. The 2025 revision made ISO 27701 certifiable on its own, without requiring ISO 27001 first. In practice, most SaaS companies still pursue both together, since the standards share structure and a lot of the same evidence — but the standalone path is real for organizations that want privacy certification specifically without taking on the full ISMS scope.
How Much Does ISO 27701 Certification Cost?
Vendor-cited estimates vary widely, roughly from $2,000 to $30,000 or more depending on organization size, scope, and whether an ISMS already exists. For the full cost breakdown and why the estimates disagree so much, see ComplyJet's ISO 27701 guide.
Does ISO 27701 Software Help with GDPR?
Yes, as supporting evidence, not a substitute. ISO 27701 includes an annex mapping its privacy controls to GDPR's requirements, so certification is meaningful evidence in a broader GDPR program. It doesn't replace the legal mechanics GDPR requires on its own — lawful basis, breach-notification timelines, data subject rights — which sit outside what any ISO certification covers.
Which Platforms Support Both ISO 27001 and ISO 27701?
Nine of the eleven platforms compared here run both on one connected program: Vanta, Drata, Secureframe, Sprinto, Scrut Automation, Thoropass, Scytale, Hyperproof, and ComplyJet. See the "Platforms Supporting ISO 27701 and ISO 27001" section above for the full breakdown, including the two exceptions.
Is the Best ISO 27701 Software Worth It for Small Teams?
If a customer or DPA review has started asking privacy-specific questions your ISO 27001 certificate doesn't answer, yes — the alternative is scrambling to build a PIMS manually once a deal is already stalled on it. If nobody's asked yet, it's reasonable to wait, especially if you're already running ISO 27001 on a platform that supports ISO 27701 as an easy add when the question does come up.
What Does the Best ISO 27701 Software Include?
At minimum: confirmed, current ISO 27701 framework support (not a glossary mention), evidence reuse with an existing ISO 27001 program if you have one, 2025-edition standalone-certification readiness, and pricing you can actually plan around. The deeper differentiator, if your privacy program has real complexity, is dedicated DPIA and ROPA tooling — which only a couple of platforms in this comparison genuinely have.
Final Thoughts on the Best ISO 27701 Software
There isn't a dedicated "ISO 27701 software" category to shop in, and pretending otherwise would have made this a worse, less useful article. What actually exists is a set of multi-framework compliance platforms — the same names already competing on SOC 2 and ISO 27001 — deciding how seriously to take this one privacy framework, with real differences in how deep that support actually goes once you check past the marketing page.
Nine of the eleven platforms here will run ISO 27701 on the same program as an existing ISO 27001 build. If you're already on one of them, that's usually your fastest, cheapest path — check what you have before you shop for something new.
If you're evaluating from scratch, weigh how much genuine privacy-specific depth you need against how much you're willing to pay for it, and don't take a vendor's "we support this framework" claim at face value without checking the actual page yourself, the way this ISO 27701 software comparison did.
Free Demo
See ComplyJet's ISO 27701 support in a real walkthrough
Flat, per-company pricing and a team that guides you through setup instead of leaving you alone with a dashboard.
Sources: Vendor ISO 27701 support verified directly against each platform's own site — Vanta's ISO 27701 compliance software page, Drata's frameworks page (lists ISO 27701 twice, "Extend ISO 27001 with a privacy information management system"), Secureframe, OneTrust's "ISO 27701: How OneTrust Helps", and Sprinto's public frameworks page.
Also verified: Scrut Automation, Thoropass's frameworks page (confirms ISO 27701 is not yet shown in the visible framework grid, only ISO 27001 under "ISO Certifications," consistent with its being a May 2025 addition), Scytale's frameworks page (lists ISO 27701 under Privacy), Hyperproof's frameworks page, and ISMS.online's ISO 27701 compliance software pages.
Pricing estimates for platforms without public pricing sourced to third-party deal-data aggregator Vendr where cited. Review sentiment and sub-scores sourced to G2 and Capterra listings for each respective vendor, checked directly rather than taken from a vendor's own review-quote selection.