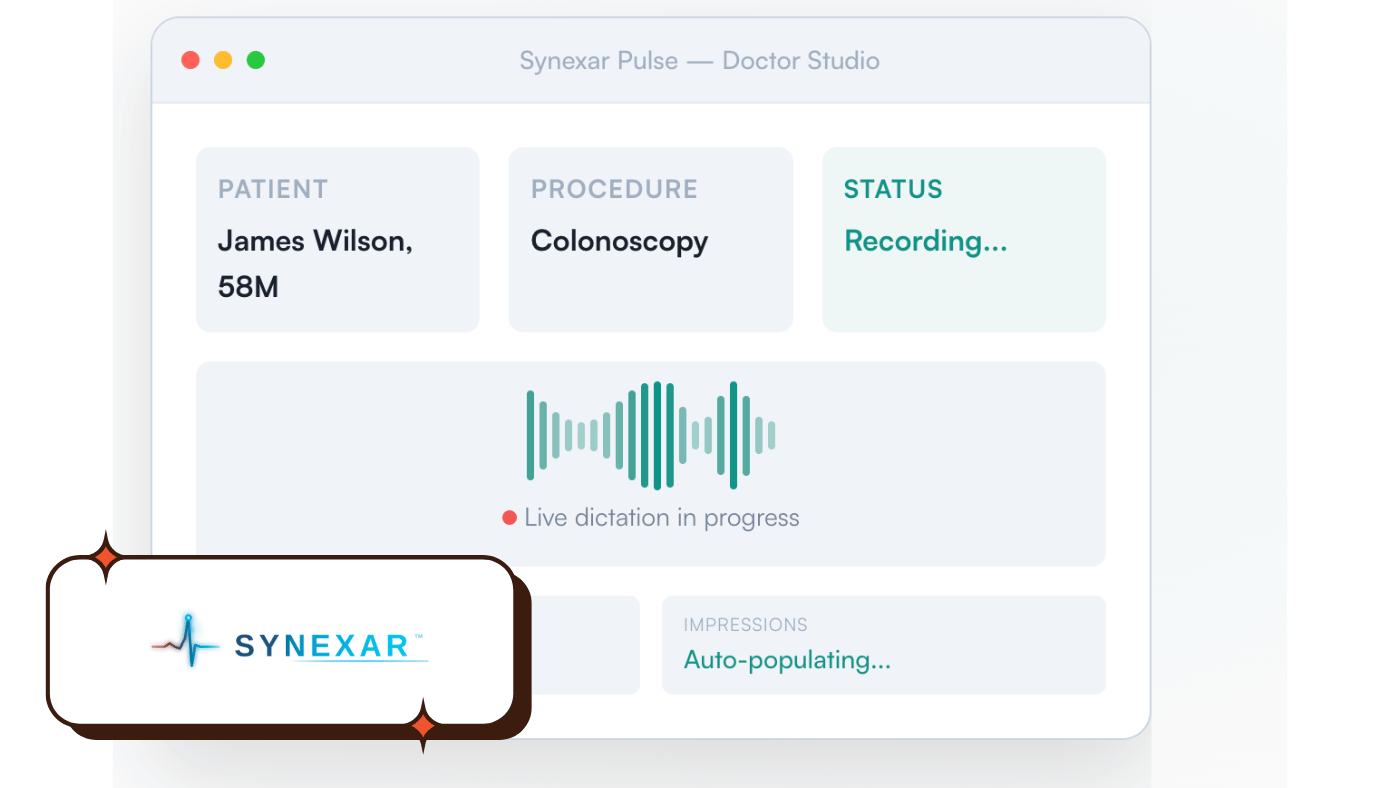
Forty-seven seconds. That's how long it takes Synexar AI's platform, Synexar Pulse, to turn a doctor's voice dictation during a GI endoscopy into a structured report with CPT and ICD-10 codes attached. It replaces documentation tools that have dominated the space for years, and it does it by sitting directly inside a hospital's workflow — listening to the procedure, touching the EHR, handling patient records the moment they're created.
That's also exactly why security couldn't wait. When Synexar's co-founder Raghuram Vadapally started scoping the company's first enterprise deals with hospital systems, the pattern was consistent: every procurement team asked for a SOC 2 report, and every legal team asked about HIPAA in the same breath. Not eventually — before they'd sign anything.
Two Frameworks, One Clock
Most startups treat compliance frameworks as a sequence: get SOC 2 first, add HIPAA later once there's budget and time. Synexar didn't have that luxury. Their customers are hospitals, clinics, and GI practices, and for a platform touching protected health information (PHI), a SOC 2 report alone doesn't answer the question a hospital's compliance officer is actually asking. SOC 2 proves the security controls hold up. HIPAA proves the PHI itself is handled the way federal law requires. Healthcare buyers want both, and they want to see them together.
So Synexar partnered with ComplyJet to run both audits in parallel rather than in sequence — on an Azure-native stack (Microsoft Azure for infrastructure, Microsoft Entra ID for identity, GitHub Enterprise for source control) that's common in healthcare but less common among early-stage startups, and that needed the same depth of integration support AWS or GCP customers get by default.
From Kickoff to Issued Reports
The SOC 2 Type 1 engagement kicked off in Q2 2026. Because a Type 1 report is a point-in-time assessment rather than an observation period, the audit could move straight to fieldwork once Synexar's controls were mapped — no waiting for months of evidence to accumulate. HIPAA ran on the same track, reusing the same policy set and evidence base wherever the two frameworks overlapped, so the team wasn't duplicating work across two parallel audits.
Within the same quarter, both reports were signed off: the SOC 2 Type 1 management assertion and the HIPAA report were approved for final issuance within days of each other. For a small compliance effort inside an early-stage AI startup, running two healthcare-grade frameworks to completion that quickly is a fast clock — and it's exactly the timeline Synexar needed, because their pipeline of hospital deals wasn't waiting.
What Getting There Actually Took
The reports didn't appear on their own. Over that stretch, Synexar's team:
- Connected Azure infrastructure and GitHub Enterprise for continuous, automated evidence collection instead of manual screenshots
- Generated security policies mapped across SOC 2 and HIPAA simultaneously using ComplyJet's policy wizard, so one policy update served both frameworks
- Rolled out employee security awareness training and policy acceptance across the team
- Worked through risk assessments and vendor management — the unglamorous but necessary groundwork auditors check for
Raghuram stayed hands-on with the process throughout, following up directly when something looked stalled and pushing for clarity on next steps rather than waiting passively for updates. That posture — treating compliance as a startup problem to be worked, not a checkbox to wait out — is a large part of why the timeline held.
What Raghuram Says
ComplyJet has become an indispensable part of our compliance workflow, helping us stay organized and audit-ready at all times... I honestly can't imagine going back to managing compliance without it.— Raghuram Vadapally, Managing Director & Head of Software Engineering at Synexar AI
On support specifically, he didn't hedge: "The support team at ComplyJet is, without question, the best I've experienced with any software vendor."
Already Moving to the Next Bar
A SOC 2 Type 1 report proves your controls are designed correctly at a single point in time. A Type 2 report proves they held up over months of actual operation — and it's the version larger enterprise and hospital-system buyers increasingly expect. Synexar isn't waiting to find that out the hard way: the team signed their SOC 2 Type 2 examination agreement in Q2 2026, and that observation period is running now, in parallel with new hospital conversations.
Why This Matters
Healthcare AI adoption is gated by trust, and trust in healthcare means compliance — not as a future milestone, but as a credential that has to already exist by the time a hospital's security review starts. Synexar didn't build that credential after signing customers; they built it into the first year of the company, running two frameworks on the same clock instead of stringing them together over two years.
For a platform sitting inside the highest-trust workflows in a hospital, that's not just smart sequencing. It's the difference between a deal that closes and one that stalls in security review.
Looking Ahead
SOC 2 Type 1 and HIPAA are issued. SOC 2 Type 2 is in its observation window. When Synexar's next hospital system asks for proof — and in healthcare, that question always comes — the answer keeps getting stronger.